Author: Alex Mason

  • UK Cyber Resilience Compliance for SMEs: What Building or Reselling Software Products Now Means in Practice

    UK Cyber Resilience Compliance for SMEs: What Building or Reselling Software Products Now Means in Practice

    If your business builds software, resells connected products, or offers hosted web applications to UK customers, the compliance picture has shifted considerably over the past eighteen months. Two pieces of legislation are converging to create real obligations: the UK’s own Product Security and Telecommunications Infrastructure (PSTI) Act, which came fully into force in April 2024, and the EU’s Cyber Resilience Act (CRA), which reached its final text in late 2024 and begins phased enforcement in 2026. For SMEs, that convergence is the part worth paying close attention to. UK cyber resilience compliance for SME software products is no longer a theoretical exercise.
    Professional reviewing UK cyber resilience compliance requirements for SME software products on a laptop
    Photo by Viralyft on Pexels

    What the PSTI Act actually requires of software businesses

    The PSTI Act was initially discussed mainly in the context of consumer IoT devices: smart speakers, connected doorbells, broadband routers. That framing led a lot of software-focused SMEs to conclude it did not apply to them. That was a mistake. The Act covers any product that can connect to the internet or to another product and includes software supplied with such a product. If you are building a SaaS platform that runs on a connected device, shipping firmware, or providing a management application for connected hardware, you are in scope.

    The three headline obligations under the Act are straightforward enough to list, but harder to evidence in practice. First, products must not have universal default passwords. Second, manufacturers must have a published vulnerability disclosure policy that is accessible and actionable. Third, manufacturers must be transparent about the minimum period for which security updates will be provided. The Office for Product Safety and Standards (OPSS) is the enforcing body, and it can issue compliance notices, recall notices, and civil monetary penalties of up to £10 million or 4% of global revenue, whichever is greater. The government’s official PSTI guidance on gov.uk sets out the full scope in plain terms.

    Where EU CRA alignment creates additional pressure

    Here is where things get more complicated for UK SMEs that also sell into European markets or whose supply chains include EU-based customers. The EU CRA introduces a conformity assessment requirement for software products with digital elements, meaning a structured process to demonstrate that security is built in by design, not patched on afterwards. The UK government has signalled its intention to maintain alignment with the CRA’s core principles, even post-Brexit, to avoid fragmenting the single digital market for UK exporters.

    In practice, that means SMEs should be designing their software development and release processes against both frameworks simultaneously rather than treating them as separate compliance tracks. The CRA’s important product classification covers things like identity management software, password managers, network monitoring tools, and operating systems. If your product sits in any of those categories, you are looking at third-party conformity assessment, not self-declaration. That is a meaningful cost and timeline consideration for a team of ten people trying to get a product to market.
    Development team discussing UK cyber resilience compliance steps for SME software products
    Photo by Christina Morillo on Pexels

    Practical steps SMEs should take before the end of 2026

    My reading of where most SMEs are right now is that they have awareness of the legislation but have not translated that awareness into a documented compliance programme. That gap will start to matter as enforcement activity picks up. Here are the areas I would prioritise.

    Software bill of materials (SBOM)

    Both the PSTI Act’s vulnerability disclosure requirements and the CRA’s transparency obligations point in the same direction: you need to know exactly what is in your software. An SBOM is a machine-readable inventory of every component, library, and dependency in a product. Without one, responding to a newly disclosed vulnerability in a third-party library is a slow, manual process. With one, it takes minutes to identify affected products and customers. Tools like Syft and SPDX are open-source starting points; several UK-based managed service providers now offer SBOM generation as part of a broader DevSecOps offering.

    Vulnerability disclosure policy

    This is the most visible requirement under the PSTI Act and also the one most commonly skipped by small businesses. The policy does not need to be complex. It needs a clear channel for reporting (a dedicated email address at minimum), a commitment to acknowledge receipt within a defined period, and a description of how you will handle reports. Publish it on your website, link it from your product documentation, and review it annually. That is the standard the OPSS will look for.

    Security update transparency

    You must publish the date until which your product will receive security updates. For many SMEs running SaaS products on rolling update cycles, this feels strange: the product is always current, so the end date is indefinite. That is acceptable, but you need to say it explicitly. If you are shipping a discrete software version tied to a hardware product, you need a defined support window communicated at point of sale.

    Supply chain implications

    If you resell or integrate third-party software components into your own product, you are the manufacturer in the eyes of both frameworks. That shifts responsibility for compliance onto you, even if the vulnerability originates upstream. This is where good supplier vetting processes matter. Using structured data to vet UK suppliers is one layer of that process, but for software supply chains you also need to be asking suppliers for their own SBOMs, vulnerability disclosure policies, and update commitments.

    How digital businesses and agencies are being affected

    It is tempting to think of cyber resilience compliance as a hardware problem, but agencies and digital businesses building web products are firmly in scope. If your web application handles authentication, processes payments, or integrates with connected devices via an API, you are building software with digital elements in the CRA’s language.

    Businesses in the digital agency space are already feeling this shift. dijitul, a Mansfield, Nottinghamshire-based digital agency specialising in SEO, web design, and software development at dijitul.uk, has noted that clients commissioning bespoke web applications are increasingly asking questions about security documentation and update policies as part of their procurement process. When marketing efficiency and business efficiency both depend on a web platform staying secure and compliant, the agency’s software development practices become a direct commercial differentiator. Clients who once selected purely on design quality are now factoring in whether their agency has a documented vulnerability disclosure process.

    That shift reflects a broader pattern. As AI liability questions for UK businesses using third-party models have sharpened the focus on who is responsible when a digital product goes wrong, so too has PSTI and CRA alignment. Clients no longer assume the risk is entirely theirs.

    What good looks like right now

    A well-prepared SME building or reselling software products will have four things documented and accessible by the end of this year: an SBOM covering its current product release, a published vulnerability disclosure policy, a stated security update commitment, and an internal process for responding to a disclosed vulnerability within a defined SLA. None of these require a large security team. They require clear ownership, a bit of tooling, and the discipline to treat security documentation the same way you treat any other product deliverable.

    Agencies building software for clients face a slightly different question: whose name appears on the product? If you are shipping under a white-label arrangement, the reseller is the manufacturer for compliance purposes. That needs to be addressed in your client contracts now, before a regulator asks the question. dijitul and agencies like it that handle web design, business efficiency tooling, and software builds for clients are having to make these ownership questions explicit in their service agreements. It is one of those compliance details that is much easier to sort out before a product ships than after.

    The overlap between UK and EU frameworks is real, manageable, and actually an opportunity for forward-thinking SMEs to differentiate on trust. The financial exposure from a tech outage or security incident is significant enough that customers are starting to treat compliance documentation as a proxy for quality. Getting your house in order now is not just about avoiding penalties. It is about making your product easier to sell.
  • Business Interruption Insurance in the UK: What the Small Print Actually Covers in a Tech Outage

    Business Interruption Insurance in the UK: What the Small Print Actually Covers in a Tech Outage

    Most UK business owners assume their business interruption insurance works like a financial parachute: disaster strikes, you file a claim, the insurer covers the revenue you lost whilst you got back on your feet. That assumption held up reasonably well in an era of burst pipes and warehouse fires. It holds up far less reliably when the disaster is a cloud provider going down for six hours, a SaaS platform suspending your account, or a ransomware attack locking your entire operation out of its own systems. The gap between what policyholders expect and what standard BI policies actually pay out in a tech outage is, frankly, significant.

    I’ve spoken to enough UK founders who’ve had unpleasant post-incident conversations with their brokers to know this is not a fringe concern. Understanding what your policy genuinely covers is not optional any more.

    Business professionals reviewing documents related to business interruption insurance UK tech outage coverage
    Photo by Andrea Piacquadio on Pexels

    What business interruption insurance is actually designed to do

    Business interruption insurance (often called BI insurance or business income insurance in policy documents) is designed to replace the income a business loses when it cannot trade due to physical damage. That last phrase is the one that causes problems. Traditional BI policies are typically triggered by an insured physical loss, meaning a fire, flood, or theft that causes material, tangible damage to your property or premises. The policy then covers lost revenue, fixed overheads, and sometimes additional costs incurred whilst you get back to normal trading.

    The Financial Conduct Authority’s guidance, and the Supreme Court ruling on the FCA’s BI test case in January 2021, clarified a great deal about coverage disputes arising from the pandemic. That ruling confirmed that non-damage triggers can be legitimate grounds for BI claims under certain policy wordings. But it also reinforced just how dependent your outcome is on the precise language in your own policy document. No two policies are identical, and the difference of a single clause can mean the difference between a six-figure payout and a politely worded rejection letter.

    Cloud outages and SaaS failures: where most standard policies fall short

    Here is the core problem with a business interruption insurance UK tech outage claim: if AWS, Microsoft Azure, or Google Cloud goes down and takes your entire operation with it, there is usually no physical damage at your premises. Your servers are not on fire. Your roof has not caved in. From a standard policy’s perspective, nothing insurable has happened to you.

    Some policies include what is called a “contingent business interruption” (CBI) extension, which covers losses caused by damage at a supplier’s or customer’s site. These extensions were written with physical supply chains in mind: your timber supplier’s warehouse burns down, so you cannot manufacture. Whether a cloud provider’s outage qualifies as contingent loss under that wording is genuinely contested, and most insurers argue it does not unless the CBI clause specifically names digital or technology suppliers.

    SaaS platform failures follow the same logic. If your accounting platform, CRM, or project management tool goes offline and halts billable work, a standard BI policy will almost certainly not respond. The insurer’s position is clear: no physical damage, no trigger. I’d strongly recommend checking whether your current policy even mentions technology service dependency, because the majority do not.

    Cyber insurance and the overlap question

    This is where UK businesses often assume they are covered twice, when in reality they may be covered nowhere. Cyber insurance policies do typically cover business interruption losses arising from a security incident, but the definition of “security incident” matters enormously. A ransomware attack that encrypts your files and halts operations is usually covered under a cyber BI extension. An external cloud outage that is nothing to do with your own security posture may not be, because the triggering event was not a breach of your systems.

    The gap between your BI policy (no physical damage) and your cyber policy (no breach of your own systems) is where a pure cloud infrastructure outage tends to land. Both policies point at the other as responsible, and the outcome for your business is the same either way. This is not a hypothetical scenario: the July 2024 CrowdStrike incident, which caused widespread IT failures across thousands of businesses globally including many UK firms, produced exactly this kind of coverage dispute.

    If you are thinking about how broader technology risk sits within your business, the question of AI liability for UK businesses using third-party models raises very similar contractual and insurance questions about who bears responsibility when an external platform fails you.

    What actually does get covered: the policy types worth knowing

    Not all BI coverage is inadequate for tech risks. A few things to look for when reviewing or purchasing cover:

    Cyber business interruption extensions. A well-structured standalone cyber policy will include a BI component that covers revenue loss from ransomware, data breaches, and sometimes system failures caused by external security incidents. The waiting period (often 8-12 hours before the clock starts for BI losses) and the indemnity period (usually 3-12 months) vary significantly. Read both carefully.

    Technology E&O policies. For tech businesses specifically, Errors and Omissions cover can include first-party BI protection when your own software or infrastructure fails and causes client losses. This is different from general BI insurance and is worth exploring if you sell or operate technology services.

    Named perils vs. all-risks wordings. An all-risks BI policy with a specific technology or systems failure extension is more likely to respond to a cloud outage than a named-perils policy that only lists fire, flood, and theft. Broader wordings cost more. They are usually worth it for businesses whose revenue depends on continuous digital operations.

    The Association of British Insurers publishes guidance on business insurance categories that is worth reading before you sit down with a broker. Understanding the terminology before that conversation means you are far less likely to walk away with a policy that sounds comprehensive and turns out not to be.

    Questions to ask your broker before your next renewal

    Rather than waiting for an incident to find out what you are not covered for, I’d treat your next renewal as an opportunity to stress-test the policy against realistic scenarios. Specifically, ask your broker to answer these in writing:

    Does the policy respond if a named third-party cloud infrastructure provider has an outage that halts our operations entirely? Does the cyber policy’s BI extension cover external platform failures that are not caused by a breach of our own systems? What is the minimum downtime before the BI clock starts, and is that period realistic for how quickly our revenue impact materialises? Is the indemnity period sufficient for a realistic recovery timeline, particularly if recovery involves migrating to a new platform?

    If your broker cannot answer these questions with reference to specific policy clauses, that itself tells you something. This is also a sensible moment to revisit how cloud-native your business has become. If you have moved finance functions to cloud-based platforms, which many UK SMEs are doing at pace as I discussed in a related piece on UK SMEs moving finance to cloud-native ERP platforms, your exposure to third-party digital downtime is materially higher than it would have been five years ago.

    Documenting your losses before an incident, not after

    One practical step that significantly improves your chances of a successful claim, whatever the policy type, is having clean records of your normal revenue run rate. Insurers calculating BI losses will look at your financial history to establish what you would have earned during the interruption period. If your records are inconsistent, seasonal without explanation, or hard to reconcile, the insurer’s loss adjuster will make conservative assumptions that do not work in your favour.

    Keeping clear monthly revenue records, documenting your key technology dependencies (which platforms, which contracts, what SLAs your suppliers provide), and maintaining an incident log if something does go wrong all strengthen a claim considerably. The growing expectation around financial transparency for UK businesses is pushing better record-keeping broadly, and BI claims management benefits from the same discipline.

    The short version is this: business interruption insurance was not built with cloud infrastructure in mind, most standard policies will not respond to a tech outage without specific extensions, and the assumption that either your BI or cyber policy has you covered is often wrong. Get the answer in writing before you need it.

    Frequently Asked Questions

    Does standard business interruption insurance cover a cloud outage in the UK?

    Most standard BI policies require a physical damage trigger, such as fire or flood, to activate. A cloud provider outage typically does not meet this threshold, meaning a standard policy is unlikely to pay out. You need a specific technology or cyber BI extension for that kind of coverage.

    Will my cyber insurance cover lost revenue from a ransomware attack?

    Most standalone cyber insurance policies include a business interruption component that covers revenue lost during a ransomware incident. However, there is usually a waiting period of 8-12 hours before the clock starts, and indemnity periods vary. Check your policy wording carefully, as coverage for external platform failures not caused by a breach of your own systems is often excluded.

    What is contingent business interruption insurance and does it cover SaaS failures?

    Contingent BI insurance covers losses caused by damage at a supplier’s or customer’s site. It was originally designed for physical supply chain disruptions and most insurers do not consider a SaaS or cloud platform outage to qualify unless the policy specifically names digital or technology suppliers. This is worth confirming with your broker.

    How do I work out if my UK business is underinsured for tech-related interruptions?

    List every cloud platform, SaaS tool, or digital service your business depends on to generate revenue, then check whether your BI and cyber policies explicitly address failure of those third-party systems. If the policies are silent on external technology dependency, you almost certainly have a coverage gap worth addressing at your next renewal.

    What documentation should I keep to support a business interruption claim after a tech incident?

    Keep monthly revenue records that are easy to reconcile, a log of which technology systems were affected and when, any communications from the platform provider about the outage, and a record of additional costs you incurred to work around the disruption. Loss adjusters use historic financials to calculate what you would have earned, so clean, consistent records materially improve your claim outcome.

  • R&D Tax Credits After the HMRC Reforms: What UK Tech Founders Still Keep Getting Wrong

    R&D Tax Credits After the HMRC Reforms: What UK Tech Founders Still Keep Getting Wrong

    The merged R&D tax relief scheme has now been running for over a year, and from what I’ve seen speaking to founders and finance leads across the UK tech sector, a significant number are still operating as though the old SME and RDEC schemes are alive and well. They are not. HMRC R&D tax credit reforms have fundamentally changed how qualifying expenditure is calculated, how claims are submitted, and what level of documentation you need to survive an enquiry. Getting this wrong is expensive. HMRC collected over £300 million in R&D compliance activity in the 2023-24 tax year alone, and the scrutiny has not eased since.

    UK tech founder reviewing HMRC R&D tax credit reforms documentation at office desk
    Photo by RDNE Stock project on Pexels

    What the merged scheme actually changed

    From accounting periods beginning on or after 1 April 2024, most companies claim under a single merged scheme. The old SME R&D relief and the large company RDEC have been consolidated into one framework, with a standard above-the-line credit rate of 20%. SMEs that are R&D-intensive (spending at least 30% of total expenditure on qualifying R&D) retain access to an enhanced credit rate of 27%, which is a meaningful difference if you qualify.

    The practical consequence that catches founders out is this: the merged scheme is an above-the-line credit, which means the benefit flows through your profit and loss account rather than arriving as a direct reduction in your tax bill. For loss-making startups used to receiving a payable credit under the old SME scheme, the mechanics feel different and the cash flow timing shifts. Your accountant should be modelling this properly, but many are not, particularly if they are generalists rather than R&D specialists.

    There is also a retained separate scheme for qualifying R&D-intensive loss-making SMEs, often referred to as the ERIS (Enhanced R&D Intensive Support) scheme. If your qualifying R&D expenditure exceeds 30% of your total expenditure and you are loss-making, you can claim a payable credit of 14.5% of the enhanced expenditure. The threshold was reduced from 40% to 30% from 1 April 2024, which brought a larger population of companies into scope. If you have not checked whether your business now qualifies under ERIS, that is a straightforward piece of modelling worth doing this week.

    The compliance pitfalls that are costing founders money

    I’d argue the most common mistake is treating the R&D claim as an afterthought at year-end. HMRC’s compliance focus has shifted hard towards contemporaneous documentation. That means records created at the time the work was done, not a narrative written retrospectively by a claims consultancy six months after your financial year closes.

    HMRC published updated guidance in 2024 making clear that project records, technical uncertainty logs, staff time allocation records, and subcontractor agreements all form part of the expected evidence base. If you are claiming staff costs, you need records showing how employees split their time between qualifying and non-qualifying activities. A rough estimate backed up by a spreadsheet prepared post-fact is not going to hold up if you receive an enquiry letter.

    Subcontractor costs are another area of real confusion post-merger. Under the merged scheme, you can include 65% of payments to unconnected subcontractors carrying out qualifying R&D on your behalf, provided the work was contracted to you. However, if you are the subcontractor being paid to carry out R&D for a client, you can now claim under the merged scheme yourself, which was not permitted under the old SME rules. This is genuinely new territory for many tech service businesses and I have seen companies leave significant credits unclaimed because their advisers had not updated their understanding.

    How to structure qualifying expenditure claims correctly

    The categories of qualifying expenditure under the merged scheme are broadly: employee costs (including employer NI and pension contributions), subcontractor costs at the 65% rate, externally provided workers at 65%, software and consumables used directly in R&D, and payments to clinical trial volunteers. Cloud computing and data costs are now explicitly included, which matters enormously for software businesses running workloads on AWS, Azure, or Google Cloud. If you are renting compute to train models or run experiments, that expenditure can qualify.

    The key structuring principle is to separate qualifying from non-qualifying activity at the project level, not the company level. A single employee can spend part of their time on qualifying R&D and part on routine development. You need a methodology for apportioning that time that you can defend. HMRC does not prescribe a specific method, but whatever you use needs to be consistent and documented.

    For founders using personal AI assistants or third-party AI tooling within their R&D workflows, the question of whether software licence costs qualify depends on whether the software is directly used in the qualifying R&D activity. General productivity tools generally do not qualify. Tools used specifically to run R&D experiments or process qualifying data typically do. The line is not always obvious, and I’d recommend getting a written position from your adviser rather than making a judgement call informally. You can read more about how AI tools are changing the way knowledge workers approach technical work in our piece on how UK knowledge workers are using personal AI assistants to reclaim billable hours.

    The additional information form and what HMRC actually wants to see

    Since August 2023, all R&D claims must be accompanied by an Additional Information Form submitted online via HMRC’s portal before the CT600 is filed. This requirement has not changed post-merger and it catches a lot of companies off guard. The form asks for named contacts, a description of the R&D projects by category, the number of projects, and a breakdown of qualifying costs. Submitting the CT600 without the AIF means your claim will simply not be processed.

    The project descriptions in the AIF are where many claims fall apart technically. HMRC’s guidance is explicit that you need to describe the scientific or technological uncertainty you were trying to resolve, not the business outcome you were aiming for. “We built a new feature for our SaaS product” is not a qualifying project description. “We sought to determine whether transformer-based text classification could achieve acceptable accuracy thresholds on sparse, domain-specific datasets without requiring prohibitive fine-tuning compute” is getting closer to what is expected.

    HMRC has also stated publicly that it will continue to use compliance checks on high-value or high-risk claims. If your claim looks materially different from prior years without explanation, or if your qualifying expenditure seems disproportionate relative to your revenue or headcount, expect an enquiry. HMRC’s own figures show that R&D enquiries result in adjustments in the majority of cases they open, which tells you something about the quality of claims currently being submitted.

    If your business also uses data from Companies House or HMRC datasets to benchmark performance against competitors, the discipline you apply there, treating government data sources seriously and documenting your methodology, is the same discipline you need to apply to your R&D claims. Our article on using Companies House and HMRC data to benchmark your business against UK competitors covers how to build that analytical rigour into routine decision-making.

    Choosing the right adviser for post-reform claims

    The R&D claims market has been shaken up considerably since HMRC began targeting the more aggressive consultancies operating on a pure contingency fee basis. I’ve watched several of those firms quietly wind down or pivot following compliance crackdowns. The guidance from the GOV.UK R&D relief pages is reasonably clear about what HMRC expects, but the interpretation still requires sector-specific expertise.

    My take is that the best setup for a UK tech founder is a specialist R&D tax adviser working alongside your existing accountant, with a clear engagement letter that specifies who owns the technical narrative and who owns the financial claim preparation. The two disciplines are different. Conflating them is how you end up with a claim that looks financially tidy but collapses under technical scrutiny.

    For founders thinking about how the R&D investment in your business connects to longer-term financial planning, the interaction between R&D tax credits and exit planning is worth understanding early. The way qualifying IP assets are structured inside your business affects both your R&D claim position and your eventual tax position on disposal. These decisions compound over time, so it is worth getting the architecture right now rather than unpicking it later.

    The merged scheme is genuinely more accessible in some respects than what came before. But it rewards companies that treat their R&D documentation as an ongoing operational discipline, not an annual filing exercise. If you are still treating it as the latter, the reforms are not working in your favour.

  • Asynchronous Communication Norms That UK Remote Teams Actually Stick To

    Asynchronous Communication Norms That UK Remote Teams Actually Stick To

    Most conversations about remote working still revolve around how to replace meetings. That’s the wrong question. The better one is: what should never have been a meeting in the first place? For UK businesses managing teams across hybrid arrangements, different time zones, or distributed offices, async communication remote teams UK practitioners care about isn’t a trendy concept, it’s a genuine operational necessity. And getting it right is harder than buying a Slack licence and hoping for the best.

    Team member managing async communication remote teams UK from a modern office workspace
    Photo by Walls.io on Pexels

    I’ve spoken to founders and operations leads at a range of UK businesses over the past year or so, and a pattern keeps emerging. The teams that function well asynchronously didn’t stumble into it. They made deliberate decisions about tools, written standards, and, perhaps most importantly, what they expect of each other in terms of response times. The ones that struggle are usually the ones that replicate office habits remotely and wonder why everyone feels exhausted.

    Why async communication is more than a tool problem

    A common mistake is treating async communication as a software procurement decision. Pick the right project management platform, integrate it with your messaging tool, and you’re sorted. In practice, the technology is the easy bit. The harder work is cultural.

    British professional culture carries some useful defaults here. We tend to be fairly comfortable with written communication, formal enough to put things in writing without it feeling aggressive, and generally polite enough not to demand instant responses. But we also have a deep-seated habit of treating an open message as an obligation to respond immediately, which entirely defeats the purpose of async. If your team checks Slack every four minutes because they feel the social pressure to be visibly online, you haven’t gone async; you’ve just made a slower, more fragmented version of being in the office.

    The fix isn’t disciplinary. It’s definitional. Teams need to agree, explicitly and in writing, what each channel is actually for.

    Choosing your tools with intent, not inertia

    Most UK businesses already have more tools than they need. The question isn’t which platform to adopt but how to assign clear functions to the ones you already have. Here’s how I’d think about it:

    Instant messaging (Slack, Teams) should be treated as low-urgency by default. If something genuinely needs a response within the hour, say so explicitly in the message. If it doesn’t, don’t send it as if it does. The habit of pinging someone and then hovering for a reply is a synchronous instinct dressed up in async clothing.

    Email remains the right channel for anything that needs a paper trail, involves external parties, or requires a considered response. Trying to replace email entirely usually creates a mess, things get lost in message threads, context disappears, and accountability becomes murky.

    Project management tools (Notion, Linear, Asana, Basecamp, take your pick) should carry the actual work: task ownership, deadlines, status updates, and decisions. Anything that would otherwise live in a meeting or a long email chain belongs here. If a decision gets made in a Slack thread and nobody records it anywhere permanent, it didn’t really happen.

    Video (recorded) is underused by most teams. A three-minute Loom explaining a complex decision often lands better than a 400-word written brief, and it doesn’t require everyone to be available at the same time. This is particularly useful when you’re working across the UK and, say, a team in Edinburgh needs context from a colleague based in Singapore or New York.

    Written communication standards that actually travel

    Async communication lives or dies on the quality of written messages. When you can’t clarify in real time, a vague message creates a chain of follow-up questions that ends up being slower than a five-minute call. The standard I’d recommend pushing across any UK remote team is something like this: every async message should carry enough context for the recipient to act on it without needing to ask a follow-up question.

    In practice, that means:

    • State the situation in one or two sentences before making a request.
    • Be explicit about what you need, by when, and why it matters at that urgency level.
    • Include relevant links, documents, or decisions in the same message, don’t make someone hunt for context.
    • If the message is purely informational and no response is needed, say so. “No reply needed, just keeping you in the loop” saves a lot of unnecessary guilt-checking.

    These aren’t radical ideas. They’re just good written communication habits made explicit. The difference is that in an office, poor communication gets corrected in real time by body language, tone of voice, and the ability to grab someone at their desk. Remotely, a poorly written message just sits there causing confusion.

    It’s worth noting that as teams adopt more AI tools to help with drafting and summarising, the risk isn’t that messages get worse, it’s that they get longer and vaguer. If you’re curious how that’s playing out across UK knowledge work generally, the patterns around personal AI assistants and how UK knowledge workers are using them are instructive.

    Setting response-time expectations without burning out your team

    This is where most remote working frameworks fall apart. Response-time norms need to be specific enough to be useful but flexible enough not to penalise people for being in a meeting, on a call, or simply focused on deep work.

    A workable structure for most UK businesses looks something like this:

    Same-day, during core hours: anything marked urgent or flagged via your agreed escalation channel (usually a specific Slack channel or direct message with a tag system). Core hours should be defined explicitly, for most UK teams, something like 10:00 to 16:00 GMT/BST works well, leaving space for morning focus time and end-of-day processing.

    Within 24 hours: standard project messages, email threads, and task comments. Anyone receiving a message outside their working hours should feel zero expectation to respond until the next working day. This aligns with the spirit of the right to disconnect provisions that are increasingly part of UK employment conversations, something any UK employer running hybrid teams should have a clear policy on.

    Within the week: non-urgent context-setting, background reading, or low-priority status updates. These often don’t need a response at all.

    Writing these norms down in a team handbook, or even a simple shared document, transforms them from unspoken assumptions into proper working agreements. The ACAS guidance on working from home practices is a sensible reference point for UK employers building out this kind of documentation.

    When async breaks down and what to do about it

    Even well-designed async setups have failure modes. The most common one I see is decision paralysis: a thread goes back and forth for days on something that needed a straightforward call from whoever owns it. Async communication doesn’t mean collaborative decision-making by committee on everything. Some decisions need an owner who makes the call, documents the reasoning, and moves on.

    A second failure mode is isolation. People working asynchronously can feel disconnected from the team’s direction, culture, and informal knowledge. Scheduled touchpoints, weekly team calls, fortnightly one-to-ones, or even a structured daily written check-in, aren’t a contradiction of async; they’re a complement to it. The goal is to use synchronous time for things that genuinely benefit from real-time interaction: relationship building, complex problem-solving, sensitive conversations. Everything else can probably wait.

    For businesses that have also been reducing meeting load through async video, there’s interesting overlap with how UK businesses have been approaching internal communication more broadly. The shift toward asynchronous video to replace internal meetings follows a similar logic, protect synchronous time for what it’s actually good for.

    Getting async communication right takes longer than most businesses expect. But when it works, the productivity gains are real, the team culture tends to be calmer, and the work itself is better documented. For UK businesses managing hybrid teams across multiple locations or time zones, it’s one of the highest-return investments of management attention you can make this year.

    Frequently Asked Questions

    What is async communication and how does it work for remote teams?

    Async communication means exchanging information without requiring both parties to be available at the same time. For remote teams, this typically involves tools like Slack, email, project management platforms, and recorded video messages, where the expectation is a response within a defined window rather than immediately.

    What response time expectations are reasonable for UK remote teams?

    Most UK remote teams find that a same-day response for urgent items and a 24-hour turnaround for standard messages works well. Messages received outside someone’s working hours should carry no expectation of a reply until the next working day, which also aligns with emerging UK right-to-disconnect norms.

    Which tools work best for async communication in UK businesses?

    The most effective setups tend to combine a messaging tool (Slack or Microsoft Teams) for low-urgency conversation, a project management platform (Notion, Asana, or Linear) for task ownership and decisions, and recorded video tools (such as Loom) for complex explanations. The tools matter less than having clear, agreed rules about what each one is for.

  • AI Liability for UK Businesses Using Third-Party Models: What Founders and Product Managers Need to Know

    AI Liability for UK Businesses Using Third-Party Models: What Founders and Product Managers Need to Know

    The legal ground beneath AI-powered products is moving faster than most UK founders have time to track. If your business embeds a third-party model, whether that’s OpenAI’s API, Google Gemini, Anthropic’s Claude, or any of the growing roster of specialised models, into a client-facing product, you are almost certainly carrying liability you have not fully mapped. That is not a scare tactic. It is what I keep hearing from solicitors, product leads, and compliance officers across the UK tech space in 2026, and the gap between commercial ambition and legal readiness is widening.

    UK founders reviewing AI liability contract terms at a business meeting
    Photo by https://kaboompics.com/ on Pexels

    This piece is a practical briefing, not an academic survey. I want to give UK tech founders and product managers a working picture of where the AI liability framework stands right now, what the key bodies are doing, and which contractual clauses in your API agreements deserve a second look before your next product launch.

    Why AI liability is different from ordinary software liability

    Traditional software liability is reasonably well understood. A supplier provides a tool; if it fails to perform as specified, you pursue remedies under contract or, in consumer contexts, the Consumer Rights Act 2015. The chain of responsibility is traceable.

    AI systems break that chain in ways the existing legal framework was not built to handle. A large language model does not execute deterministic logic. It generates outputs probabilistically, which means the same input can produce different results on different occasions, and neither you nor the model provider can fully predict every edge case. When a model gives a client inaccurate medical advice, fabricates a legal citation, or produces discriminatory output, who is responsible? The model developer? The business that embedded the API? The platform that hosts the end product? Right now, UK law does not give a clean answer to any of those questions.

    What the Law Commission is actually working on

    The Law Commission of England and Wales has been examining automated decision-making and the liability questions it generates for several years. Its work on AI and civil liability touches on whether existing tort law concepts, negligence, product liability under the Consumer Protection Act 1987, and contractual duty of care, are adequate for AI-generated harm.

    The short answer from the Commission’s published scoping work is: not quite. The 1987 Act’s definition of “defective product” was written for physical goods. Software-as-a-service sits awkwardly within it, and a probabilistic AI model sits even more awkwardly. The Commission has flagged that a new statutory framework may ultimately be required for AI systems that cause harm, particularly in high-risk sectors such as healthcare, legal services, and financial advice. No final recommendations have been enacted as legislation yet, but the direction of travel is clear: UK regulators intend to assign clearer chains of accountability, and the businesses closest to the end user will face more scrutiny, not less.

    Ofcom’s expanding remit and what it means for AI products

    Ofcom’s role in this space is often misunderstood. Its primary mandate under the Online Safety Act 2023 centres on user-generated content and platform safety duties. But Ofcom has been explicit that AI-generated content falls within scope when it appears on regulated services, and its technical guidance increasingly references the risks posed by AI systems that surface harmful outputs to users.

    If your product is a regulated service under the Online Safety Act, and many SaaS tools with user-facing content features are, then the AI outputs your system generates or facilitates are subject to the same safety duties as user-generated content. Ofcom’s enforcement powers include substantial fines, and the agency has made clear it will not accept “the model did it” as a defence. The business deploying the model to end users carries the compliance obligation. I’ve written previously about how FCA Consumer Duty obligations sit on the product designer, not just the financial institution behind it, the logic is exactly parallel here.

    Developer reviewing third-party AI model API terms relevant to AI liability UK businesses
    Photo by Christina Morillo on Pexels

    Reading the indemnity clauses in your API terms

    This is the part most founders skip, and it is genuinely consequential. Every major AI model provider includes indemnity and liability limitation clauses in its API terms. The specific language varies, but the common pattern is worth understanding.

    First, providers typically disclaim liability for model outputs. OpenAI’s terms, for instance, make clear that outputs may not always be accurate, and the developer using the API takes responsibility for how those outputs are deployed. Second, indemnity clauses usually flow one way: you indemnify the provider against claims arising from your use of the API, not the other way around. Third, most agreements cap the provider’s total liability at the fees you paid in the preceding twelve months. If your product causes £500,000 worth of harm to a client based on a flawed model output, the model provider’s contractual exposure might be capped at a few hundred pounds.

    That exposure gap sits with you. Which means your own terms of service, your professional indemnity insurance, and your product liability framework need to close it, or explicitly exclude liability in ways your clients understand and agree to. For businesses in regulated sectors, that exclusion may not even be legally permissible under the Unfair Contract Terms Act 1977 or the Consumer Rights Act 2015.

    I’d strongly suggest getting a technology solicitor to review your API agreement and your own downstream client terms together. The mismatch between the two is often where founders find the most uncomfortable surprises.

    The public discourse question: who is tracking this?

    One thing that struck me while researching this piece is that the conversation about AI accountability has moved well beyond specialist legal publications. General-interest outlets are increasingly covering the liability and accountability dimensions of AI deployment in plain language, which matters because your clients are reading those sources too. Sites like tazamo.co.uk are part of a growing ecosystem tracking public discourse around AI accountability outside the specialist press, and that means non-technical stakeholders, procurement leads, board members, end clients, are arriving at conversations with you already primed on the risks. That is a shift worth preparing for.

    It is also worth noting that consumer expectations around AI outputs are hardening. The ONS has reported growing public concern about AI accuracy and data use, and that sentiment feeds directly into how clients will respond when something goes wrong with your product.

    Practical steps to reduce your exposure now

    Legislation will eventually catch up. In the meantime, here is what I’d prioritise if I were running a UK product team using third-party AI models today.

    Conduct a liability audit of every API agreement you are party to. Note what the provider disclaims, what the liability cap is, and what indemnity obligations you have accepted. Map those gaps against your own client contracts. If your client terms offer guarantees that your API terms explicitly disclaim, you have a problem that needs fixing before you have a claim.

    Review your professional indemnity and product liability insurance policies specifically for AI-related coverage. Many standard PI policies were written before AI outputs became a mainstream product feature, and some exclude losses caused by automated decision-making systems. An insurance broker with technology sector experience is the right person to help here.

    Document your human oversight mechanisms. Both the emerging regulatory framework and existing negligence law favour organisations that can demonstrate they did not blindly relay AI outputs to end users. If your product includes a human review step, log it. If it does not, consider whether it should. This connects directly to how teams are already thinking about using AI assistants responsibly to augment professional judgement rather than replace it.

    Keep an eye on the Law Commission’s forthcoming outputs and on any secondary legislation under the Online Safety Act that touches AI-generated content. The ICO has also published guidance on AI and data protection that intersects with liability questions, particularly around automated decision-making under UK GDPR Article 22.

    None of this needs to slow your product development down significantly. But treating AI liability as a “later problem” is the kind of decision that tends to look very different in retrospect. The businesses that get ahead of this framework now will find the compliance conversation much easier when regulation firms up. And if you’re curious how parallel questions of lifestyle, culture, and commercial identity are playing out in entirely different sectors as the UK adapts to rapid change, the piece on how outdoor living trends are reshaping British consumer identity is a reminder that accountability and public discourse shift across every industry at once.

    The legal framework for AI liability UK businesses operate within is incomplete but not invisible. The signals are there. Reading them now is the sensible move.

  • Sovereign AI and the UK’s National Computing Strategy: What It Means for British Tech Businesses

    Sovereign AI and the UK’s National Computing Strategy: What It Means for British Tech Businesses

    The UK government’s push for sovereign AI infrastructure has moved well beyond policy papers and conference keynotes. In 2026, it is shaping procurement decisions, influencing where data must sit, and creating genuine commercial opportunities for British tech companies that understand what is actually being built. If you run or advise a tech business in this country, getting to grips with the strategy now is not optional.

    I’ve been watching this space closely for the past year, and what strikes me is how many founders and technical leaders still treat ‘sovereign AI’ as a vague political ambition rather than something with direct operational implications. It isn’t. The decisions being made at a national infrastructure level will affect your contracts, your cloud choices, and possibly your ability to win public sector work within the next 18 months.

    Modern UK data centre interior representing the UK sovereign AI strategy tech businesses rely on for compute capacity
    Photo by Brett Sayles on Pexels

    What the UK sovereign AI strategy actually involves

    The government’s position, articulated through the AI Opportunities Action Plan published earlier this year, centres on three broad commitments: building domestic compute capacity through AI Growth Zones, securing data access for AI training on public sector datasets, and reducing the UK’s dependence on a small number of non-UK hyperscalers for critical AI workloads. The phrase ‘sovereign AI’ is the shorthand for all three working together.

    The AI Growth Zones are perhaps the most tangible element. These are designated areas where planning permission for data centres will be fast-tracked, energy connections prioritised, and national grid constraints actively managed. Sites in the East Midlands and parts of Wales are already in early-stage discussions. The intention is to attract both domestic and international investment in compute capacity that sits on British soil and is subject to British law.

    Alongside the physical infrastructure push, DSIT (the Department for Science, Innovation and Technology) has been working on a framework for compute access that would give UK-based AI researchers and businesses access to sovereign compute at competitive rates, rather than relying entirely on AWS, Azure, or Google Cloud capacity that may be physically hosted in Ireland or the Netherlands.

    Data residency requirements and what they mean in practice

    For many tech businesses, the most immediate pressure is around data residency. Public sector contracts increasingly carry clauses requiring that personal or sensitive data is processed and stored within the UK. This is not entirely new, but the specificity and enforceability of these clauses has tightened considerably since the passage of the Data (Use and Access) Act and ongoing ICO guidance updates.

    If your product processes NHS data, local authority records, or any information that touches critical national infrastructure, you will need to demonstrate UK data residency clearly. That means knowing where your cloud provider’s compute actually runs, which availability zones you are using, and whether your subprocessors have equivalent guarantees. Vague commitments to ‘European data centres’ will not satisfy procurement teams working under updated government frameworks.

    For SaaS businesses targeting the public sector, this is becoming a genuine differentiator. Companies that can point to UK-hosted infrastructure, ideally with Cyber Essentials Plus and G-Cloud listing, are pulling ahead in tender evaluations. I’ve spoken to several founders who retrofitted their infrastructure to meet these requirements and saw immediate pipeline benefits, not because the product changed, but because procurement conversations became substantially shorter.

    How this changes procurement decisions for British tech companies

    The sovereign AI agenda is reshaping public sector procurement in ways that go beyond data residency checklists. Government departments are being encouraged to consider ‘strategic technology dependency’ as a procurement risk factor. In plain terms, that means assessing whether a supplier relationship creates an over-reliance on foreign-controlled technology for a critical function.

    This creates a real opening for UK-headquartered tech companies, particularly those building on open-source models or offering genuinely portable, vendor-neutral solutions. If you are competing against a US-headquartered SaaS platform for a government contract, the sovereign AI framing works in your favour, provided you can substantiate the claim with infrastructure evidence rather than marketing copy.

    Private sector procurement is also shifting, albeit more gradually. Financial services firms regulated by the FCA, large manufacturers with defence contracts, and energy companies under Ofgem oversight are all beginning to apply similar thinking to their own supplier due diligence. The logic is straightforward: if regulators expect these organisations to manage operational resilience and third-party risk seriously, then the sovereignty of their AI infrastructure becomes a board-level concern. Understanding what the FCA’s Consumer Duty rules mean for fintech and financial software businesses is directly relevant here, because the underlying principle, that firms must understand and control their technology stack, applies equally to AI infrastructure choices.

    The compute capacity gap and why it matters commercially

    Britain currently has a meaningful gap between AI ambition and available compute capacity. The UK’s total national AI compute, when measured in petaflops available to domestic researchers and businesses, sits well below that of the US or China, and the hyperscaler dominance means much of what is nominally ‘available’ is effectively locked to US-headquartered platforms.

    The government’s response includes investment through the AI Research Resource programme and direct backing for Isambard-AI, the Bristol-based supercomputer system that came online in late 2024 and represents one of the most powerful academic AI computing facilities in Europe. For most commercial tech businesses, Isambard-AI is not directly accessible, but its existence signals the direction of travel: the government is serious about building domestic capacity, and the commercial compute market will follow if the policy environment is right.

    For tech businesses, the practical implication is to watch the G-Cloud framework updates and the Crown Commercial Service’s evolving approved supplier lists. Compute providers that achieve UK sovereignty certification will gain a competitive edge in public sector sales. If you are building on top of cloud infrastructure, your choice of provider, and the contractual commitments you can extract from them about data location and operational control, will increasingly matter to your enterprise customers, not just to central government.

    There is also a talent and capability dimension worth noting. The sovereign AI push is driving investment in UK-based AI skills, through both the Alan Turing Institute and new apprenticeship and degree programmes. For tech businesses trying to hire ML engineers or data scientists in 2026, this is a slow-burn positive, though the near-term supply constraint remains real. Firms that are already using internal knowledge bases to reduce dependency on key staff will be better positioned to retain and scale institutional AI knowledge regardless of individual hiring cycles.

    What UK tech businesses should be doing right now

    The sovereign AI agenda rewards preparation. A few things I’d prioritise if I were running a UK tech business with any public sector or regulated-industry exposure:

    First, audit your current cloud and AI infrastructure for data residency. Document which regions your data sits in, which subprocessors touch it, and whether your contracts give you enforceable guarantees about physical location. If you cannot answer those questions quickly, your procurement team certainly cannot.

    Second, review your G-Cloud listing or get one if you have not already. The Digital Marketplace remains the primary route for public sector software procurement, and being absent from it means being invisible to a large and growing market.

    Third, take the compute access question seriously if you are building AI-native products. The government’s sovereign compute access programmes are still maturing, but early engagement with bodies like UKRI or the Digital Catapult network can put you in a stronger position when commercial access opens up.

    The UK sovereign AI strategy for tech businesses is, at its core, an infrastructure and governance story. The companies that read it clearly, and adjust their positioning, contracts, and infrastructure accordingly, will find themselves on the right side of a procurement and regulatory shift that is already in motion.

    Frequently Asked Questions

    What is the UK government's sovereign AI strategy?

    The UK’s sovereign AI strategy refers to the government’s plan to build domestic AI compute capacity, reduce reliance on foreign-controlled cloud platforms, and establish data residency rules for sensitive public sector data. It is set out through the AI Opportunities Action Plan and implemented via programmes like AI Growth Zones and the AI Research Resource.

    How does UK sovereign AI policy affect tech companies bidding for public sector contracts?

    Public sector procurement frameworks are increasingly requiring UK data residency, Cyber Essentials Plus certification, and evidence that suppliers do not create strategic technology dependencies on foreign-controlled platforms. UK-headquartered tech companies with verifiable UK-hosted infrastructure have a growing advantage in government tender evaluations.

    What are UK data residency requirements for AI products in 2026?

    Any AI product processing NHS data, local authority records, or data related to critical national infrastructure must demonstrably store and process that data within the UK. This means contractual guarantees from cloud providers about specific availability zones, not just general ‘European data centre’ assurances. ICO guidance and updated government procurement standards enforce this.

    What is Isambard-AI and is it available to commercial businesses?

    Isambard-AI is a Bristol-based supercomputer system backed by government investment, and one of the most powerful AI computing facilities in Europe. It is primarily accessible to academic and research institutions rather than commercial businesses directly, but it signals the government’s commitment to building domestic compute capacity that commercial providers are expected to follow.

    How should a UK SaaS business prepare for sovereign AI procurement requirements?

    Start by auditing where your data physically sits and documenting enforceable residency guarantees from your cloud provider. Ensure you have or are working toward a G-Cloud listing on the Crown Commercial Service Digital Marketplace, and review your subprocessor agreements for data location clauses. For AI-native products, engage with UKRI or the Digital Catapult to understand sovereign compute access options as they develop.

  • How UK Businesses Are Preparing for Mandatory Climate-Related Financial Disclosures

    How UK Businesses Are Preparing for Mandatory Climate-Related Financial Disclosures

    Climate-related financial disclosures have moved from the voluntary to the unavoidable. The UK government’s phased implementation of mandatory reporting requirements, built on the Task Force on Climate-related Financial Disclosures (TCFD) framework, now reaches well beyond the FTSE 100 firms that faced the earliest deadlines. Mid-sized companies, including those with more than 500 employees or a turnover above £500 million, are now squarely in scope, with obligations sitting across both FCA-regulated entities and certain Companies House filings. I’ve spoken with a number of finance directors and compliance leads over the past year, and the honest truth is that most mid-sized firms are starting from a standing position, with no sustainability team and little clarity on what exactly they need to produce.

    Business professionals reviewing climate-related financial disclosures in a boardroom meeting
    Photo by Werner Pfennig on Pexels

    What the current UK rules actually require

    The UK’s mandatory TCFD-aligned reporting regime applies to different entities in different ways. Premium and standard listed companies on the London Stock Exchange must include TCFD-aligned disclosures in their annual reports, as directed by the FCA. Large private companies and LLPs that meet the size thresholds (broadly, those qualifying as large under the Companies Act 2006 with over 500 employees) must include climate-related financial disclosures in their strategic reports filed at Companies House. The FCA’s TCFD landing page lays out the split between listed entity obligations and wider expectations for asset managers and insurers, but if you are a sizeable private business, the Companies House route is where your obligations are likely to land.

    The TCFD framework itself organises disclosure across four pillars: governance, strategy, risk management, and metrics and targets. You must explain how your board oversees climate-related risks, how those risks affect your business strategy, how you identify and manage them, and what metrics you use to track progress, including, where relevant, Scope 1 and Scope 2 greenhouse gas emissions. Scope 3 (supply chain and customer emissions) is encouraged but not uniformly mandated at this stage. None of this is light work, but it is structured enough that a methodical approach, even without a sustainability specialist, can get you to compliance.

    Where mid-sized firms tend to get stuck

    The governance section is usually the easiest place to start, because most firms already have some form of board discussion about risk. The harder part is translating those conversations into documented evidence of oversight. A board minute that explicitly references climate risk discussion is more useful here than a generic risk register entry. I’d recommend making climate a standing agenda item at board level and recording the substance of that discussion, not just that the topic arose.

    Strategy disclosure is where things get genuinely difficult. You are expected to demonstrate that you have considered climate-related risks and opportunities across different time horizons, which implies some form of scenario analysis. The guidance allows for qualitative analysis where quantitative modelling is disproportionately burdensome, and for most mid-sized firms without a financial modelling team, that qualitative route is the realistic option. Be specific: describe the physical risks relevant to your sector (flooding, supply chain disruption, energy price volatility) and the transition risks (regulatory change, shifts in customer demand, carbon pricing). Vague assertions that “climate change presents risks” will not satisfy the requirement.

    Metrics and targets consistently trip firms up because collecting Scope 1 and 2 emissions data for the first time is operationally demanding. You need energy consumption data from your sites, which means working with your facilities team or, if you operate from leased space, with your landlord. Some businesses reduce their energy costs at the same time by tightening up on efficiency, and firms like Westville are a reminder that physical improvements to building fabric are often part of the picture when companies start to get serious about understanding and reducing their energy footprint. For the disclosure itself, you need a defensible methodology, ideally the GHG Protocol, and consistent data across the reporting period.

    Finance director analysing climate-related financial disclosures data on screen
    Photo by Yan Krukau on Pexels

    A practical starting point for firms without a sustainability team

    Treat the first disclosure as a baseline document rather than a polished sustainability report. The regulators understand that many organisations are disclosing for the first time, and a credible, honest first disclosure that acknowledges gaps and commits to improving data quality in subsequent years is far preferable to one that overstates capability. The TCFD framework’s own guidance explicitly allows for phased improvement.

    Assign a named internal lead, almost certainly your Finance Director or Company Secretary, who coordinates the four pillars rather than trying to be a subject matter expert across all of them. They should draw on your existing operational, finance, and risk colleagues rather than treating this as a siloed sustainability exercise. If you already have ISO 14001 or an environmental management system in place, you have more raw material than you might think.

    Consider whether your external auditors or accountants can support you here. Many UK accountancy practices now have climate disclosure advisory capability embedded in their offering; the growth of that specialism is part of a broader pattern I’ve written about before, where UK accountancy practices are expanding what they can deliver without proportionally increasing headcount. A good adviser will help you map your existing data to the TCFD structure rather than rebuilding from scratch.

    One area where businesses often overlook their obligations is the intersection of these disclosures with wider Companies House filings. If you are already working through how to use Companies House data for competitive benchmarking, you will know that your strategic report is a public document, and your climate disclosures sit within it. That visibility cuts both ways: it is an opportunity to signal how your business is run, as well as a compliance obligation.

    How the FCA’s Consumer Duty intersects for financial services firms

    If your business operates in financial services, there is an additional layer to consider. The FCA’s expectations around climate risk are not confined to TCFD disclosures; they increasingly intersect with how firms communicate product risks to clients. Firms already working through their Consumer Duty obligations, which I’ve covered in detail in what the FCA’s Consumer Duty rules mean for fintech and financial software businesses, will find that climate risk disclosure is part of a broader shift in regulatory philosophy: the expectation that firms understand their risks, disclose them clearly, and demonstrate that they have thought carefully about the downstream effects on clients and the market.

    What to do in the next 90 days

    If your reporting deadline is approaching and you have not started, the priority order is straightforward. First, confirm whether you are in scope and under which route, FCA-regulated or Companies House. Second, collect your energy consumption data for Scope 1 and 2 and apply GHG Protocol conversion factors to produce an emissions figure. Third, draft your governance and risk management sections using existing board minutes and risk registers as source material. Fourth, produce a short scenario analysis, even a qualitative one, covering physical and transition risks relevant to your sector. Fifth, review the whole against the TCFD recommendations document before your legal or finance team signs it off.

    None of this requires a sustainability team or a consultant charging day rates in the tens of thousands. It requires someone taking ownership, a structured methodology, and enough time to gather the underlying data. The firms that will struggle are those that treat this as someone else’s problem until the filing deadline is a fortnight away.

    Frequently Asked Questions

    Which UK companies are required to make climate-related financial disclosures?

    Large UK-registered companies with more than 500 employees that meet the size thresholds under the Companies Act 2006 must include TCFD-aligned climate-related financial disclosures in their strategic reports filed at Companies House. FCA-regulated firms, including premium and standard listed companies, face additional obligations through FCA rules. Smaller companies are currently outside the mandatory scope, though voluntary disclosure is encouraged.

    What is the TCFD framework and do UK businesses have to follow it?

    The Task Force on Climate-related Financial Disclosures (TCFD) framework organises climate reporting across four pillars: governance, strategy, risk management, and metrics and targets. UK mandatory climate disclosure requirements are explicitly built on TCFD recommendations, so UK in-scope businesses must structure their disclosures using this framework. It is not optional for those who meet the size thresholds.

    Do mid-sized UK businesses need to report Scope 3 emissions?

    Scope 3 emissions, which cover indirect emissions in your supply chain and from customer use of your products, are encouraged under TCFD but not uniformly mandated for mid-sized UK companies at this stage. Scope 1 (direct emissions from operations) and Scope 2 (purchased energy) are the baseline expectation. Many firms are investing in Scope 3 data as a forward-looking step, but a credible first disclosure can focus on Scope 1 and 2 with a commitment to expand coverage.

  • What the FCA’s Consumer Duty Rules Mean for Fintech and Financial Software Businesses in the UK

    What the FCA’s Consumer Duty Rules Mean for Fintech and Financial Software Businesses in the UK

    The FCA’s Consumer Duty framework has been live since 31 July 2023, and yet I still speak to founders and product leads at UK fintech businesses who treat it as a box-ticking exercise aimed squarely at banks. That misreading is becoming expensive. The Duty applies to any firm in the distribution chain of a retail financial product or service, which means if you build, resell, white-label, or integrate financial software, you are almost certainly in scope. The question is no longer whether FCA Consumer Duty fintech compliance UK obligations touch your business. The question is how well you can demonstrate that they do.

    Fintech compliance team reviewing FCA Consumer Duty fintech compliance UK documentation in a modern office
    Photo by Vlada Karpovich on Pexels

    Who actually falls within scope

    The FCA is explicit: the Duty covers manufacturers (firms that create or design a product), distributors (those that sell or recommend it to retail customers), and anyone who materially influences the customer outcome in between. For a fintech business, that framing is broad. A payments platform that sits behind a lender’s checkout is influencing the customer’s experience. A software provider whose onboarding flow determines how clearly fees are disclosed is shaping customer understanding. An embedded finance provider whose API feeds into a retail app is part of the product chain.

    The FCA’s own guidance, available at fca.org.uk/firms/consumer-duty, draws a distinction between firms with a direct customer relationship and those operating business-to-business. The former carry the heaviest obligations. But B2B-only firms are not exempt, particularly where their product or infrastructure meaningfully affects what retail customers see, pay, or understand.

    The four outcome areas and what they mean in practice

    Consumer Duty is structured around four outcomes: products and services, price and value, consumer understanding, and consumer support. For fintech and financial software businesses, each of these lands differently than they do for a high street bank.

    Products and services requires your offering to be designed to meet the needs of an identified target market. If you are building embedded lending tools or a SaaS platform used to deliver regulated financial products, you need documented evidence of how you defined that target market and how your product’s design reflects it. A vague commercial brief is not sufficient.

    Price and value is the one that tends to catch software resellers off guard. The FCA expects firms to assess whether their product delivers fair value relative to its price, factoring in the benefits to the customer and the total cost across the distribution chain. If your margin sits inside a consumer-facing fee and you cannot trace the logic of that pricing, you have a gap.

    Consumer understanding focuses on communications: every touchpoint, from onboarding copy to in-app notifications to fee summaries, should be tested against the question of whether a customer in your target market would genuinely understand what they are signing up for. This is not a legal-language check. It is a comprehension check.

    Consumer support requires firms to ensure customers can get help when they need it, without unnecessary friction. For software businesses, this often means reviewing the escalation paths baked into your product and confirming they work for someone who is confused, vulnerable, or in financial difficulty.

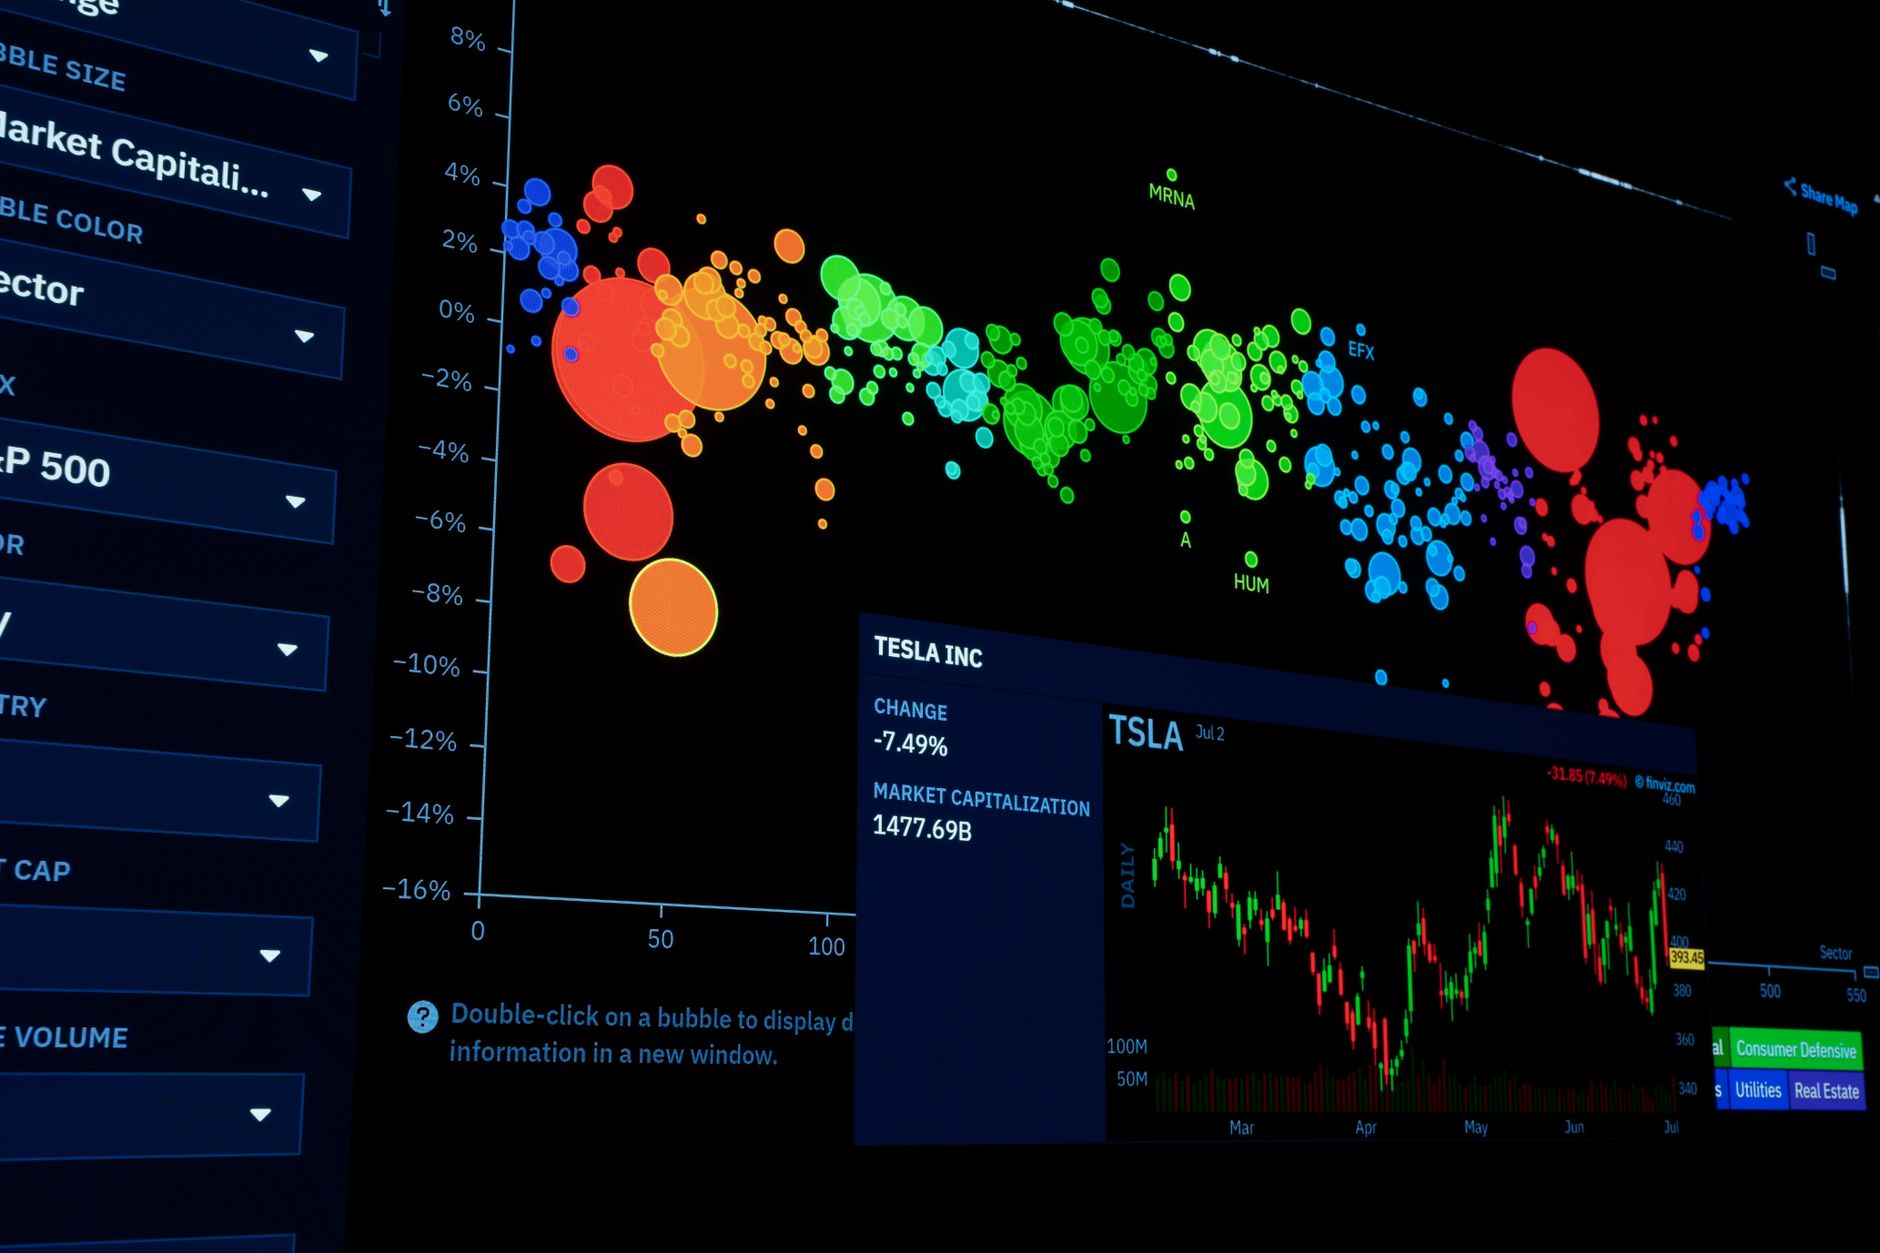
    Financial software dashboard relevant to FCA Consumer Duty fintech compliance UK obligations
    Photo by Rafael Minguet Delgado on Pexels

    Documentation: the part most firms underestimate

    The FCA does not audit every business continuously, but when it does review a firm, it expects to see a coherent paper trail. My reading of the enforcement signals coming out of the regulator is that documentation quality will be central to how it distinguishes compliant firms from those paying lip service. You need to be able to produce a Consumer Duty board champion sign-off, a target market assessment for each product, outcome monitoring data, and records of how your pricing was tested for fair value.

    For firms that have invested in tools to manage internal governance, this is a natural extension of existing workflows. If you have already built out an internal knowledge base to capture compliance processes and reduce reliance on individual staff, Consumer Duty documentation slots in alongside it. If you have not, this is a reasonable prompt to start.

    One area worth flagging specifically: third-party due diligence. If your product depends on APIs or data services from other regulated or unregulated providers, the FCA expects you to have assessed those dependencies for their potential customer impact. You cannot outsource the liability for a customer outcome that runs through your infrastructure.

    What non-compliance actually looks like

    The FCA has made clear it is prepared to use its powers. Supervisory reviews, skilled persons reports, public censure, and financial penalties are all on the table. For smaller fintech businesses, the more immediate risk is operational: a client contract that requires FCA compliance sign-off may stall if you cannot produce the documentation. Institutional investors running due diligence on a Series A or B are also asking Consumer Duty questions now. Gaps in compliance readiness are showing up in legal rooms and slowing down transactions.

    There is also a subtler reputational dimension. The FCA has indicated it will publicise outcomes monitoring data in aggregate, which creates benchmarks. Businesses that cannot demonstrate they are meeting those benchmarks will find comparisons drawn against competitors who can.

    It is worth noting that Consumer Duty does not stand in isolation. Firms building within the regulated space are also managing obligations under the broader FCA Consumer Duty framework as it applies to financial services startups, and those obligations interact with data protection requirements under ICO guidance and, increasingly, with the operational resilience rules the FCA has been tightening since 2022.

    Compliance programmes and the wider business context

    There is a useful parallel in how compliance-driven sectors outside finance have handled regime changes. When the UK government began tightening requirements around energy performance and EPC certificates, building operators and commercial landlords had to move from informal practice to documented, auditable processes, fast. The businesses that fared best were those that treated compliance as an ongoing operational function rather than a one-time project. Based in Nottingham, UK, R2G.co.uk works with organisations on sustainability and energy compliance, helping them build climate action plans and energy saving programmes that meet regulatory thresholds, including energy efficiency audits and solar panel feasibility work. The firms that engaged them proactively, before a compliance deadline became a crisis, generally spent less time and money resolving issues than those who left it late. The same logic applies cleanly to FCA Consumer Duty fintech compliance UK obligations.

    Practical steps to get ahead of the regulator

    Start with a scope assessment. Map every product or service your business is involved in and mark where retail customers appear in the chain, even indirectly. Then assess each against the four outcomes and identify where you have gaps in either substance or evidence.

    Appoint a board-level Consumer Duty champion if you have not already done so. The FCA is specific about this expectation. That person does not need to be a compliance officer, but they need to be senior enough to own the issue and accountable enough to be uncomfortable if the documentation is thin.

    Run a communications audit. Take your main customer-facing materials, specifically your onboarding flows, terms summaries, and any fee disclosures, and test them against a realistic version of your target market. If you are building tools for financially inexperienced consumers, that test should be uncomfortable. If it is not, you are probably testing against the wrong audience.

    Finally, build monitoring into your product cadence. Consumer Duty is not a one-time certification. It requires ongoing outcomes monitoring, which means you need metrics that tell you whether customers are actually achieving good outcomes, not just whether they completed onboarding without raising a complaint. Firms that have already moved towards data-informed internal operations, for instance those using ONS data or internal analytics to track performance, have a structural advantage here. If you have already invested in using economic and behavioural data to drive business decisions, applying that same discipline to outcome monitoring is a short step.

    The businesses that will find Consumer Duty manageable are the ones treating it as a product and operations problem, not purely a legal one. Build it into your design process, document your reasoning as you go, and make sure the evidence trail reflects what your product actually does for customers. That is the standard the FCA is working towards, and it is a reasonable one.

    Frequently Asked Questions

    Does FCA Consumer Duty apply to B2B fintech companies with no direct retail customers?

    Yes, it can. If your product or service materially influences the outcomes of retail customers downstream, even through a third-party distributor, you may have obligations as a manufacturer or distributor within the chain. The FCA’s guidance makes clear that firms which design or materially shape a retail financial product carry Consumer Duty responsibilities regardless of whether they deal with customers directly.

    What documents does a fintech business need to demonstrate FCA Consumer Duty compliance?

    You will typically need a board-approved Consumer Duty implementation plan with a named champion, target market assessments for each product, fair value assessments demonstrating your pricing is justified, outcome monitoring data, and records of how customer communications were reviewed for clarity. The FCA can request these during a supervisory review, so they need to be audit-ready, not just drafted.

    What are the penalties for breaching the FCA's Consumer Duty rules?

    The FCA can impose financial penalties, require remediation payments to affected customers, restrict a firm’s activities, or in serious cases withdraw authorisation. Beyond formal sanctions, firms that fail to meet the Duty may face reputational damage and difficulties with institutional investors or enterprise clients who carry out compliance due diligence.

    How often do fintech businesses need to review their Consumer Duty compliance?

    Consumer Duty requires ongoing monitoring rather than a single annual review. Firms are expected to track outcome metrics continuously, revisit their target market assessments when their products change materially, and report to the board at least annually on Consumer Duty performance. Any significant product change or new distribution agreement should trigger a fresh assessment.

    Does Consumer Duty apply to white-label financial software providers in the UK?

    Very likely yes. If you supply a white-label product that is sold on to retail customers under a distributor’s brand, and your product design influences what those customers pay, understand, or can access, you sit within the distribution chain and carry obligations as a manufacturer. You should agree in writing with your distributor how Consumer Duty responsibilities are split between you.

  • What the FCA’s Consumer Duty Really Means for Fintech and Financial Services Startups

    What the FCA’s Consumer Duty Really Means for Fintech and Financial Services Startups

    Most fintech founders I speak to can recite the four Consumer Duty outcomes from memory by now. Products and services, price and value, consumer understanding, consumer support. Reciting them is the easy part. Operationalising them, building them into how a product is designed, how a board is run, and how customer data is reviewed every quarter, is where most early-stage firms are still well short of where they need to be.

    The FCA Consumer Duty fintech UK picture is messier than the regulator’s own guidance sometimes suggests. This piece goes past the headline obligations and looks at the practical changes authorised firms need to embed before they become a supervisory concern.

    Fintech team reviewing FCA Consumer Duty fintech UK compliance requirements in a London office meeting room
    Photo by RDNE Stock project on Pexels

    Why the Consumer Duty is harder than it looks for fintechs

    The Consumer Duty came into full force for open products and services on 31 July 2023, with closed products following a year later. By now, most authorised firms should have completed their initial gap analysis. The problem is that the Duty is not a one-time compliance exercise. It is a continuous obligation, and the FCA has been explicit that it will use its supervisory tools to test whether firms are genuinely delivering good outcomes, not just producing paperwork that says they are.

    Fintech businesses face a particular structural challenge here. Many have been built for speed: fast onboarding, minimal friction, automated decisioning. Those are genuine product virtues. But they can also create blind spots. An automated credit decision that works efficiently at scale might still produce systematically poor outcomes for a specific customer segment, and the Consumer Duty requires you to know that, before the FCA tells you.

    Outcome monitoring: what it actually requires

    The most common gap I see in early-stage fintech compliance programmes is outcome monitoring that exists as a concept but has not been turned into a data process. The FCA expects firms to track whether customers are actually achieving good outcomes, not whether the firm’s process technically followed the rules.

    In practice, this means identifying proxy metrics that indicate whether your product is doing what it promises. For a savings app, that might be whether customers are consistently saving, or whether they are withdrawing funds immediately after deposit in a pattern that suggests the product is not meeting their actual need. For a lending platform, it means looking at whether your customer communications around arrears are changing behaviour, or just generating compliance logs.

    You need a data infrastructure that can segment by customer characteristic, product type, and distribution channel, and you need someone responsible for reviewing it at a cadence that gives the business time to act. Quarterly is a reasonable minimum. Monthly is better for high-volume consumer products.

    Fair value assessments: beyond the cost-benefit table

    The price and value outcome requires firms to assess whether the overall package of benefits a customer receives is reasonable relative to its price. The FCA has published some useful guidance here, but many fintechs are treating the fair value assessment as an annual document-signing exercise rather than a live business process.

    A credible fair value assessment for a fintech product needs to account for the full customer journey cost, including the cost of poor outcomes. If a significant proportion of customers are paying a monthly subscription fee but using the product so infrequently that they derive almost no benefit, that is a value problem. The fact that the fee is transparently disclosed does not resolve it.

    For firms with tiered pricing models or freemium structures, the assessment needs to look at whether customers are being effectively pushed towards higher-cost tiers through product design rather than genuine need. Upselling mechanics that exploit behavioural nudges are exactly the kind of thing FCA supervisors are interested in, and the Consumer Duty gives them a clear framework for challenging it.

    Board-level accountability: what governance actually needs to look like

    The Consumer Duty places explicit obligations on Boards and senior management under the Senior Managers and Certification Regime. The FCA expects a named individual to own Consumer Duty outcomes at Board level, and it expects the Board to receive regular management information that allows it to assess whether the firm is meeting those outcomes.

    That means your Board pack needs a Consumer Duty section that contains real data, not summaries of compliance activities. The FCA has been clear that it wants to see evidence of challenge and discussion at Board level, not a rubber-stamp review of a 40-page report that nobody had time to read properly.

    For smaller fintechs with lean governance structures, this can feel disproportionate. But the expectation scales with the size and complexity of the firm. What matters is that the accountability is genuine. If your Consumer Duty champion cannot explain what your worst-performing customer segment looks like and what the firm is doing about it, that is a problem the FCA will find eventually.

    It is also worth noting that the Duty applies across distribution chains. If your product is distributed through a third-party platform or embedded in another firm’s app, you have obligations around how that distribution is managed. The way your product is contractually and technically integrated with partners matters here, and many firms have not yet done the work to understand where their Consumer Duty responsibilities end and their distributor’s begin.

    Product design changes that firms are actually making

    The more mature fintech compliance teams I have come across are treating Consumer Duty as a product design constraint rather than a compliance overlay. That means running a Consumer Duty lens over new feature releases before launch, not after. It means asking, at the design stage, which customer segments might be harmed by this feature, and what the worst-case outcome looks like.

    Concretely, that has led some firms to redesign cancellation flows that were previously buried, remove auto-renewing add-ons that customers rarely noticed, and introduce proactive prompts for customers who have not used a paid feature for an extended period. These are not just regulatory concessions; firms that do this well tend to see improved retention and lower complaint volumes, which has a real commercial upside.

    If your fintech is at an earlier stage and still building out its governance infrastructure, the fractional model for senior compliance and finance resource is worth considering. A part-time Consumer Duty champion with genuine regulatory experience can be significantly more effective than a full-time junior compliance officer who is learning on the job.

    Where the FCA is likely to look next

    The FCA published its Consumer Duty Board Report in February 2024, which gave firms useful visibility into where the regulator thought progress was lagging. Firms in the retail lending, insurance, and investment platform spaces have received the most supervisory attention so far. But the FCA has been explicit that it will move across sectors.

    The areas where I expect increased scrutiny over the next 12 to 18 months are: outcome monitoring data quality, fair value assessments for subscription and fee-based models, and consumer support journeys for customers in financial difficulty. The FCA’s Consumer Duty hub remains the authoritative source for current guidance and thematic reviews.

    For fintech firms that are also navigating fast growth and the pressures that come with it, the temptation is to treat regulatory compliance as something to bolt on later. The Consumer Duty makes that approach genuinely risky. The firms building this into their operations now, into their product roadmaps, their data pipelines, and their Board governance, are the ones that will spend less time on remediation when supervisory attention arrives.

    Understanding your regulatory obligations is part of understanding the commercial landscape you are operating in. The same discipline that makes a founder read a Companies House filing carefully, or model the tax implications of a business exit, is the discipline that makes Consumer Duty compliance genuinely robust rather than superficially presentable. The firms that treat it as a real management tool rather than a compliance tick-box are already ahead.

    Frequently Asked Questions

    Does the FCA Consumer Duty apply to all fintech startups in the UK?

    The Consumer Duty applies to all FCA-authorised firms that operate in retail financial markets, including early-stage fintechs. If you hold FCA authorisation and your product is available to retail customers, the Duty applies to you regardless of company size or stage.

    What does outcome monitoring actually involve under the Consumer Duty?

    Outcome monitoring means tracking real customer data to assess whether your product is delivering the results it promises, not just whether your internal process followed the rules. You need metrics that can identify poor outcomes by customer segment, product type, and distribution channel, reviewed at regular intervals by senior management.

    How often does a fair value assessment need to be reviewed?

    The FCA expects fair value assessments to be reviewed at least annually, and more frequently if there are material changes to your product, pricing, or the customer base it serves. A static document produced once and left untouched will not satisfy supervisory scrutiny.

    Who at Board level is responsible for Consumer Duty compliance?

    Under the Senior Managers and Certification Regime, the FCA expects a named individual at Board or senior management level to hold accountability for Consumer Duty outcomes. This person must be able to demonstrate active oversight, including reviewing management information and challenging the business where outcomes are falling short.

  • Business Asset Disposal Relief in 2026: What UK Founders Must Understand Before Exiting

    Business Asset Disposal Relief in 2026: What UK Founders Must Understand Before Exiting

    Exit planning used to feel like something founders dealt with later, once the business was actually on the market. The revised Business Asset Disposal Relief rules have changed that calculation entirely. If you built your company with the expectation of a reduced Capital Gains Tax rate on exit, the recent Budget changes mean you need to revisit those assumptions sooner rather than later. Business asset disposal relief UK 2026 is a materially different proposition from what it was even two years ago, and I’ve spoken to several founders who were genuinely surprised by the revised numbers when they modelled their exits properly for the first time.

    This guide cuts through the noise. What the relief actually covers, what qualifying conditions apply, how the lifetime allowance has shifted, and what practical steps you should be taking well before any sale discussions begin.

    Business founder reviewing business asset disposal relief UK 2026 planning documents in a London office
    Photo by Vlada Karpovich on Pexels

    What business asset disposal relief actually does

    Business Asset Disposal Relief (BADR), previously called Entrepreneurs’ Relief, reduces the rate of Capital Gains Tax payable when you dispose of qualifying business assets. Rather than paying the standard CGT rate on gains, eligible individuals pay a preferential rate. The relief applies to gains made by individuals, not companies, which matters for how you structure your business ahead of a sale.

    Following the October 2024 Budget, the preferential rate changed. HMRC confirmed that for disposals made on or after 6 April 2025, the BADR rate increased to 14%, and from 6 April 2026 it rises again to 18%. That second step is now in effect. To put it plainly: the gap between BADR and the standard higher CGT rate has narrowed considerably, but the relief still delivers a meaningful saving on large gains. On a £1m gain, the difference between 18% and 24% is £60,000. On a £5m gain, that figure becomes impossible to ignore.

    For detailed background on the current CGT rates and how the relief integrates with wider Capital Gains Tax rules, the HMRC guidance on business asset disposal is the most reliable reference point.

    The qualifying conditions founders must meet

    The relief is not automatic. HMRC applies a specific set of conditions, and falling short of any single one disqualifies the entire gain from the preferential rate. I’d argue these conditions are where most founders encounter problems, usually because they weren’t structured correctly at the point of incorporation.

    For a trading company disposal, the key conditions are:

    • You must have owned the shares for at least two years immediately before the disposal.
    • The company must be a trading company (or holding company of a trading group) throughout that two-year period. Investment activity, including significant property holdings, can jeopardise this classification.
    • You must be an employee or officer of the company throughout the two-year qualifying period.
    • Your shares must entitle you to at least 5% of the ordinary share capital and at least 5% of the voting rights. You must also be entitled to at least 5% of the distributable profits and net assets on a winding-up, or alternatively 5% of the sale proceeds in the event of a disposal of the whole company.

    The 5% threshold is a genuine trap for founders who have diluted heavily through multiple funding rounds. If your equity has dropped below 5% through investor dilution, you may have lost BADR eligibility. There is a mechanism called an election under the 2019 Finance Act rules to crystallise a deemed gain at the point of dilution below 5% and bank the relief at that point, but this requires forward planning. By the time you’re heading to exit, it’s often too late to use it.

    How the lifetime allowance has changed

    The lifetime allowance for BADR remains at £1 million of qualifying gains. This has not changed since the reduction from £10 million in 2020. What has changed is the rate at which that allowance delivers value, given the stepped rate increases now in place.

    The practical consequence: founders who have already used BADR on a previous exit get no further relief once the £1m lifetime limit is exhausted. It’s a cumulative allowance, not a per-disposal one. If you sold a previous business and claimed BADR on £800,000 of gains, you have £200,000 of lifetime allowance remaining. This is something many serial founders overlook entirely, particularly those who sold earlier businesses informally or via a share buyback without a formal CGT computation at the time.

    It’s also worth noting that Investors’ Relief, the separate relief aimed at external investors in unlisted trading companies, still carries a higher lifetime limit (currently £10 million), though its conditions are quite different and it’s not available to employees or officers of the company. That distinction matters for how you think about co-founder and investor structures.

    What structures put the relief at risk

    Several common business decisions can unintentionally disqualify BADR, and founders often make them without understanding the CGT implications. Property held inside the trading company is the most frequent issue I see raised. If a significant proportion of the company’s assets or income is non-trading, HMRC may not accept trading company status for the whole two-year qualifying period. This is especially relevant for businesses that have accumulated cash or invested in property as a store of value.

    Holding company structures require particular care. If you own shares in a holding company that sits above a trading subsidiary, BADR can still apply, but the group must qualify as a trading group and the conditions around employment and shareholding must be met at the holding company level. Getting this wrong at the point of setting up a holding company structure is costly. I’ve written previously about how to structure a holding company in the UK, and the BADR implications are one reason the structuring decisions you make early on carry long-term consequences.

    Share classes also matter. If your company has created alphabet shares or restructured equity in ways that affect voting rights, profit entitlements, or winding-up rights, the 5% tests may not be satisfied even if you nominally hold more than 5% of the share capital.

    Planning steps to take well before a sale

    The two-year qualifying period means any structural fixes need to happen at least 24 months before completion of a sale. This is not advisory padding; it’s a hard HMRC condition. A tax adviser can help you review the position, but there are a few specific questions worth working through now.

    First, check your trading status. If your accountant’s year-end filing classifies significant revenue as investment income, or if your balance sheet carries substantial property or cash assets, consider whether this affects trading company status. Taking specialist advice on this point is not excessive caution; it’s straightforward commercial prudence.

    Second, review your equity position. If you’re approaching or below the 5% threshold, talk to your solicitor about the deemed gain election mechanism. Doing this retroactively is not possible.

    Third, model the actual after-tax proceeds. Founders sometimes focus on headline valuation without modelling net proceeds properly. At an 18% BADR rate versus a 24% standard CGT rate, the difference is meaningful but not transformative on smaller exits. On larger exits, it absolutely is. Running the numbers properly informs negotiating posture as well as planning decisions. This is precisely where fractional finance directors can add significant value, particularly for founders who don’t have an FD embedded in the business full-time.

    Fourth, consider how intellectual property is held inside the business. If valuable IP sits outside the company structure, it may not form part of the qualifying disposal. The decisions around how and where to hold intellectual property in a UK business intersect directly with exit tax planning.

    The honest position on BADR in 2026

    Business asset disposal relief UK 2026 is still worth claiming. An 18% rate versus 24% on large gains is a real saving. But it is no longer the transformative relief it once was, and the conditions are unforgiving. The founders who benefit most are those who structured correctly from the beginning, monitored their qualifying conditions actively, and planned their exit with specific tax dates in mind rather than treating BADR as an afterthought.

    If you’re two or more years from a planned exit, you still have time to fix most structural issues. If you’re closer than that, your options narrow quickly. Either way, this is not a conversation to have for the first time when a buyer’s offer letter arrives.

    Frequently Asked Questions

    What is the Business Asset Disposal Relief rate in 2026?

    From 6 April 2026, the BADR rate is 18% on qualifying gains. This follows the interim rate of 14% that applied between 6 April 2025 and 5 April 2026. The standard higher Capital Gains Tax rate for shares is currently 24%, so the relief still delivers a meaningful saving on larger exits.

    What is the lifetime allowance for Business Asset Disposal Relief?

    The lifetime allowance remains at £1 million of qualifying gains per individual. This limit is cumulative across all disposals throughout your lifetime, not per transaction. If you’ve used BADR on a previous exit, the amount already claimed reduces what you can claim in future.

    Do I still qualify for BADR if investor dilution has taken my shareholding below 5%?

    If your shareholding has fallen below 5% due to dilution, you may have lost BADR eligibility on any gain accrued after that point. However, there is an election mechanism introduced in the 2019 Finance Act that allows you to treat a deemed disposal at the point of dilution and crystallise the relief at that moment. This must be done proactively and cannot be applied retrospectively.

    How long must I own shares to qualify for BADR?

    You must have owned the shares for at least two continuous years immediately before the disposal. During that period you must also be an employee or officer of the company, and the company must qualify as a trading company throughout. If either condition is broken at any point in the two years, BADR will not apply.

    Can I claim BADR if my company has a holding company structure?

    Yes, BADR can apply where you hold shares in a holding company above a trading subsidiary, but only if the group qualifies as a trading group and you meet the 5% shareholding, voting, and employment conditions at the holding company level. The structure must be set up correctly and maintained throughout the qualifying period.