Category: The World

  • Sovereign AI and the UK’s National Computing Strategy: What It Means for British Tech Businesses

    Sovereign AI and the UK’s National Computing Strategy: What It Means for British Tech Businesses

    The UK government’s push for sovereign AI infrastructure has moved well beyond policy papers and conference keynotes. In 2026, it is shaping procurement decisions, influencing where data must sit, and creating genuine commercial opportunities for British tech companies that understand what is actually being built. If you run or advise a tech business in this country, getting to grips with the strategy now is not optional.

    I’ve been watching this space closely for the past year, and what strikes me is how many founders and technical leaders still treat ‘sovereign AI’ as a vague political ambition rather than something with direct operational implications. It isn’t. The decisions being made at a national infrastructure level will affect your contracts, your cloud choices, and possibly your ability to win public sector work within the next 18 months.
    Modern UK data centre interior representing the UK sovereign AI strategy tech businesses rely on for compute capacity
    Photo by Brett Sayles on Pexels

    What the UK sovereign AI strategy actually involves

    The government’s position, articulated through the AI Opportunities Action Plan published earlier this year, centres on three broad commitments: building domestic compute capacity through AI Growth Zones, securing data access for AI training on public sector datasets, and reducing the UK’s dependence on a small number of non-UK hyperscalers for critical AI workloads. The phrase ‘sovereign AI’ is the shorthand for all three working together.

    The AI Growth Zones are perhaps the most tangible element. These are designated areas where planning permission for data centres will be fast-tracked, energy connections prioritised, and national grid constraints actively managed. Sites in the East Midlands and parts of Wales are already in early-stage discussions. The intention is to attract both domestic and international investment in compute capacity that sits on British soil and is subject to British law.

    Alongside the physical infrastructure push, DSIT (the Department for Science, Innovation and Technology) has been working on a framework for compute access that would give UK-based AI researchers and businesses access to sovereign compute at competitive rates, rather than relying entirely on AWS, Azure, or Google Cloud capacity that may be physically hosted in Ireland or the Netherlands.

    Data residency requirements and what they mean in practice

    For many tech businesses, the most immediate pressure is around data residency. Public sector contracts increasingly carry clauses requiring that personal or sensitive data is processed and stored within the UK. This is not entirely new, but the specificity and enforceability of these clauses has tightened considerably since the passage of the Data (Use and Access) Act and ongoing ICO guidance updates.

    If your product processes NHS data, local authority records, or any information that touches critical national infrastructure, you will need to demonstrate UK data residency clearly. That means knowing where your cloud provider’s compute actually runs, which availability zones you are using, and whether your subprocessors have equivalent guarantees. Vague commitments to ‘European data centres’ will not satisfy procurement teams working under updated government frameworks.

    For SaaS businesses targeting the public sector, this is becoming a genuine differentiator. Companies that can point to UK-hosted infrastructure, ideally with Cyber Essentials Plus and G-Cloud listing, are pulling ahead in tender evaluations. I’ve spoken to several founders who retrofitted their infrastructure to meet these requirements and saw immediate pipeline benefits, not because the product changed, but because procurement conversations became substantially shorter.

    How this changes procurement decisions for British tech companies

    The sovereign AI agenda is reshaping public sector procurement in ways that go beyond data residency checklists. Government departments are being encouraged to consider ‘strategic technology dependency’ as a procurement risk factor. In plain terms, that means assessing whether a supplier relationship creates an over-reliance on foreign-controlled technology for a critical function.

    This creates a real opening for UK-headquartered tech companies, particularly those building on open-source models or offering genuinely portable, vendor-neutral solutions. If you are competing against a US-headquartered SaaS platform for a government contract, the sovereign AI framing works in your favour, provided you can substantiate the claim with infrastructure evidence rather than marketing copy.

    Private sector procurement is also shifting, albeit more gradually. Financial services firms regulated by the FCA, large manufacturers with defence contracts, and energy companies under Ofgem oversight are all beginning to apply similar thinking to their own supplier due diligence. The logic is straightforward: if regulators expect these organisations to manage operational resilience and third-party risk seriously, then the sovereignty of their AI infrastructure becomes a board-level concern. Understanding what the FCA’s Consumer Duty rules mean for fintech and financial software businesses is directly relevant here, because the underlying principle, that firms must understand and control their technology stack, applies equally to AI infrastructure choices.

    The compute capacity gap and why it matters commercially

    Britain currently has a meaningful gap between AI ambition and available compute capacity. The UK’s total national AI compute, when measured in petaflops available to domestic researchers and businesses, sits well below that of the US or China, and the hyperscaler dominance means much of what is nominally ‘available’ is effectively locked to US-headquartered platforms.

    The government’s response includes investment through the AI Research Resource programme and direct backing for Isambard-AI, the Bristol-based supercomputer system that came online in late 2024 and represents one of the most powerful academic AI computing facilities in Europe. For most commercial tech businesses, Isambard-AI is not directly accessible, but its existence signals the direction of travel: the government is serious about building domestic capacity, and the commercial compute market will follow if the policy environment is right.

    For tech businesses, the practical implication is to watch the G-Cloud framework updates and the Crown Commercial Service’s evolving approved supplier lists. Compute providers that achieve UK sovereignty certification will gain a competitive edge in public sector sales. If you are building on top of cloud infrastructure, your choice of provider, and the contractual commitments you can extract from them about data location and operational control, will increasingly matter to your enterprise customers, not just to central government.

    There is also a talent and capability dimension worth noting. The sovereign AI push is driving investment in UK-based AI skills, through both the Alan Turing Institute and new apprenticeship and degree programmes. For tech businesses trying to hire ML engineers or data scientists in 2026, this is a slow-burn positive, though the near-term supply constraint remains real. Firms that are already using internal knowledge bases to reduce dependency on key staff will be better positioned to retain and scale institutional AI knowledge regardless of individual hiring cycles.

    What UK tech businesses should be doing right now

    The sovereign AI agenda rewards preparation. A few things I’d prioritise if I were running a UK tech business with any public sector or regulated-industry exposure:

    First, audit your current cloud and AI infrastructure for data residency. Document which regions your data sits in, which subprocessors touch it, and whether your contracts give you enforceable guarantees about physical location. If you cannot answer those questions quickly, your procurement team certainly cannot.

    Second, review your G-Cloud listing or get one if you have not already. The Digital Marketplace remains the primary route for public sector software procurement, and being absent from it means being invisible to a large and growing market.

    Third, take the compute access question seriously if you are building AI-native products. The government’s sovereign compute access programmes are still maturing, but early engagement with bodies like UKRI or the Digital Catapult network can put you in a stronger position when commercial access opens up.

    The UK sovereign AI strategy for tech businesses is, at its core, an infrastructure and governance story. The companies that read it clearly, and adjust their positioning, contracts, and infrastructure accordingly, will find themselves on the right side of a procurement and regulatory shift that is already in motion.

    Frequently Asked Questions

    What is the UK government's sovereign AI strategy?

    The UK’s sovereign AI strategy refers to the government’s plan to build domestic AI compute capacity, reduce reliance on foreign-controlled cloud platforms, and establish data residency rules for sensitive public sector data. It is set out through the AI Opportunities Action Plan and implemented via programmes like AI Growth Zones and the AI Research Resource.

    How does UK sovereign AI policy affect tech companies bidding for public sector contracts?

    Public sector procurement frameworks are increasingly requiring UK data residency, Cyber Essentials Plus certification, and evidence that suppliers do not create strategic technology dependencies on foreign-controlled platforms. UK-headquartered tech companies with verifiable UK-hosted infrastructure have a growing advantage in government tender evaluations.

    What are UK data residency requirements for AI products in 2026?

    Any AI product processing NHS data, local authority records, or data related to critical national infrastructure must demonstrably store and process that data within the UK. This means contractual guarantees from cloud providers about specific availability zones, not just general ‘European data centre’ assurances. ICO guidance and updated government procurement standards enforce this.

    What is Isambard-AI and is it available to commercial businesses?

    Isambard-AI is a Bristol-based supercomputer system backed by government investment, and one of the most powerful AI computing facilities in Europe. It is primarily accessible to academic and research institutions rather than commercial businesses directly, but it signals the government’s commitment to building domestic compute capacity that commercial providers are expected to follow.

    How should a UK SaaS business prepare for sovereign AI procurement requirements?

    Start by auditing where your data physically sits and documenting enforceable residency guarantees from your cloud provider. Ensure you have or are working toward a G-Cloud listing on the Crown Commercial Service Digital Marketplace, and review your subprocessor agreements for data location clauses. For AI-native products, engage with UKRI or the Digital Catapult to understand sovereign compute access options as they develop.
  • How UK Businesses Are Using Digital Twins to Model Operations Before Spending a Penny

    How UK Businesses Are Using Digital Twins to Model Operations Before Spending a Penny

    There is a particular kind of expensive lesson that most business owners know well: you commit capital, roll out a process, and only then discover the flaw that was obvious in hindsight. Digital twin technology is, at its core, a direct answer to that problem. It lets you build a precise virtual replica of a physical process, facility, or operational workflow, run it through simulated conditions, and stress-test decisions before a single pound leaves your account.

    What was once the preserve of aerospace and defence contractors is now reaching UK manufacturing plants in the Midlands, logistics hubs across the North West, and even professional services firms in London. The price of entry has dropped substantially, and the practical upside is significant enough that mid-market operators can no longer afford to dismiss it as enterprise-only technology.

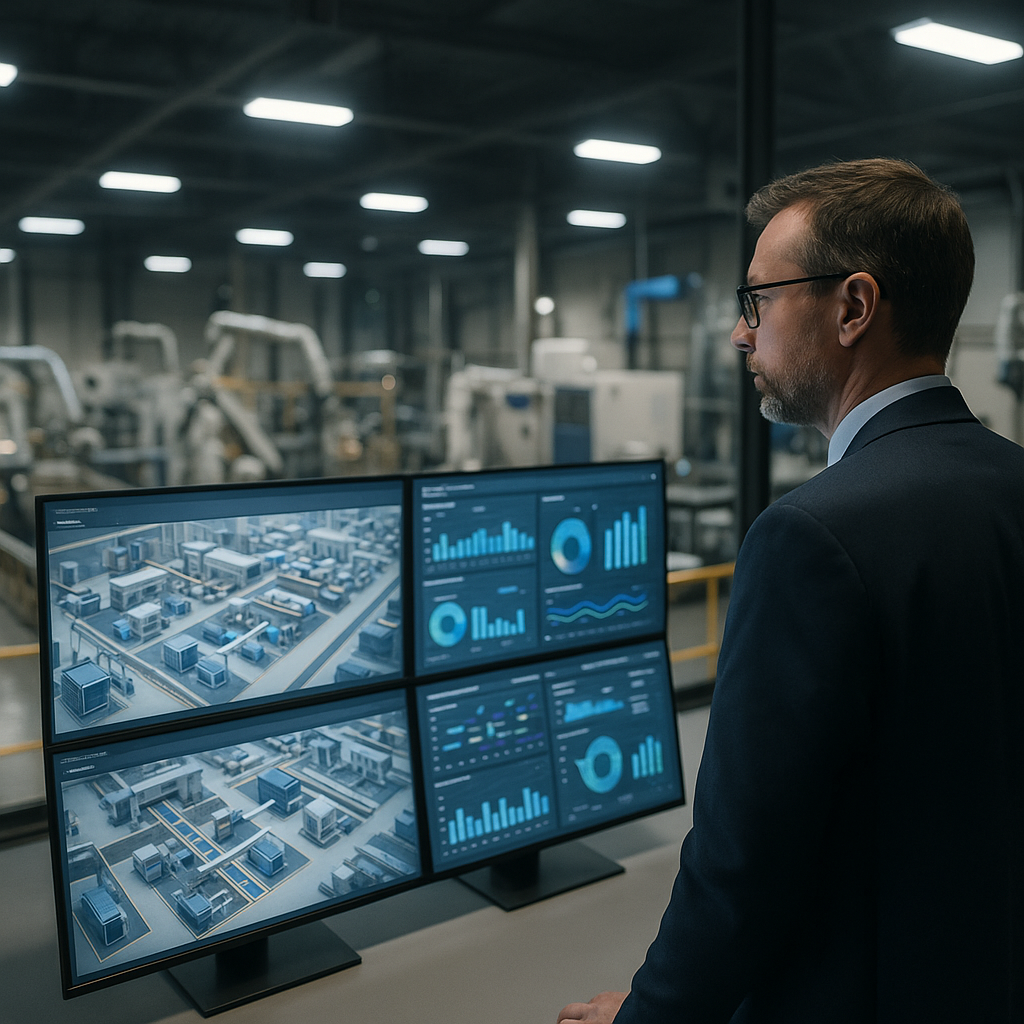
    Operations manager reviewing digital twin technology simulation in a UK manufacturing control room

    What digital twin technology actually means for a mid-sized business

    The phrase gets misused often. A digital twin is not simply a 3D model or a dashboard of live metrics. It is a dynamic, data-fed simulation that mirrors a real-world system in something close to real time. When conditions change in the physical world, the twin updates. When you want to test a hypothetical change, you apply it to the twin first and observe what the model predicts.

    A warehouse operator, for instance, might build a digital twin of their pick-and-pack floor. They can then simulate what happens when order volumes spike by 40 per cent, a conveyor goes offline, or a new fulfilment layout is introduced. Instead of reorganising the physical space and discovering the bottleneck three weeks later, they find it in the simulation on a Tuesday afternoon and never disrupt live operations at all.

    The UK’s Manufacturing Technology Centre in Coventry has been actively supporting SMEs in this space, running pilot programmes specifically designed to help smaller manufacturers understand where simulation tools can generate measurable returns. Their published case work consistently shows that firms using simulation before capital deployment reduce rework costs by a meaningful margin, often between 15 and 30 per cent on specific projects.

    Manufacturing use cases: where UK firms are seeing the clearest returns

    UK manufacturing has been under sustained pressure: rising energy costs, supply chain fragility, and a persistent skills shortage have all forced operators to be more precise about where they invest. Digital twin technology fits that environment well, because it reduces the cost of being wrong.

    One practical example is factory layout planning. When a Birmingham-based precision components manufacturer wants to reconfigure a production line to accommodate a new product family, traditionally they would hire a consultant, sketch a floor plan, and then implement it with significant disruption. With a digital twin, they can model five different layouts, simulate material flow and labour movement through each, and choose the option that maximises throughput before a single machine is moved.

    Energy modelling is another area attracting serious interest. With industrial energy costs still elevated, firms are using digital twins to simulate the effect of operational changes on consumption. Running a shift pattern differently, adjusting equipment sequences, or identifying idle load can all be tested virtually. The carbon reporting obligations coming down the line from HMRC and Companies House are also nudging businesses to get better data on operational efficiency, and digital simulation supports exactly that kind of audit trail.

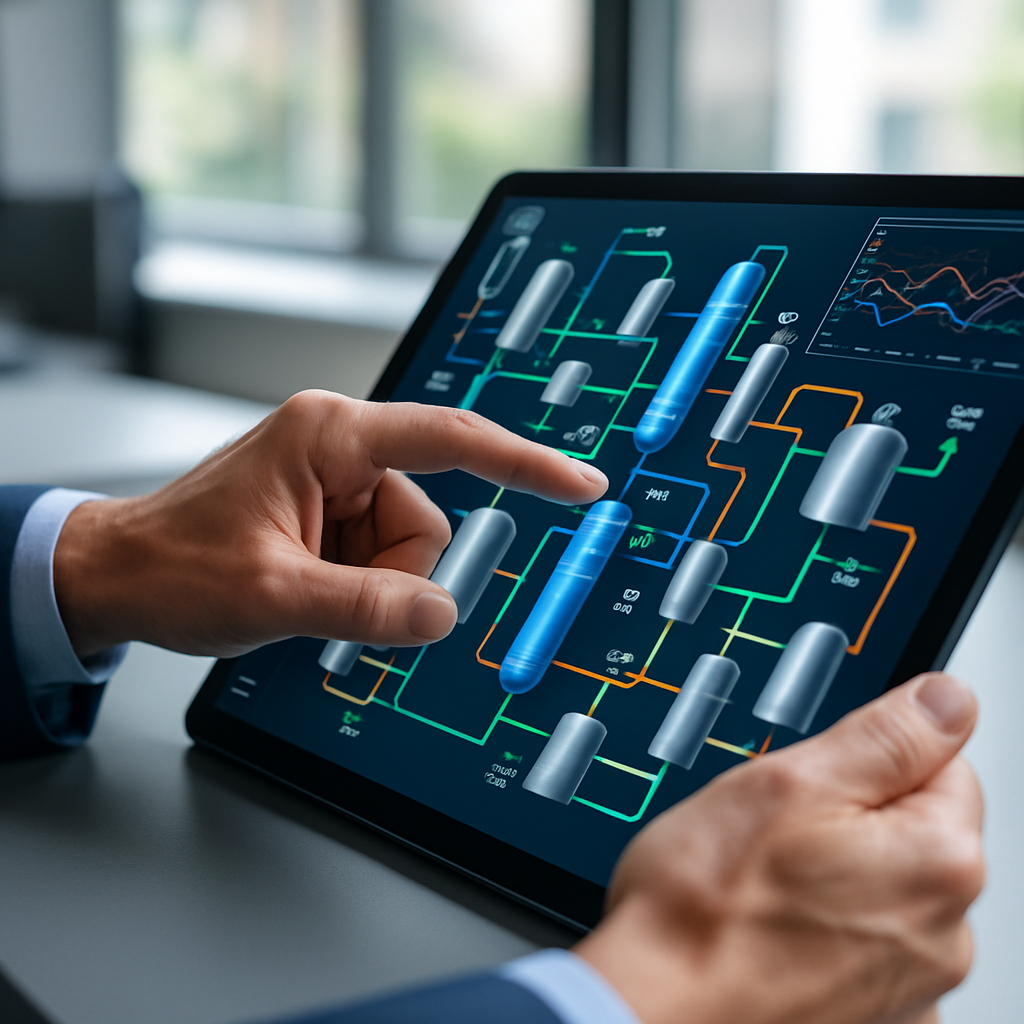
    Close-up of digital twin technology interface showing process simulation data on a touchscreen

    Logistics and supply chain: testing resilience without the risk

    For logistics operators, the appeal is slightly different. The question is not usually about facility layout; it is about decision-making under uncertainty. What happens to your delivery network if a key supplier is delayed by a fortnight? What does rerouting through a different regional hub do to your cost per parcel and your on-time delivery rate?

    Answers to those questions used to come from painful experience. Now they can come from a simulation run over a weekend. Companies including Wincanton and DHL’s UK operations have invested in simulation and digital modelling capabilities precisely because the cost of getting a network decision wrong at scale is too high to accept without prior testing.

    For smaller logistics firms, cloud-based simulation platforms have made this more accessible. Tools built on platforms such as AnyLogic or Simio can be configured without a software engineering team, and several UK resellers now offer managed setups for SMEs at price points that were unimaginable five years ago. The Innovate UK funding guidance lists several active streams that specifically support digital adoption in logistics and supply chain operations.

    Professional services: the less obvious application

    Manufacturing and logistics are the obvious homes for digital twins, but professional services firms are starting to find genuine utility in the concept, even if the implementation looks different. A consultancy or law firm does not have a factory floor, but it does have workflows, capacity constraints, and resource allocation decisions that can be modelled.

    A mid-sized accountancy practice, for example, might build a workflow twin of their tax return processing operation. They can model what happens to turnaround times if they onboard 20 per cent more clients in Q1, or if two senior managers are simultaneously on annual leave during the January deadline crunch. The simulation does not need to be complex to be useful; it just needs to be grounded in real operational data.

    This kind of structured operational thinking also connects to broader conversations about how businesses use technology and data to make better decisions. Some firms approaching this have drawn inspiration from adjacent fields, including the way digital activism has demonstrated that well-modelled, data-driven approaches can produce outcomes that pure intuition consistently misses.

    What stops UK SMEs from adopting digital twin technology faster

    The honest answer is a mix of cost perception, skills gaps, and organisational inertia. Many business owners still assume digital twin projects require a dedicated data science team and a six-figure budget. That was true in 2015. It is far less true now.

    The more persistent barrier is data quality. A digital twin is only as accurate as the operational data feeding it. Firms that have never systematically captured process times, failure rates, or resource utilisation will struggle to build a meaningful model without first doing some groundwork. That groundwork, though, has its own value: the process of preparing data for a simulation often surfaces operational blind spots that businesses did not know they had.

    There is also a change management dimension. Senior teams who have built processes on experience and instinct can be resistant to having a model tell them their assumptions are wrong. The firms getting the most out of digital twin technology tend to be those where leadership has actively championed the approach rather than simply funding it and stepping back.

    Getting started without overcommitting

    The most sensible entry point for most UK mid-market firms is a bounded pilot. Pick one process that is costing you money or causing operational friction, and model only that. A single production line, one logistics route, one client service workflow. The goal is not to build a complete operational twin in year one; it is to demonstrate enough value from a small simulation that the business case for wider adoption becomes self-evident.

    Several UK universities with manufacturing and operations research departments, including Loughborough, Cranfield, and Strathclyde, offer collaborative project programmes that give SMEs access to simulation expertise at reduced cost. These partnerships are underused and worth investigating before committing to a commercial software contract.

    The competitive pressure to make better operational decisions faster is not going away. Digital twin technology gives UK businesses a structured, evidence-based way to do exactly that, and the window for treating it as someone else’s problem is narrowing.

  • Ofcom’s Online Safety Act Duties: What Digital Business Owners in the UK Must Actually Do

    Ofcom’s Online Safety Act Duties: What Digital Business Owners in the UK Must Actually Do

    The Online Safety Act is now firmly in force, and Ofcom is no longer in the mood for vague promises or half-measures. If you run a digital product with user-generated content, a community platform, a marketplace, a forum, a social feature bolted onto a SaaS tool, this legislation applies to you. The question is not whether your business falls under Online Safety Act compliance obligations; for most UK digital founders, it does. The question is what you are actually required to do about it, and how quickly Ofcom will notice if you do not.

    This is not a briefing for household-name social networks. It is for the founders, product owners, and digital operators running smaller platforms who may have quietly assumed this was someone else’s problem. It is not.

    UK digital business founder reviewing Online Safety Act compliance documents at a London office
    UK digital business founder reviewing Online Safety Act compliance documents at a London office

    Who Does the Online Safety Act Actually Cover?

    The Act applies to any service that hosts user-generated content and is accessible to UK users. That scope is broad by design. Ofcom’s own guidance makes clear that this includes forums, review platforms, dating apps, messaging features, comment sections, and online marketplaces where users can post. If your product has any mechanism through which one user can publish content that another user can see, you are almost certainly in scope.

    The legislation creates a tiered structure. Category 1 services are the largest platforms, think Meta, X, YouTube. Category 2 services cover a much wider range of businesses, and this is where most UK founders sit. Within Category 2, there are further distinctions based on functionality. The practical implication: even a modest B2B community platform with a few thousand monthly active users likely has real obligations to fulfil.

    Ofcom publishes a register of Category 1 and Category 2A services, and it is worth checking whether you should be registered. Failure to register when required is itself a compliance breach.

    The Illegal Content Risk Assessment: Your First Real Obligation

    Most in-scope services are required to complete an illegal content risk assessment. This is not a box-ticking exercise. Ofcom expects you to systematically identify the ways in which your platform could be used to share or facilitate illegal content, terrorism, child sexual abuse material, fraud, hate speech, and similar categories, and to document the likelihood and potential impact of each risk given your user base and product design.

    The assessment needs to be proportionate to your service. A small professional networking community carries different risk vectors than a public image-sharing platform. But proportionality does not mean minimal effort. You need to consider your user demographics, your content moderation capabilities, your upload volumes, and the design choices that might attract bad actors.

    Once you have identified risks, you must put in place proportionate measures to mitigate them. Ofcom’s codes of practice provide detailed guidance on what those measures should look like, and while you can depart from the codes, you need to be able to demonstrate that your alternative approach achieves an equivalent standard of protection.

    Content moderation tools used for Online Safety Act compliance on a UK digital platform
    Content moderation tools used for Online Safety Act compliance on a UK digital platform

    User Reporting Mechanisms: Not Optional, Not Cosmetic

    One of the more concrete requirements is the obligation to provide users with a clear, accessible way to report content they believe is illegal or harmful. This has to actually work. A buried link in the footer that opens a broken form is not compliance. Ofcom expects reporting mechanisms to be easy to find, easy to use, and connected to a genuine review process.

    Beyond the mechanics, you need a documented process for handling reports. How quickly do reports get reviewed? Who reviews them? What happens when content is found to violate your terms or the law? What happens when it does not, and the user who reported it disagrees with your decision? These are not rhetorical questions, they are the kinds of questions Ofcom will ask if your platform comes under scrutiny.

    If your platform is likely to be accessed by children, the obligations become significantly heavier. Age assurance, age-appropriate design, and child safety risk assessments layer on top of the baseline requirements. Any founder running an education tool, a creative platform, or a consumer-facing app needs to take this seriously.

    Record-Keeping and Review Cycles

    Compliance under the Online Safety Act is not a one-time task. Ofcom expects services to keep records of their risk assessments, the measures they have put in place, and the decisions they make about content. If your platform changes significantly, new features, new geographies, a step-change in user numbers, your risk assessment should be revisited.

    Build this into your product development cycle. When you plan a new feature that changes how users interact with each other, someone in your team should be asking whether the Online Safety Act obligations need to be reviewed. This is the kind of governance discipline that separates businesses that are genuinely compliant from those that have filed a document and forgotten about it.

    The record-keeping requirement also has a practical upside: if Ofcom ever investigates, your documented evidence of a considered, proportionate approach is your best defence. An absence of records is, from a regulatory perspective, almost as damaging as an absence of measures.

    What Ofcom Enforcement Actually Looks Like

    Ofcom has real teeth here. Fines for non-compliance can reach £18 million or 10% of qualifying global turnover, whichever is greater. For larger platforms in Category 1, senior managers can face criminal liability if they fail to comply with information requests during an investigation. That second point will sharpen minds in boardrooms considerably.

    In practice, Ofcom has signalled it will begin with larger services and work down the register. But that sequencing does not mean smaller operators are invisible. Regulatory investigations can be triggered by complaints, media coverage, or a single serious incident on your platform. The regulator does not need to work through a queue in order to come to you specifically.

    The more prudent approach is to treat your compliance obligations as a genuine operational matter rather than a legal formality. Document your thinking, implement proportionate measures, and revisit them regularly. That is also, incidentally, good product practice.

    Practical Steps for Founders Who Are Not Yet Compliant

    If you have not yet completed your illegal content risk assessment, the immediate priority is to start. Ofcom’s website has detailed guidance and template frameworks that are genuinely useful starting points. Assign ownership clearly, this sits somewhere between your legal, product, and operations functions, and if it belongs to no one specifically, it will be done by no one effectively.

    Audit your user reporting mechanisms. Test them yourself. Ask a colleague who has never used the platform to try reporting something. If they struggle, your users will too, and Ofcom will not be sympathetic to usability excuses.

    If your physical workspace hosts servers or technical infrastructure, you will also have noticed that compliance culture extends into the physical environment. From hygienic flooring in data centres to documented incident response plans, regulated businesses increasingly find that operating standards touch every layer of the business, not just the software.

    Finally, consider whether you need specialist legal advice. The Online Safety Act is detailed, and the codes of practice run to hundreds of pages. For most founders, a few hours with a solicitor who specialises in digital regulation is a worthwhile investment compared to the cost of getting this materially wrong.

    The Bottom Line

    Online Safety Act compliance is not a distant concern for large tech companies. It is a live obligation for any UK digital business operating a platform where users can interact. The regime is structured, the regulator is active, and the penalties are meaningful. Founders who treat this as an operational priority rather than a legal afterthought will be in a considerably stronger position, both with Ofcom and with the users who trust their platforms.

    Frequently Asked Questions

    Does the Online Safety Act apply to small UK businesses with user-generated content?

    Yes. The Act applies to any service that hosts user-generated content accessible to UK users, regardless of company size. Even a small B2B community platform or a SaaS product with a commenting feature is likely to be in scope and should complete an illegal content risk assessment.

    What is an illegal content risk assessment under the Online Safety Act?

    It is a documented exercise in which you identify the ways your platform could be used to facilitate or spread illegal content, assess the likelihood and impact of each risk, and put proportionate measures in place to mitigate them. Ofcom provides codes of practice with detailed guidance on what those measures should look like.

    What are the fines for failing to comply with the Online Safety Act?

    Ofcom can impose fines of up to £18 million or 10% of qualifying global annual turnover, whichever is greater. For the largest Category 1 services, senior managers can also face criminal liability for failing to comply with information requests during an investigation.

    Do I need to register my platform with Ofcom under the Online Safety Act?

    Certain Category 1 and Category 2A services are required to register with Ofcom. You should check Ofcom’s published register and guidance to determine whether your platform meets the threshold. Failing to register when required is itself a compliance breach.

    How often do I need to update my Online Safety Act risk assessment?

    There is no fixed statutory interval, but Ofcom expects assessments to be kept up to date. You should review yours whenever your platform undergoes significant changes, such as new features that alter how users interact, substantial growth in user numbers, or expansion into new markets.