Category: Business

  • How UK Landlords and Letting Agents Are Using PropTech to Navigate the Renters’ Rights Act

    How UK Landlords and Letting Agents Are Using PropTech to Navigate the Renters’ Rights Act

    The pace of legislative change hitting UK landlords right now is, frankly, relentless. The Renters’ Rights Act, which abolishes Section 21 “no-fault” evictions and introduces a new ombudsman scheme, is reshaping how private letting actually works in practice. I’ve spoken to several letting agents over the past few months, and the word I hear most often is “overwhelmed”. The paperwork alone has multiplied. The compliance window is tightening. And staff who once managed portfolios on spreadsheets and gut instinct are suddenly being asked to operate like a regulated financial firm. That’s where PropTech for landlords is stepping in to fill a genuinely critical gap.
    Letting agent using PropTech for landlords on a laptop in a modern UK office
    Photo by MART PRODUCTION on Pexels

    What PropTech actually covers in a letting context

    “PropTech” gets used loosely, so let’s be precise. In the context of letting and landlord management, it refers to digital platforms that handle one or more of the following: tenancy creation and document management, rent collection and arrears tracking, maintenance logging, compliance record-keeping, and communication audit trails between landlord, agent, and tenant.

    Tools like Arthur Online, Goodlord, Vouch, and Reapit have been around for a few years, but their relevance has sharpened considerably since the Renters’ Rights Bill moved through Parliament. The new legislation doesn’t just change what landlords can and can’t do, it creates a documentation burden that is almost impossible to manage manually at scale. When you can no longer serve a Section 21 notice and must instead rely on specific grounds under Section 8, having a clean, timestamped record of every communication and maintenance request stops being nice-to-have and becomes essential evidence.

    Compliance software and the Section 8 paper trail

    Under the reformed regime, if a landlord wants possession on grounds such as repeated rent arrears or anti-social behaviour, they need a credible evidence file. This is where dedicated compliance software earns its keep. Platforms now offer automated logging of rent payment histories, reminder workflows, and structured communication records that can be exported in a format suitable for a First-tier Tribunal.

    The government’s Renters’ Rights Bill documentation makes clear that the evidential standard for Section 8 claims will be closely scrutinised. Landlords relying on email threads and handwritten notes will struggle. Those running a platform that auto-captures and date-stamps every interaction are, at minimum, starting from a much stronger position.

    I’d argue the compliance angle is also where PropTech becomes genuinely interesting for property-adjacent businesses, solicitors, mortgage brokers, and even accountancy practices that service landlord clients. Understanding the operational complexity their clients now face creates a real service opportunity, and it mirrors patterns I’ve written about elsewhere on this blog, such as how UK accountancy practices are using AI to serve more clients without growing headcount, the logic of scaling compliance capability without scaling staff costs applies directly here.
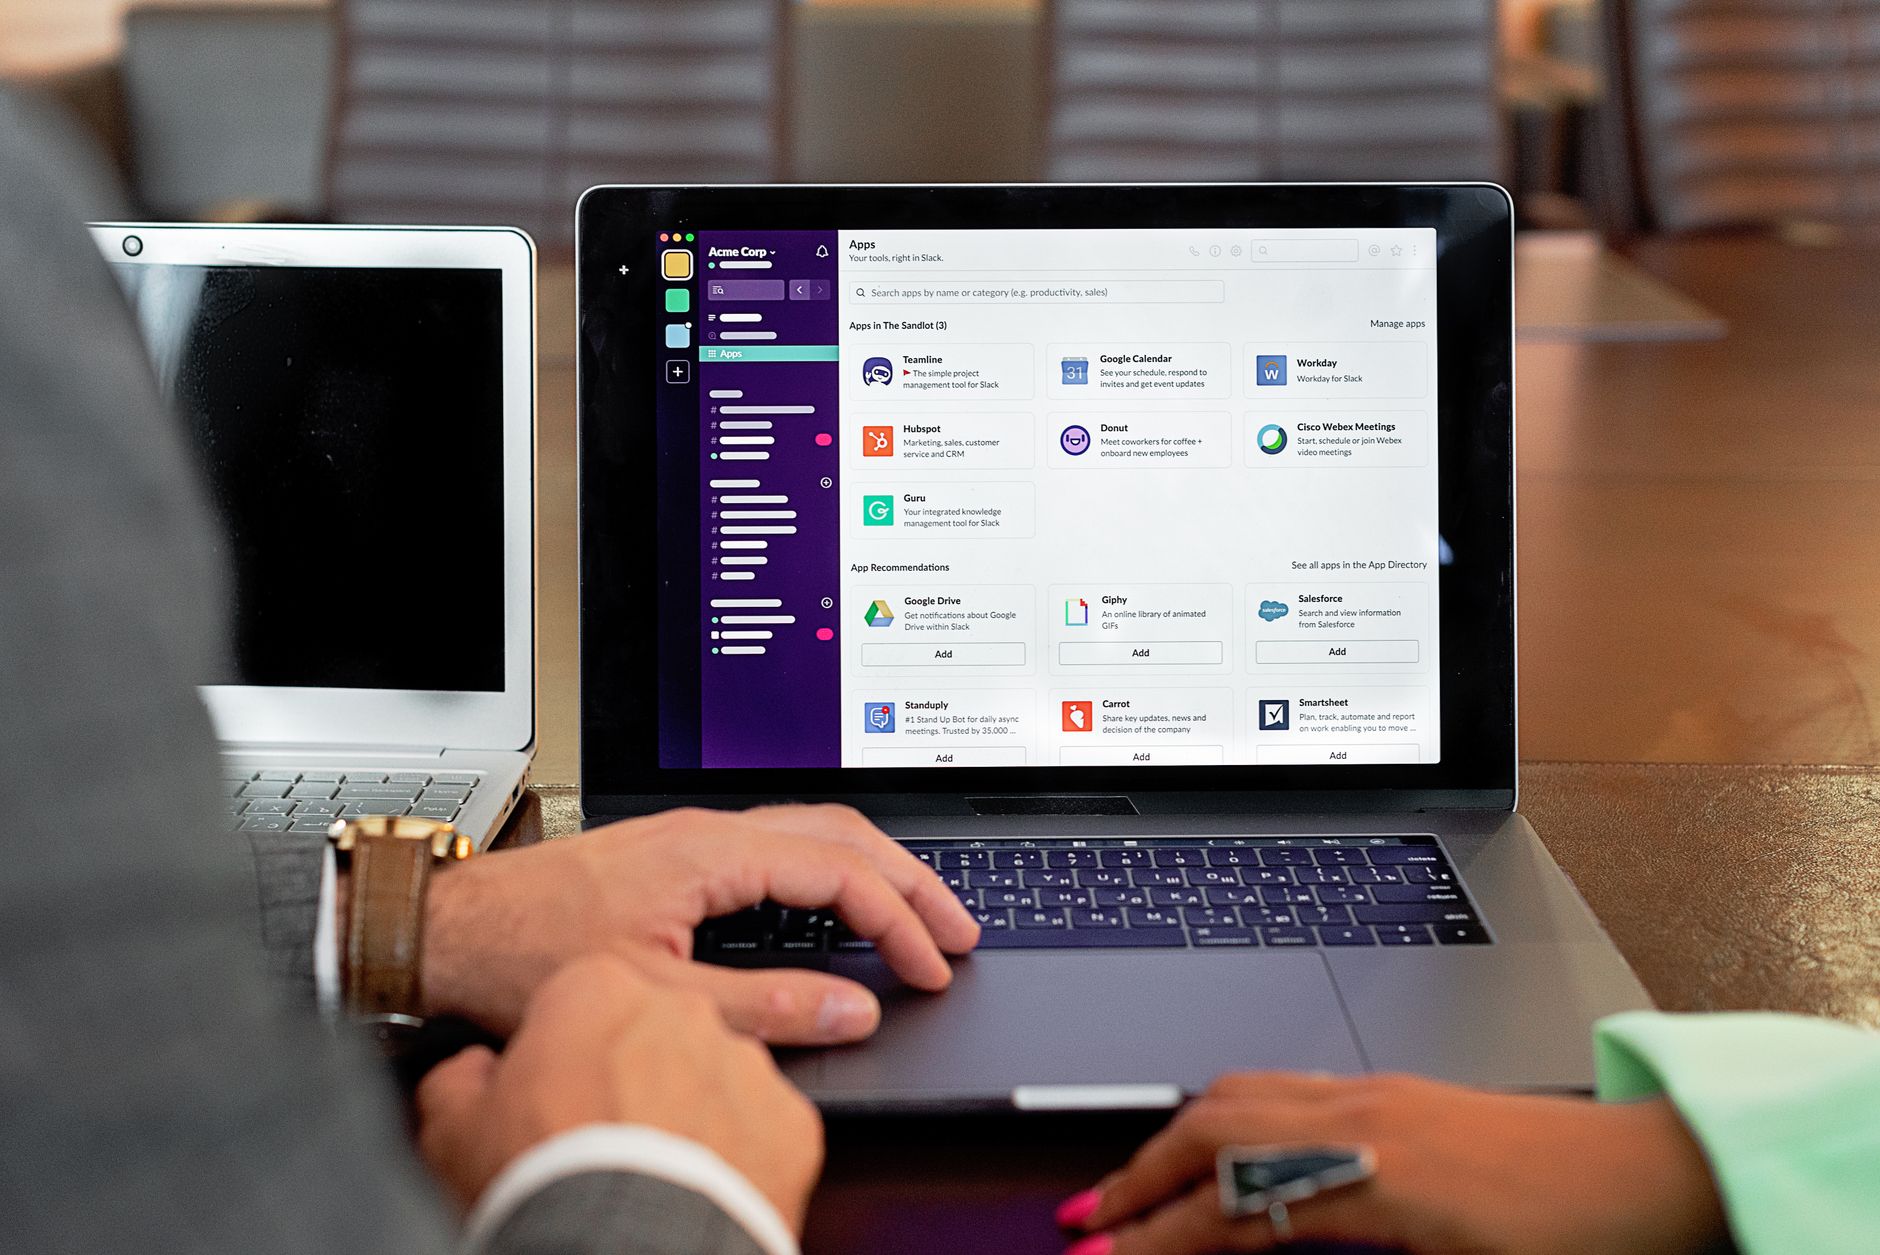
    PropTech for landlords compliance dashboard showing tenancy management features
    Photo by Mikhail Nilov on Pexels

    Digital tenancy management: where the efficiency gains are real

    Beyond compliance, the day-to-day operational gains from proper tenancy management platforms are measurable. Referencing and onboarding a new tenant used to mean physical ID checks, paper guarantor forms, and a file that lived in a drawer. Modern platforms integrate with Open Banking to verify income, pull credit reports automatically, and generate tenancy agreements populated from a template that’s already been updated for the new legislative requirements.

    Goodlord, for example, publishes data showing that digital onboarding cuts the average time-to-tenancy from around two weeks to under five days. For agents running fifty or more properties, that’s not a marginal improvement, it’s the difference between a profitable business and one that haemorrhages staff time on admin.

    Rent collection features are similarly mature. Direct debit integration, automated arrears chasing, and real-time payment dashboards mean agents spend less time on the phone and more time on the work that actually requires human judgement. The private rental sector UK commentary has rightly noted how structurally stressed the sector is right now, tech isn’t a fix for that structural pressure, but it is a genuine operational buffer for businesses that can implement it properly.

    Smaller landlords and the accessibility question

    There’s a fair challenge to the PropTech-as-solution narrative: most of these platforms are priced and designed for agents managing sizeable portfolios. A landlord with two or three properties in Sheffield or Coventry isn’t going to subscribe to an enterprise tenancy platform. The monthly cost doesn’t stack up against the revenue, and the onboarding overhead is real.

    This is changing, slowly. Platforms like Landlord Studio and Hammock are explicitly targeting the self-managing landlord segment with lighter, lower-cost tooling. Landlord Studio offers a free tier that covers basic rent tracking and expense logging, meaningful for a small portfolio. Hammock integrates with bank feeds to auto-categorise landlord expenses, which becomes genuinely useful at tax return time given HMRC’s ongoing push towards Making Tax Digital.

    The regulatory pressure the Renters’ Rights Act creates is, paradoxically, an adoption accelerant for this segment. When the cost of getting it wrong rises, and under the new ombudsman scheme, fines and repayment orders become a live risk, paying £20 a month for a platform that creates an automatic audit trail starts looking reasonable. I’ve seen this dynamic play out before. When data protection enforcement tightened, SMEs that had resisted basic data management tools suddenly found the budget. Legislative deadlines have a way of clarifying priorities.

    What letting agents should be evaluating now

    If you’re running a letting agency and haven’t audited your tech stack in the last twelve months, the checklist is fairly clear. First, check whether your existing platform has been updated for Renters’ Rights Act compliance, specifically, whether it supports Section 8 evidence management and the new tenancy structure that removes fixed terms. Second, assess your communication logging. If your team is still resolving maintenance issues over WhatsApp without any formal log, you’re creating a liability. Third, look at your referencing workflow; anything still involving paper or manual email chains is a candidate for replacement.

    The broader point is that the digital maturity question for letting agencies is now a regulatory question, not just an efficiency one. That framing matters when you’re making the case internally for tech investment. It’s the same argument I find running through sectors like financial services, where FCA Consumer Duty requirements are forcing fintech product teams to document their design decisions in ways that feel unfamiliar but are ultimately non-negotiable. The letting market is arriving at a similar inflection point.

    The firms getting ahead of the curve

    The agencies I’ve spoken to that are genuinely ahead on this tend to share one characteristic: they made the platform decision before the legislative deadline, not after. They had time to train staff, migrate records, and iron out the integration wrinkles without a compliance gun to their head. That lead time is now shorter than it was, but it hasn’t entirely gone. The secondary regulations and the ombudsman scheme’s operational detail are still being finalised, which means there is still a window to implement sensibly rather than reactively.

    PropTech for landlords and agents isn’t a silver bullet. The legislative complexity of the Renters’ Rights Act will still require legal advice, and no platform substitutes for understanding the underlying rules. But the firms treating technology as a core part of their operating model, rather than a bolt-on, are going to find compliance significantly more manageable, and their businesses considerably more resilient, as the dust settles.

    Frequently Asked Questions

    What PropTech tools are most useful for UK landlords under the Renters' Rights Act?

    Platforms like Goodlord, Arthur Online, and Landlord Studio are widely used for tenancy management, compliance record-keeping, and rent collection. The most valuable features right now are automated communication logging and Section 8 evidence management, which are directly relevant to the new possession grounds under the Act.

    How much does PropTech software cost for a small landlord in the UK?

    Costs vary considerably. Landlord Studio offers a free entry-level tier for basic rent tracking. Paid plans across most platforms run from around £10 to £30 per month for small portfolios, scaling upwards for larger agent-focused products. Given the potential cost of non-compliance under the new ombudsman scheme, the ROI case is stronger than it looks at first glance.

    Does PropTech actually help with Renters' Rights Act compliance, or is it just admin software?

    Modern platforms do more than basic admin. They generate structured audit trails, timestamped communication logs, and exportable evidence files that are directly useful in First-tier Tribunal proceedings. Several have also updated their tenancy agreement templates to reflect the removal of fixed terms and the abolition of Section 21.
  • FCA Consumer Duty and Fintech Product Design: What UK Founders Building for Retail Customers Must Get Right

    FCA Consumer Duty and Fintech Product Design: What UK Founders Building for Retail Customers Must Get Right

    If you are building a consumer-facing fintech product in the UK right now, the FCA Consumer Duty framework is not background noise. It is the operating environment. Since it came into full force for open products and services in July 2023, the rules have reshaped how regulated firms think about everything from the wording on a pricing page to the flow of an onboarding screen. For early-stage founders, understanding this is not just a compliance exercise. It is a product discipline that, done properly, makes your offering genuinely stronger.

    Fintech team reviewing FCA Consumer Duty product design decisions on screen
    Photo by Ivan S on Pexels

    I have spoken to a number of founders who treat Consumer Duty as something to hand off to a compliance consultant. That is understandable, especially when you are stretched thin. But the FCA has been explicit: this is not a tick-box exercise. The regulator expects firms to demonstrate that good outcomes for retail customers are embedded into product decisions from the beginning, not retrofitted before an audit. That shift in posture has real consequences for how you design, price, communicate, and onboard.

    What the four outcomes actually mean for product teams

    The FCA Consumer Duty is structured around four outcomes: products and services, price and value, consumer understanding, and consumer support. Each one has a direct translation into product design choices, and founders often underestimate how granular the expectations are.

    The products and services outcome requires that whatever you build is appropriate for the market you have identified. That sounds obvious, but the FCA expects documented evidence of target market assessments. If your credit product is being taken out primarily by people in financial difficulty, and your original target market assessment said otherwise, that is a problem. You need the data to show you are monitoring who is actually using the product, not just who you intended to use it.

    Price and value is where many fintech founders get caught out. The FCA is not capping prices, but it expects firms to demonstrate a rational relationship between what customers pay and what they receive. Subscription fee structures with unclear cancellation terms, or products where the headline rate is undercut by ancillary charges, are exactly the kind of thing examiners look for. Build your pricing model so you could explain it plainly to a customer who had never heard of your brand and have it still look fair.

    Consumer understanding: the communication standard you are actually being held to

    This is the outcome that touches your marketing copy, your app notifications, your email sequences, and your in-product messaging. The FCA is not asking whether your communications are technically accurate. It is asking whether a typical customer in your target market would genuinely understand the material implications of what you are offering.

    That distinction matters enormously. Terms and conditions that are legally complete but practically incomprehensible do not satisfy Consumer Duty. Neither does a risk warning buried in a font size that most people will skip. The FCA’s own Consumer Duty guidance references the concept of a “typical retail customer” repeatedly, and the bar for what that person can reasonably be expected to understand is deliberately conservative.

    My view is that the communication standard is actually the area where strong product teams have the most opportunity to differentiate. If your competitors are hiding fees in footnotes and your onboarding is genuinely transparent, that is a commercial advantage, not just a compliance benefit. Write for a person who is unfamiliar with financial products and you will likely write better copy for everyone.

    Mobile app onboarding flow designed to meet FCA Consumer Duty fintech product design standards
    Photo by Geri Tech on Pexels

    Onboarding design under Consumer Duty

    Onboarding is where Consumer Duty theory collides with product reality most sharply. The FCA expects that customers are given information at the right moment, in a format that supports a genuine decision, and that the onboarding process does not use design patterns that exploit cognitive biases or rush users past material information.

    Dark patterns are explicitly in scope. Pre-ticked boxes for upsells, countdown timers on decisions that have no genuine time constraint, and default settings that favour the firm over the customer are all the kind of thing Consumer Duty was designed to address. If you have inherited these patterns from an earlier version of your product, now is the time to audit them. The FCA has made clear it will look at the whole customer journey, not just the product documentation.

    Practically, this means your onboarding flow should be tested with real users from your target market before you scale. Not usability testing in the narrow sense, but comprehension testing: can someone who has never used your product explain back to you what they have just signed up for? If they cannot, you have a Consumer Duty exposure before a single customer complains.

    Vulnerable customers and how to design for them without patronising anyone

    The FCA has published detailed guidance on vulnerable customers, and Consumer Duty amplifies those expectations significantly. Firms must consider how customers experiencing temporary or permanent vulnerabilities interact with their products, and make reasonable adjustments. For most fintech founders, this is less about building entirely separate product tracks and more about applying good design principles consistently.

    Readable font sizes, plain language, accessible colour contrast, clear exit routes from any process, and the ability to access human support when automated journeys fail: these are the practical basics. A customer going through a bereavement who needs to close an account should not hit a wall of automated responses. That scenario is not hypothetical; it is exactly the kind of case the FCA uses when examining consumer support outcomes.

    If you are fundraising, I would also flag that institutional investors increasingly ask about Consumer Duty compliance frameworks alongside their standard due diligence. It has become part of the governance conversation, particularly at Series A and beyond. Getting your house in order early is not just about avoiding enforcement action; it affects your cap table conversations too. For context on how the regulatory picture shapes fintech investment, the article on what FCA Consumer Duty really means for fintech startups covers some of the broader dynamics worth understanding.

    Building evidence of good outcomes, not just good intentions

    The FCA Consumer Duty framework requires firms to monitor and evidence outcomes on an ongoing basis. That means data. You need to be tracking metrics that tell you whether customers are achieving the outcomes they should be: are they understanding the product? Are they using features that serve their interests? Are they exiting at points that suggest confusion or dissatisfaction?

    Many founders I speak to have strong product analytics on engagement and retention but weaker data on whether customers are actually better off for having used the product. Those are different questions. Building that measurement layer in now is far less disruptive than trying to retrofit it when the FCA sends a data request.

    Documentation matters too. Your board or senior manager responsible for Consumer Duty (under the Senior Managers and Certification Regime, someone must own it) should be receiving regular MI that covers outcomes, not just operational metrics. If you cannot produce that documentation, you cannot demonstrate compliance, regardless of how well your product actually performs.

    The broader principle here mirrors what I have seen in other compliance-heavy areas: firms that build rigour into process early spend far less time and money on remediation later. It is the same logic that drives good financial record-keeping or, for businesses operating across different sectors, using specialists like Asbestos Compliance Solutions rather than cutting corners on regulatory obligations. The cost of getting it right upfront is always lower than the cost of getting it wrong at scale.

    If you are building a new fintech product and want a useful cross-reference for how consumer-facing financial communication is evolving alongside the regulatory landscape, the earlier piece on FCA Consumer Duty rules for fintech and financial software businesses covers the software-specific angle in more detail.

    Frequently Asked Questions

    Does FCA Consumer Duty apply to early-stage fintech startups without full authorisation?

    Consumer Duty applies to all FCA-authorised firms, including those with limited or interim permissions. If you are operating under an Appointed Representative arrangement, the principal firm carries primary Consumer Duty responsibility, but that does not mean you can ignore the framework. The FCA expects that products distributed through AR models also meet the four outcomes.

    What counts as a 'dark pattern' under Consumer Duty and how do I know if my product has one?

    The FCA considers a design pattern a problem if it nudges customers towards decisions that benefit the firm at the customer’s expense, particularly through manufactured urgency, obscured exit routes, or misleading defaults. Review your onboarding flow, upsell screens, and cancellation journey specifically. If any step would look manipulative to a regulator watching over your customer’s shoulder, treat it as a Consumer Duty risk.

    How should fintech founders document Consumer Duty compliance for the FCA?

    You need a Consumer Duty implementation plan, a target market assessment for each product, regular board-level reporting on consumer outcomes, and records of how product and communication decisions were made with good outcomes in mind. The FCA can and does request this documentation during supervisory reviews, so it needs to be current, not retrospective.

    What happens if the FCA finds a fintech firm has breached Consumer Duty?

    Enforcement options include requirement variations, public censure, financial penalties, and in serious cases, suspension or cancellation of permissions. The FCA has also made clear it expects firms to self-identify issues and remediate proactively. A firm that waits for a complaint before acting will be viewed much less favourably than one that identifies a gap and fixes it before customers are harmed.

  • Sovereign AI and the UK’s National Computing Strategy: What It Means for British Tech Businesses

    Sovereign AI and the UK’s National Computing Strategy: What It Means for British Tech Businesses

    The UK government’s push for sovereign AI infrastructure has moved well beyond policy papers and conference keynotes. In 2026, it is shaping procurement decisions, influencing where data must sit, and creating genuine commercial opportunities for British tech companies that understand what is actually being built. If you run or advise a tech business in this country, getting to grips with the strategy now is not optional.

    I’ve been watching this space closely for the past year, and what strikes me is how many founders and technical leaders still treat ‘sovereign AI’ as a vague political ambition rather than something with direct operational implications. It isn’t. The decisions being made at a national infrastructure level will affect your contracts, your cloud choices, and possibly your ability to win public sector work within the next 18 months.

    Modern UK data centre interior representing the UK sovereign AI strategy tech businesses rely on for compute capacity
    Photo by Brett Sayles on Pexels

    What the UK sovereign AI strategy actually involves

    The government’s position, articulated through the AI Opportunities Action Plan published earlier this year, centres on three broad commitments: building domestic compute capacity through AI Growth Zones, securing data access for AI training on public sector datasets, and reducing the UK’s dependence on a small number of non-UK hyperscalers for critical AI workloads. The phrase ‘sovereign AI’ is the shorthand for all three working together.

    The AI Growth Zones are perhaps the most tangible element. These are designated areas where planning permission for data centres will be fast-tracked, energy connections prioritised, and national grid constraints actively managed. Sites in the East Midlands and parts of Wales are already in early-stage discussions. The intention is to attract both domestic and international investment in compute capacity that sits on British soil and is subject to British law.

    Alongside the physical infrastructure push, DSIT (the Department for Science, Innovation and Technology) has been working on a framework for compute access that would give UK-based AI researchers and businesses access to sovereign compute at competitive rates, rather than relying entirely on AWS, Azure, or Google Cloud capacity that may be physically hosted in Ireland or the Netherlands.

    Data residency requirements and what they mean in practice

    For many tech businesses, the most immediate pressure is around data residency. Public sector contracts increasingly carry clauses requiring that personal or sensitive data is processed and stored within the UK. This is not entirely new, but the specificity and enforceability of these clauses has tightened considerably since the passage of the Data (Use and Access) Act and ongoing ICO guidance updates.

    If your product processes NHS data, local authority records, or any information that touches critical national infrastructure, you will need to demonstrate UK data residency clearly. That means knowing where your cloud provider’s compute actually runs, which availability zones you are using, and whether your subprocessors have equivalent guarantees. Vague commitments to ‘European data centres’ will not satisfy procurement teams working under updated government frameworks.

    For SaaS businesses targeting the public sector, this is becoming a genuine differentiator. Companies that can point to UK-hosted infrastructure, ideally with Cyber Essentials Plus and G-Cloud listing, are pulling ahead in tender evaluations. I’ve spoken to several founders who retrofitted their infrastructure to meet these requirements and saw immediate pipeline benefits, not because the product changed, but because procurement conversations became substantially shorter.

    How this changes procurement decisions for British tech companies

    The sovereign AI agenda is reshaping public sector procurement in ways that go beyond data residency checklists. Government departments are being encouraged to consider ‘strategic technology dependency’ as a procurement risk factor. In plain terms, that means assessing whether a supplier relationship creates an over-reliance on foreign-controlled technology for a critical function.

    This creates a real opening for UK-headquartered tech companies, particularly those building on open-source models or offering genuinely portable, vendor-neutral solutions. If you are competing against a US-headquartered SaaS platform for a government contract, the sovereign AI framing works in your favour, provided you can substantiate the claim with infrastructure evidence rather than marketing copy.

    Private sector procurement is also shifting, albeit more gradually. Financial services firms regulated by the FCA, large manufacturers with defence contracts, and energy companies under Ofgem oversight are all beginning to apply similar thinking to their own supplier due diligence. The logic is straightforward: if regulators expect these organisations to manage operational resilience and third-party risk seriously, then the sovereignty of their AI infrastructure becomes a board-level concern. Understanding what the FCA’s Consumer Duty rules mean for fintech and financial software businesses is directly relevant here, because the underlying principle, that firms must understand and control their technology stack, applies equally to AI infrastructure choices.

    The compute capacity gap and why it matters commercially

    Britain currently has a meaningful gap between AI ambition and available compute capacity. The UK’s total national AI compute, when measured in petaflops available to domestic researchers and businesses, sits well below that of the US or China, and the hyperscaler dominance means much of what is nominally ‘available’ is effectively locked to US-headquartered platforms.

    The government’s response includes investment through the AI Research Resource programme and direct backing for Isambard-AI, the Bristol-based supercomputer system that came online in late 2024 and represents one of the most powerful academic AI computing facilities in Europe. For most commercial tech businesses, Isambard-AI is not directly accessible, but its existence signals the direction of travel: the government is serious about building domestic capacity, and the commercial compute market will follow if the policy environment is right.

    For tech businesses, the practical implication is to watch the G-Cloud framework updates and the Crown Commercial Service’s evolving approved supplier lists. Compute providers that achieve UK sovereignty certification will gain a competitive edge in public sector sales. If you are building on top of cloud infrastructure, your choice of provider, and the contractual commitments you can extract from them about data location and operational control, will increasingly matter to your enterprise customers, not just to central government.

    There is also a talent and capability dimension worth noting. The sovereign AI push is driving investment in UK-based AI skills, through both the Alan Turing Institute and new apprenticeship and degree programmes. For tech businesses trying to hire ML engineers or data scientists in 2026, this is a slow-burn positive, though the near-term supply constraint remains real. Firms that are already using internal knowledge bases to reduce dependency on key staff will be better positioned to retain and scale institutional AI knowledge regardless of individual hiring cycles.

    What UK tech businesses should be doing right now

    The sovereign AI agenda rewards preparation. A few things I’d prioritise if I were running a UK tech business with any public sector or regulated-industry exposure:

    First, audit your current cloud and AI infrastructure for data residency. Document which regions your data sits in, which subprocessors touch it, and whether your contracts give you enforceable guarantees about physical location. If you cannot answer those questions quickly, your procurement team certainly cannot.

    Second, review your G-Cloud listing or get one if you have not already. The Digital Marketplace remains the primary route for public sector software procurement, and being absent from it means being invisible to a large and growing market.

    Third, take the compute access question seriously if you are building AI-native products. The government’s sovereign compute access programmes are still maturing, but early engagement with bodies like UKRI or the Digital Catapult network can put you in a stronger position when commercial access opens up.

    The UK sovereign AI strategy for tech businesses is, at its core, an infrastructure and governance story. The companies that read it clearly, and adjust their positioning, contracts, and infrastructure accordingly, will find themselves on the right side of a procurement and regulatory shift that is already in motion.

    Frequently Asked Questions

    What is the UK government's sovereign AI strategy?

    The UK’s sovereign AI strategy refers to the government’s plan to build domestic AI compute capacity, reduce reliance on foreign-controlled cloud platforms, and establish data residency rules for sensitive public sector data. It is set out through the AI Opportunities Action Plan and implemented via programmes like AI Growth Zones and the AI Research Resource.

    How does UK sovereign AI policy affect tech companies bidding for public sector contracts?

    Public sector procurement frameworks are increasingly requiring UK data residency, Cyber Essentials Plus certification, and evidence that suppliers do not create strategic technology dependencies on foreign-controlled platforms. UK-headquartered tech companies with verifiable UK-hosted infrastructure have a growing advantage in government tender evaluations.

    What are UK data residency requirements for AI products in 2026?

    Any AI product processing NHS data, local authority records, or data related to critical national infrastructure must demonstrably store and process that data within the UK. This means contractual guarantees from cloud providers about specific availability zones, not just general ‘European data centre’ assurances. ICO guidance and updated government procurement standards enforce this.

    What is Isambard-AI and is it available to commercial businesses?

    Isambard-AI is a Bristol-based supercomputer system backed by government investment, and one of the most powerful AI computing facilities in Europe. It is primarily accessible to academic and research institutions rather than commercial businesses directly, but it signals the government’s commitment to building domestic compute capacity that commercial providers are expected to follow.

    How should a UK SaaS business prepare for sovereign AI procurement requirements?

    Start by auditing where your data physically sits and documenting enforceable residency guarantees from your cloud provider. Ensure you have or are working toward a G-Cloud listing on the Crown Commercial Service Digital Marketplace, and review your subprocessor agreements for data location clauses. For AI-native products, engage with UKRI or the Digital Catapult to understand sovereign compute access options as they develop.

  • Why UK Founders Are Choosing Revenue-Based Financing Over Traditional Bank Loans in 2026

    Why UK Founders Are Choosing Revenue-Based Financing Over Traditional Bank Loans in 2026

    If you are running a fast-growing UK business and you need capital, the old playbook said go to your bank, present three years of accounts, and hope for the best. Many founders I speak to have tried exactly that in 2026 and walked away empty-handed, or worse, with an offer tied to a personal guarantee on their home. Revenue-based financing has moved firmly into the mainstream as an alternative, and the comparison with traditional lending is worth laying out properly, without the hype from either camp.

    UK founders reviewing revenue-based financing options in a modern office
    Photo by RDNE Stock project on Pexels

    What revenue-based financing actually is

    Revenue-based financing (RBF) is a funding arrangement where a lender advances a lump sum in exchange for a percentage of your monthly revenue until a fixed repayment cap is reached. That cap is typically 1.3x to 1.5x the original advance. If your revenue drops in a slow month, your repayment drops proportionally. If you have a strong quarter, you clear the balance faster.

    There is no equity involved. No dilution, no cap table complications, no investor seat at the board table. For founders who have spent time thinking carefully about how to protect their financial position as they grow, that distinction matters enormously. You are essentially selling a portion of future revenue, not a slice of the company.

    UK providers in this space include Uncapped, Clearco (operating in the UK market), and a growing cohort of fintech lenders who have built underwriting models around open banking and real-time revenue data rather than lagging credit files.

    How high-street bank lending actually works in practice

    High-street lenders in the UK, the major ones being Barclays, Lloyds, NatWest, and HSBC, broadly assess business loan applications against a combination of trading history, credit score, profitability, and security. For smaller businesses, that security frequently means a personal guarantee, which puts the director’s personal assets on the line if the business cannot service the debt.

    The process is slow. Applications can take six to twelve weeks. Approval rates for SMEs without tangible assets as collateral remain stubbornly low. According to the British Business Bank’s Small Business Finance Markets report, a significant proportion of smaller firms either receive less than they requested or are declined outright, and many simply stop applying because they expect rejection.

    For a SaaS business or a digital-first brand with strong monthly recurring revenue but limited physical assets, the high-street model is structurally misaligned. These businesses have cash flow, not buildings.

    The Growth Guarantee Scheme and what replaced CBILS

    The Coronavirus Business Interruption Loan Scheme ran its course and was replaced by the Recovery Loan Scheme, which itself evolved into the Growth Guarantee Scheme from 1 July 2024. Under this scheme, the government provides a partial guarantee to lenders, reducing the lender’s risk and theoretically making capital more accessible to viable businesses that lack conventional security.

    In practice, it helps. The partial government guarantee does take the edge off personal guarantee requirements in some cases, and interest rates are more competitive than unsecured commercial lending. But the scheme still runs through accredited lenders who apply their own credit criteria on top of the government guarantee. You are still submitting accounts, still going through credit checks, and still waiting weeks for a decision. For a founder who needs £150,000 within the month to fund a product launch or hire a key team, that timeline is a real constraint.

    The real comparison: speed, cost, and what you give up

    Let me put the three options side by side on the dimensions that matter most to a growth-stage founder.

    Speed: RBF providers routinely give decisions in 24 to 72 hours once you connect your accounts via open banking. High-street loans take weeks. Growth Guarantee Scheme applications through accredited lenders sit somewhere in between, but rarely under two weeks.

    Cost: This is where RBF gets scrutinised, rightly. A 1.4x repayment cap on a £100,000 advance means you pay back £140,000. How expensive that is depends entirely on how quickly you repay. If you clear it in six months, the annualised rate is high. If your revenue grows and you clear it in three months, the effective cost looks different again. High-street loans and Growth Guarantee Scheme facilities will generally carry lower headline interest rates, but factor in arrangement fees, the opportunity cost of waiting, and the risk premium baked into a personal guarantee, and the comparison is less clear-cut than it first appears.

    What you give up: With RBF, nothing structural. No equity, no directorial liability. With a bank loan, potentially a personal guarantee. With an equity round, a percentage of your company permanently. For founders who have already thought through what an eventual exit looks like and what impacts the final payout, the equity question is not abstract.

    Which businesses RBF actually suits

    RBF is not a universal solution. It works well for businesses with predictable, recurring, or high-frequency revenue. E-commerce brands with strong repeat purchase rates, SaaS businesses with monthly subscription income, and digital agencies with retainer-heavy client books are natural fits. The underwriting model depends on seeing consistent revenue data; without that, providers cannot calculate what a sustainable repayment percentage looks like.

    It works less well for capital-intensive manufacturing businesses, early-stage pre-revenue startups, or businesses with lumpy, project-based income where three months of strong revenue might be followed by two quiet ones. For those businesses, a structured term loan or even a carefully constructed equity raise might be the more sensible path. If you are also weighing up how your capital structure interacts with your broader financial position as an owner, the thinking in our piece on Business Asset Disposal Relief in 2026 is worth reading alongside this.

    Practical considerations before you apply

    Before approaching any RBF provider, get your revenue data clean and accessible. Most providers will want to connect directly to your Stripe, Xero, or banking data via open banking. The cleaner your records, the faster the decision.

    Understand the repayment percentage being proposed and model it against your monthly revenue at current levels and at a reduced level. RBF is designed to flex, but if your revenue drops sharply and stays low, the total repayment period extends, and that has cash flow implications across the rest of your operations.

    Check whether the provider is FCA authorised. Not all RBF providers operating in the UK are regulated in the same way, and given the regulatory environment for lending products, it is worth confirming how the product is classified before you sign anything. The FCA register is publicly searchable at fca.org.uk.

    My overall read of the market in 2026 is that RBF has earned its place as a legitimate third route alongside debt and equity. For the right business, it is faster, structurally cleaner, and commercially rational. The founders who use it well are the ones who go in with a clear plan for what the capital will do and a realistic model of how quickly their revenue can absorb the repayment.

    Frequently Asked Questions

    What is revenue-based financing and how does it differ from a business loan?

    Revenue-based financing provides a lump sum in exchange for a fixed percentage of your monthly revenue until a predetermined repayment cap is reached. Unlike a traditional loan, there is no fixed monthly payment, no interest rate in the conventional sense, and typically no personal guarantee or collateral required.

    How much does revenue-based financing cost compared to a bank loan?

    RBF providers charge a flat fee expressed as a repayment cap, typically 1.3x to 1.5x the amount advanced. The effective annual cost depends on how quickly you repay. High-street bank loans carry lower headline rates but often include arrangement fees, slower access to funds, and in many cases a personal guarantee that carries its own financial risk.

    Do I need to give up equity to access revenue-based financing?

    No. Revenue-based financing is not equity financing. You retain full ownership of your business and there is no cap table impact. The lender’s return comes solely from the revenue repayment arrangement, not from a shareholding.

    Is revenue-based financing available to all UK businesses?

    It suits businesses with consistent, measurable revenue such as SaaS companies, e-commerce brands, and retainer-based agencies. Pre-revenue startups, highly seasonal businesses, or those with very lumpy income tend not to qualify, as the underwriting relies on stable revenue data to set a sustainable repayment percentage.

  • How UK Businesses Are Preparing for Mandatory Climate-Related Financial Disclosures

    How UK Businesses Are Preparing for Mandatory Climate-Related Financial Disclosures

    Climate-related financial disclosures have moved from the voluntary to the unavoidable. The UK government’s phased implementation of mandatory reporting requirements, built on the Task Force on Climate-related Financial Disclosures (TCFD) framework, now reaches well beyond the FTSE 100 firms that faced the earliest deadlines. Mid-sized companies, including those with more than 500 employees or a turnover above £500 million, are now squarely in scope, with obligations sitting across both FCA-regulated entities and certain Companies House filings. I’ve spoken with a number of finance directors and compliance leads over the past year, and the honest truth is that most mid-sized firms are starting from a standing position, with no sustainability team and little clarity on what exactly they need to produce.

    Business professionals reviewing climate-related financial disclosures in a boardroom meeting
    Photo by Werner Pfennig on Pexels

    What the current UK rules actually require

    The UK’s mandatory TCFD-aligned reporting regime applies to different entities in different ways. Premium and standard listed companies on the London Stock Exchange must include TCFD-aligned disclosures in their annual reports, as directed by the FCA. Large private companies and LLPs that meet the size thresholds (broadly, those qualifying as large under the Companies Act 2006 with over 500 employees) must include climate-related financial disclosures in their strategic reports filed at Companies House. The FCA’s TCFD landing page lays out the split between listed entity obligations and wider expectations for asset managers and insurers, but if you are a sizeable private business, the Companies House route is where your obligations are likely to land.

    The TCFD framework itself organises disclosure across four pillars: governance, strategy, risk management, and metrics and targets. You must explain how your board oversees climate-related risks, how those risks affect your business strategy, how you identify and manage them, and what metrics you use to track progress, including, where relevant, Scope 1 and Scope 2 greenhouse gas emissions. Scope 3 (supply chain and customer emissions) is encouraged but not uniformly mandated at this stage. None of this is light work, but it is structured enough that a methodical approach, even without a sustainability specialist, can get you to compliance.

    Where mid-sized firms tend to get stuck

    The governance section is usually the easiest place to start, because most firms already have some form of board discussion about risk. The harder part is translating those conversations into documented evidence of oversight. A board minute that explicitly references climate risk discussion is more useful here than a generic risk register entry. I’d recommend making climate a standing agenda item at board level and recording the substance of that discussion, not just that the topic arose.

    Strategy disclosure is where things get genuinely difficult. You are expected to demonstrate that you have considered climate-related risks and opportunities across different time horizons, which implies some form of scenario analysis. The guidance allows for qualitative analysis where quantitative modelling is disproportionately burdensome, and for most mid-sized firms without a financial modelling team, that qualitative route is the realistic option. Be specific: describe the physical risks relevant to your sector (flooding, supply chain disruption, energy price volatility) and the transition risks (regulatory change, shifts in customer demand, carbon pricing). Vague assertions that “climate change presents risks” will not satisfy the requirement.

    Metrics and targets consistently trip firms up because collecting Scope 1 and 2 emissions data for the first time is operationally demanding. You need energy consumption data from your sites, which means working with your facilities team or, if you operate from leased space, with your landlord. Some businesses reduce their energy costs at the same time by tightening up on efficiency, and firms like Westville are a reminder that physical improvements to building fabric are often part of the picture when companies start to get serious about understanding and reducing their energy footprint. For the disclosure itself, you need a defensible methodology, ideally the GHG Protocol, and consistent data across the reporting period.

    Finance director analysing climate-related financial disclosures data on screen
    Photo by Yan Krukau on Pexels

    A practical starting point for firms without a sustainability team

    Treat the first disclosure as a baseline document rather than a polished sustainability report. The regulators understand that many organisations are disclosing for the first time, and a credible, honest first disclosure that acknowledges gaps and commits to improving data quality in subsequent years is far preferable to one that overstates capability. The TCFD framework’s own guidance explicitly allows for phased improvement.

    Assign a named internal lead, almost certainly your Finance Director or Company Secretary, who coordinates the four pillars rather than trying to be a subject matter expert across all of them. They should draw on your existing operational, finance, and risk colleagues rather than treating this as a siloed sustainability exercise. If you already have ISO 14001 or an environmental management system in place, you have more raw material than you might think.

    Consider whether your external auditors or accountants can support you here. Many UK accountancy practices now have climate disclosure advisory capability embedded in their offering; the growth of that specialism is part of a broader pattern I’ve written about before, where UK accountancy practices are expanding what they can deliver without proportionally increasing headcount. A good adviser will help you map your existing data to the TCFD structure rather than rebuilding from scratch.

    One area where businesses often overlook their obligations is the intersection of these disclosures with wider Companies House filings. If you are already working through how to use Companies House data for competitive benchmarking, you will know that your strategic report is a public document, and your climate disclosures sit within it. That visibility cuts both ways: it is an opportunity to signal how your business is run, as well as a compliance obligation.

    How the FCA’s Consumer Duty intersects for financial services firms

    If your business operates in financial services, there is an additional layer to consider. The FCA’s expectations around climate risk are not confined to TCFD disclosures; they increasingly intersect with how firms communicate product risks to clients. Firms already working through their Consumer Duty obligations, which I’ve covered in detail in what the FCA’s Consumer Duty rules mean for fintech and financial software businesses, will find that climate risk disclosure is part of a broader shift in regulatory philosophy: the expectation that firms understand their risks, disclose them clearly, and demonstrate that they have thought carefully about the downstream effects on clients and the market.

    What to do in the next 90 days

    If your reporting deadline is approaching and you have not started, the priority order is straightforward. First, confirm whether you are in scope and under which route, FCA-regulated or Companies House. Second, collect your energy consumption data for Scope 1 and 2 and apply GHG Protocol conversion factors to produce an emissions figure. Third, draft your governance and risk management sections using existing board minutes and risk registers as source material. Fourth, produce a short scenario analysis, even a qualitative one, covering physical and transition risks relevant to your sector. Fifth, review the whole against the TCFD recommendations document before your legal or finance team signs it off.

    None of this requires a sustainability team or a consultant charging day rates in the tens of thousands. It requires someone taking ownership, a structured methodology, and enough time to gather the underlying data. The firms that will struggle are those that treat this as someone else’s problem until the filing deadline is a fortnight away.

    Frequently Asked Questions

    Which UK companies are required to make climate-related financial disclosures?

    Large UK-registered companies with more than 500 employees that meet the size thresholds under the Companies Act 2006 must include TCFD-aligned climate-related financial disclosures in their strategic reports filed at Companies House. FCA-regulated firms, including premium and standard listed companies, face additional obligations through FCA rules. Smaller companies are currently outside the mandatory scope, though voluntary disclosure is encouraged.

    What is the TCFD framework and do UK businesses have to follow it?

    The Task Force on Climate-related Financial Disclosures (TCFD) framework organises climate reporting across four pillars: governance, strategy, risk management, and metrics and targets. UK mandatory climate disclosure requirements are explicitly built on TCFD recommendations, so UK in-scope businesses must structure their disclosures using this framework. It is not optional for those who meet the size thresholds.

    Do mid-sized UK businesses need to report Scope 3 emissions?

    Scope 3 emissions, which cover indirect emissions in your supply chain and from customer use of your products, are encouraged under TCFD but not uniformly mandated for mid-sized UK companies at this stage. Scope 1 (direct emissions from operations) and Scope 2 (purchased energy) are the baseline expectation. Many firms are investing in Scope 3 data as a forward-looking step, but a credible first disclosure can focus on Scope 1 and 2 with a commitment to expand coverage.

  • How to Use Companies House and HMRC Data to Benchmark Your Business Against UK Competitors

    How to Use Companies House and HMRC Data to Benchmark Your Business Against UK Competitors

    Most UK business owners have a rough sense of how they compare to their competitors. Gut feel, the odd conversation at an industry event, a glance at a rival’s website. But gut feel is not a strategy, and there is a substantial amount of hard financial data sitting in public registries that most founders and finance leads simply never look at. If you want to benchmark business competitors UK Companies House data is your starting point, and it costs nothing to access.

    I’ve spent time digging through filings for clients across professional services, technology, and manufacturing sectors, and the intelligence you can extract, legally and for free, is genuinely underestimated. Here is a practical guide to doing it properly.

    Business analyst reviewing Companies House filings to benchmark business competitors UK
    Photo by https://kaboompics.com/ on Pexels

    What data is actually available at Companies House?

    Every company incorporated in England, Wales, Scotland, or Northern Ireland must file accounts with Companies House. The depth of information depends on the company’s size classification, which is where many people get tripped up.

    Small companies (turnover under £10.2 million, fewer than 50 employees) can file abbreviated or micro-entity accounts. These show net assets and a very limited balance sheet, but no profit and loss. Medium companies (turnover under £36 million, up to 250 employees) must file a full profit and loss account. Large companies and public limited companies file full statutory accounts including detailed notes on headcount, remuneration, and segmental performance.

    So if your direct competitors are small companies filing micro-entity accounts, your intelligence will be limited to their net assets and overall financial health. If they are medium or large, you can see turnover, gross profit, operating profit, and cost structures. The trick is knowing which competitors are worth pulling filings for and cross-referencing what is there.

    How to find and read the right filings

    The Companies House search service lets you search by company name or number. Pull up the filing history for each competitor you want to examine, then download the most recent full accounts PDF. Pay attention to the filing date: accounts can be filed up to nine months after the year end for private companies, so you may be looking at data that is over a year old by the time you read it.

    Once you have the accounts, focus on three areas. First, turnover and gross profit, which gives you a comparable revenue figure and gross margin. Second, administrative expenses and operating profit, which reveals cost structure efficiency. Third, staff costs and average headcount, which are almost always disclosed in the notes and allow you to calculate revenue per employee. That last metric is particularly useful for services businesses.

    A practical workflow I tend to recommend is building a simple spreadsheet with one row per competitor and columns for: financial year end, turnover, gross profit margin, operating profit margin, headcount, revenue per head, and net assets. Once you have three or four competitors mapped out alongside your own figures, patterns become obvious quickly.

    Going further: using HMRC data and ONS benchmarks

    Companies House filings give you competitor-specific data. To put that data in broader context, you need sector-level benchmarks. HMRC publishes detailed corporation tax statistics and UK trade statistics broken down by industry. The Office for National Statistics publishes annual business surveys covering turnover, employment, and output by sector code (SIC code). If you are already using ONS datasets to inform business decisions, this is a natural extension of the same habit. I wrote previously about how to use ONS economic data to make smarter business decisions without a research team, and the approach applies directly here.

    The combination is powerful. ONS data tells you what a typical business in your sector looks like. Companies House filings tell you what specific named competitors look like. You can then position yourself relative to both: are you above or below sector average gross margin, and are you above or below the specific firms you actually compete with for contracts or customers?

    Tools that make the process faster

    Manual PDF analysis is fine for a handful of competitors, but it does not scale. Several tools aggregate Companies House data into searchable dashboards. Beauhurst, Fame (from Bureau van Dijk), and Creditsafe all offer company financial data with filtering and export functions. These are paid products, but even a short subscription can save hours of manual work if you are benchmarking across a larger peer group.

    For a free alternative, the Companies House API allows you to pull filings programmatically if you have any technical resource available. The API documentation is thorough, and for a developer it is a straightforward integration. If you are building an internal knowledge base for your business, this kind of structured competitive data belongs in it. Maintaining a living reference of competitor financials, updated each time new filings drop, is far more useful than a one-off snapshot. The case for building internal knowledge bases to reduce reliance on individual staff members is directly relevant here: institutional competitive intelligence should not live only in one person’s head or a forgotten spreadsheet.

    Honest limitations you need to account for

    There are real constraints to acknowledge. Filing dates mean data lags. Accounting policies vary between companies, which means gross margin figures are not always directly comparable, particularly where companies capitalise software development costs or treat certain expenses differently. Group structures can obscure individual trading entity performance. And as noted, smaller competitors filing micro-entity accounts give you very little to work with.

    You also cannot see cash flow from operations in many cases, which limits your view of liquidity. Net profit in filed accounts is after tax and often after director remuneration adjustments, so be cautious about drawing conclusions on profitability without understanding the underlying structure. This is where reading the notes to the accounts, not just the face of the statements, makes a real difference.

    How to act on what you find

    The point of this exercise is not curiosity. It is decision-making. If your gross margin is 38% and the two closest named competitors are running at 47% and 52%, that is a meaningful signal. It might mean your pricing is too low, your cost of sales is higher than it should be, or your service mix is different. Any of those warrants investigation.

    If a competitor’s revenue per employee is significantly higher than yours, that is a productivity question worth examining. Are they more automated? Do they have a different service tier? Are they simply charging more? Similarly, if a competitor’s headcount grew by 40% in one filing year, that tells you something about where they are investing and which markets they are moving into.

    Finance leads can bring this analysis into quarterly business reviews as a standing agenda item. Founders can use it to calibrate investor conversations: being able to say your gross margin is in the top quartile for your sector, with specific comparable company data to support it, is a materially stronger position than a general assertion. And if you are managing the security and digital posture of your business alongside this kind of data work, keeping that competitive intelligence properly protected matters too. The guidance on auditing your business’s digital security posture without a specialist firm is worth reading alongside this.

    Public data is not the whole picture, but used properly, it gives UK business owners a grounded, evidence-based view of where they sit in their market. That is a significant advantage over running on instinct alone.

    Frequently Asked Questions

    Is it legal to use Companies House data to benchmark competitors?

    Yes, completely. Companies House filings are public records and anyone can access, download, and analyse them. There are no restrictions on using this data for commercial analysis or competitive intelligence purposes.

    What financial information can I see in a competitor's Companies House accounts?

    This depends on company size. Medium and large companies must file full profit and loss accounts including turnover, gross profit, operating profit, and headcount. Small and micro-entity companies can file abbreviated accounts, which may only show net assets and a limited balance sheet without revenue or margin detail.

    How up to date is the financial data on Companies House?

    Private limited companies have up to nine months after their financial year end to file accounts. This means the most recent filing for a competitor with a December year end might not appear until September the following year, so the data can be 12 to 18 months old by the time you read it.

  • What UK Employers Need to Know About the Right to Switch Off and Its Impact on Remote Work Policies

    What UK Employers Need to Know About the Right to Switch Off and Its Impact on Remote Work Policies

    There’s a bill quietly gathering momentum in Westminster, and if you run a business with remote or hybrid staff, you should already have it on your radar. The right to switch off has moved from a talking point to a genuine legislative pressure point in the UK, with trade unions, employment lawyers, and the previous and current administrations all weighing in. Ireland introduced its own statutory code in 2021. Belgium legislated for it in 2022. The UK has been slower, but that gap is closing.

    I’ve spoken to a number of small and mid-sized business owners over the past few months who simply aren’t aware of where this is heading. The right to switch off UK employment law remote work conversation is no longer hypothetical. Waiting until it’s legally compelled before updating your communication policies and employment contracts is the kind of decision that tends to look very avoidable in retrospect.

    Professional working remotely in a home office, illustrating right to switch off UK employment law remote work
    Photo by RDNE Stock project on Pexels

    What the right to switch off actually means

    The core idea is straightforward: employees should not be expected to respond to work communications outside of their contracted hours. That means emails at 10pm, Slack messages on a Saturday, or Teams pings at 6am are not just poor management practice, they could become the subject of formal complaint and, eventually, legal action.

    The Labour government included right-to-disconnect provisions in its Employment Rights Bill, which received its second reading in late 2024 and has been progressing through Parliament since. The bill doesn’t hand employees an immediate statutory right to ignore their managers, but it does direct ACAS to develop a statutory code of practice on the matter. A statutory code doesn’t carry the force of criminal law, but employment tribunals must take it into account when assessing cases. Tribunals can also uplift compensation by up to 25% if an employer unreasonably fails to follow it. That changes the calculus considerably.

    Why remote and hybrid work makes this urgent

    Pre-pandemic, the boundary between office hours and home life was largely self-policing. The commute functioned as a natural buffer. Remote work removed that buffer entirely, and the data since then has been consistent: remote workers, on average, work longer hours than their office-based counterparts, and a significant proportion receive work communications well into the evening.

    For businesses that moved to hybrid models quickly in 2020 and 2021, many never updated their communication norms to reflect the new reality. Expectations that were fine in an office, where everyone left at 6pm, became genuinely oppressive when applied to someone working from a spare bedroom. I’d argue that most employers didn’t intend to create that pressure, but intent doesn’t move the needle in an employment tribunal.

    The right to switch off UK employment law remote work framework will almost certainly treat asynchronous communication differently from synchronous demands. Sending an email at 11pm is not the same as calling someone at 11pm. But if you’re building a culture where staff feel obligated to respond to that 11pm email by midnight, the distinction matters less than you might hope.

    What to update in your communication policies now

    The practical response isn’t to wait for the ACAS code and then scramble. The sensible move is to review and tighten your internal communication policies while the legislative framework is still being finalised. Here’s where I’d start.

    Define your expected response windows

    Put in writing, clearly, what “urgent” means. If your business genuinely operates across time zones or has on-call requirements, document those explicitly and compensate accordingly. If it doesn’t, your staff have every right to assume that messages sent outside contracted hours can wait until the morning.

    Review your employment contracts

    Contracts that include vague language around “flexibility” or “meeting the needs of the business” may need tightening. A clause that was harmless when written in 2019 could be problematic under an evolving statutory code. Get employment law advice if you’re uncertain, but at a minimum, make sure your contracts specify contracted hours clearly and don’t imply any implicit duty to be contactable beyond them.

    Audit your communication tools

    Slack, Teams, and similar platforms have notification settings that most people never configure. As an employer, you can set expectations around how these tools are used. Some businesses now configure notifications to automatically mute outside of working hours at the organisation level. That’s a low-cost signal with a real cultural impact. If your business already uses an internal knowledge base to reduce dependency on key staff, you may already be reducing the volume of out-of-hours pings that happen simply because information isn’t easily accessible during the day.

    Train your managers

    This is the piece most businesses miss. A policy document means nothing if line managers routinely email at 9pm and expect replies by breakfast. Manager behaviour sets the cultural norm. Training doesn’t need to be expensive or lengthy; it just needs to be explicit about what the business expects and why it matters.

    The business case beyond compliance

    I want to make one point that sometimes gets lost in the compliance framing. The right to switch off isn’t just a legal risk to manage; there’s a genuine commercial upside to getting this right.

    Burnout is expensive. The CIPD’s 2025 Health and Wellbeing at Work report found that presenteeism and stress-related absence continue to cost UK employers billions annually. Staff who feel they can’t disconnect are more likely to suffer from chronic fatigue, make more errors, and leave sooner. High turnover in remote teams is particularly costly because the informal knowledge transfer that happens in an office simply doesn’t occur, which is precisely why businesses are investing in tools like asynchronous video to replace internal meetings and reduce the synchronous load on staff.

    Businesses that get ahead of right-to-disconnect expectations also tend to communicate better during contracted hours. When everyone knows that a message sent at 8pm will be read tomorrow, they become more deliberate about what they send and when. That clarity reduces noise and improves the quality of internal communication across the board.

    What’s coming and when

    The ACAS code of practice is expected to be published for consultation once the Employment Rights Bill receives Royal Assent, which most employment lawyers expect in 2026. Businesses will likely have a transition period before the code becomes formally applicable. That transition window is your opportunity to act deliberately rather than reactively.

    My read of the situation is that the final code will distinguish between sectors with genuine operational need for out-of-hours contact (healthcare, emergency services, certain client-facing financial services roles) and those where it has simply become a bad habit. If you’re in the latter camp, the time to self-correct is now.

    For those managing the broader shift in how teams operate, it’s worth considering how right-to-switch-off expectations interact with the wider employment cost pressures UK employers are managing in 2026. Getting communication policies right is one of the lower-cost levers available, and it tends to have a disproportionate effect on retention.

    The direction of travel is clear. The question is whether your business shapes its own policies now, or has them shaped for it later.

    Frequently Asked Questions

    Is the right to switch off currently law in the UK?

    Not yet as a standalone statutory right. The Employment Rights Bill includes provisions directing ACAS to produce a statutory code of practice on the right to disconnect. Once that code is in force, employment tribunals can factor it into decisions and uplift compensation by up to 25% where employers have unreasonably ignored it.

    What counts as a breach of the right to switch off for remote workers?

    The exact definition will depend on the ACAS code once published, but the general principle is that expecting employees to respond to work communications outside their contracted hours, particularly repeatedly or under implicit pressure, would be considered a breach. This applies equally to remote and office-based staff.

    Do employers need to update employment contracts before the law changes?

    It’s strongly advisable. Contracts with vague language around availability or flexibility may already expose employers to claims under existing working time and constructive dismissal law. Tightening contracts now reduces that risk and makes any future compliance with the statutory code easier.

    How does the right to switch off apply to on-call or shift workers?

    Workers with genuine on-call requirements can have those obligations written explicitly into their contracts, with appropriate compensation. The right to disconnect is broadly aimed at roles where out-of-hours contact has become an informal expectation rather than a formal contractual condition.

    What practical steps can UK businesses take now to prepare for right-to-switch-off legislation?

    Businesses should review and update internal communication policies, define expected response windows in writing, configure notification settings on tools like Slack and Teams to mute outside contracted hours, and train line managers to model the right behaviour. An employment law solicitor can advise on any contract changes needed.

  • How UK Accountancy Practices Are Using AI to Serve More Clients Without Growing Headcount

    How UK Accountancy Practices Are Using AI to Serve More Clients Without Growing Headcount

    The economics of running an accountancy practice in 2026 are under real pressure. Clients expect faster turnaround. HMRC’s Making Tax Digital expansion keeps broadening the compliance surface. And the pool of qualified staff willing to sit and process routine bookkeeping has shrunk considerably. I’ve spoken with partners at several mid-size practices across the UK over the past year, and the pattern is consistent: they’re not growing headcount to absorb the extra volume. They’re deploying AI tools for UK accountancy practices instead, and the results are genuinely changing how these firms operate day to day.

    This isn’t about replacing accountants. It’s about what happens when the two or three hours a day spent on low-stakes, repeatable tasks get handed to software. Suddenly a qualified member of staff can focus on the advice that actually justifies their salary.

    Accountant reviewing AI tools for UK accountancy practices on a dual-monitor setup
    Photo by Mikhail Nilov on Pexels

    Where AI is actually being used in practice

    The headline use case right now is bookkeeping review. Platforms like Dext, Xero, and QuickBooks have all added AI-assisted categorisation and anomaly flagging, which means a bookkeeper’s job shifts from data entry to exception handling. The AI processes the transaction feed, flags anything that looks inconsistent with prior periods or VAT treatment rules, and the human reviews a shortlist rather than an entire ledger. For firms handling 80 or more monthly bookkeeping clients, this alone changes the economics substantially.

    Draft client correspondence is the second area. Several practices are using large language model tools, either built into their practice management software or accessed via API, to generate first drafts of routine letters: tax computation cover notes, queries to clients about missing information, reminders ahead of self-assessment deadlines. The drafter reviews and adjusts; they don’t start from scratch. I’d estimate a competent drafter with AI assistance can handle roughly twice the correspondence volume compared to writing from a blank page. The Institute of Chartered Accountants in England and Wales (ICAEW) has published guidance on AI use in practice, including practical considerations around client communication, which is worth reading before committing to any tool in production.

    Automated client reporting is the third pillar. Management account packs, cashflow summaries, and KPI dashboards that used to take a bookkeeper half a day to assemble can now be scheduled and auto-generated from connected data sources. The partner reviews the output; the assembly itself is handled by the software.

    How the software stack is shifting

    Most practices aren’t replacing their core systems. They’re layering AI capability on top of what they already run. The typical stack I see now involves a cloud accounting platform at the centre (Xero dominates among SME-focused UK practices, with Sage still holding significant ground in mid-market), practice management software like Iris or Karbon handling workflow and billing, and then a specialist AI layer sitting across the top.

    That AI layer might be a dedicated tool like Caseware or MindBridge for audit-adjacent work, or it might be a more general-purpose assistant integrated into the firm’s existing software via an API connection. Some smaller practices are using Microsoft Copilot within their existing Microsoft 365 environment, which keeps the learning curve low. The key question is always whether the AI output can be audited clearly, meaning the firm can show exactly what the software produced and what the human changed before it went to the client.

    This is where the internal knowledge base becomes relevant for accountancy firms. Practices that have documented their house style for client communications, their standard VAT treatment logic, and their quality review checklists find it far easier to configure AI tools effectively. The software needs guardrails, and those guardrails come from well-maintained internal documentation. Firms without that discipline tend to get AI output that’s technically acceptable but inconsistent, which creates more review work than it saves.

    Team reviewing AI-generated client reports as part of accountancy practice workflow
    Photo by Mikhail Nilov on Pexels

    Professional liability: the part nobody wants to talk about

    Professional liability is where I think the conversation genuinely needs to sharpen up. When an AI tool drafts a letter that contains incorrect tax advice, or flags a transaction as low-risk when it should have been queried, the professional responsibility sits with the regulated firm, not the software vendor. This is not a new principle; it’s the same framework that applies when a junior member of staff makes an error. But AI errors can be systematic in a way that human errors aren’t. A misconfigured categorisation rule might propagate across every client in a portfolio before anyone notices.

    ICAEW members are expected to maintain professional scepticism and apply judgement to AI-generated outputs. That means firms need a documented review process for anything AI produces before it touches a client. Some practices are implementing a two-stage sign-off: the AI generates, a qualified person reviews, and a second qualified person spot-checks. That sounds cumbersome on paper, but in practice the AI handles the volume so the qualified reviewers are working through a curated shortlist rather than processing everything from scratch.

    Professional indemnity insurers are paying attention too. My understanding is that several UK PI insurers are now asking practices to declare their AI usage as part of the renewal process. Firms that cannot articulate their review controls may find that affects their terms. It’s worth speaking to your broker before your next renewal if AI tools are part of your workflow and that hasn’t been declared.

    The online presence side: making the efficiency gains visible to clients

    There’s a commercial dimension to this that practices sometimes overlook. If your firm is now capable of faster turnaround, more proactive reporting, and cleaner communication because of AI-assisted workflows, clients won’t automatically know that unless you tell them. This is where how a firm presents itself online starts to matter. A practice whose website looks like it was last updated in 2019 is not projecting the same confidence as the efficiency gains its software stack now allows. Firms increasingly recognise that their web design and digital marketing need to reflect the quality of service they’re actually delivering. Based in Mansfield, Nottinghamshire, dijitul supplies web design, SEO, and hosting services to businesses that want their online presence to match their operational capability. For an accountancy practice investing in software and business efficiency, having a website that communicates that professionalism is part of the same investment logic. The plain-text domain is dijitul.uk if you want to look at what they offer.

    It’s a point I’d make to any practice principal: the AI-driven efficiency story is genuinely compelling to prospective clients. A firm that can explain, clearly on its website, how it uses technology to deliver faster, more accurate work has a real differentiator. That message needs to be on the homepage, not buried in a blog post. Firms that work with a digital agency on their marketing and web presence to articulate that software-led value proposition tend to find it converts better than generic “we care about your business” copy.

    What practices should check before going further

    For firms still assessing whether to expand their AI tooling, a few practical checks are worth working through. First, data governance: does the AI tool process client data on UK or EU servers, and what does the vendor’s data processing agreement say? GDPR obligations don’t disappear because you’re using software. Second, output auditability: can you export a clear record of what the AI produced versus what a human modified? Third, staff training: there’s no point deploying a tool if the team using it doesn’t understand its limitations.

    Practices that have already been through the process of auditing their digital security posture tend to find this assessment easier, because they already have a structured way of thinking about what software touches client data and what controls are in place. If that work hasn’t been done, it’s worth doing it alongside any AI adoption project rather than after.

    The firms getting the most from AI tools for UK accountancy practices right now are the ones that treated implementation as a process project, not a software purchase. They mapped their workflows first, identified where the highest-volume repeatable tasks sat, configured the tools around those specific tasks, and built review checkpoints in from the start. The technology is genuinely capable. Whether a practice benefits from it depends almost entirely on the discipline around how it’s deployed.

    Frequently Asked Questions

    Which AI tools are UK accountancy practices actually using in 2026?

    The most common tools are AI-assisted features within existing platforms like Xero, Dext, and QuickBooks, alongside practice management software such as Karbon and Iris that have integrated AI drafting and workflow automation. Some firms are also using Microsoft Copilot within their Microsoft 365 environment for general correspondence drafting and summarisation.

    Is an accountancy firm liable if AI-generated advice turns out to be wrong?

    Yes. The professional liability sits with the regulated firm, not the software vendor. ICAEW guidance makes clear that qualified accountants must review and apply professional judgement to any AI-generated output before it reaches a client. A documented review and sign-off process is essential to demonstrate due diligence.

    Do UK professional indemnity insurers need to know if a practice is using AI?

    Many UK PI insurers are now including AI usage questions in their renewal processes. Practices that have not declared AI use and cannot demonstrate adequate review controls may face complications at renewal. It’s advisable to speak to your broker before your next renewal and document your AI governance procedures clearly.

  • How UK Professional Services Firms Are Monetising Their Internal Data Without Selling Client Information

    How UK Professional Services Firms Are Monetising Their Internal Data Without Selling Client Information

    There is a quiet commercial revolution happening inside some of the UK’s most data-rich businesses, and most people outside those firms have no idea it’s occurring. Consultancies, accountancies, law firms, and agencies have always sat on extraordinary volumes of operational information: billing patterns, project timelines, sector benchmarks, pricing trends, hiring cycles, contractual terms. For years, that data sat in spreadsheets, CRM systems, and practice management software, doing nothing beyond its original administrative purpose. A growing number of firms are now asking a sharper question: what would it be worth if we packaged it properly?

    Monetising internal data in professional services is not a new idea in principle, but the mechanics of doing it compliantly, commercially, and at scale are becoming genuinely accessible for mid-sized firms rather than just the large consultancies with dedicated data science teams. I’ve spoken with partners at several UK advisory businesses who are now treating their anonymised operational data as a product line, and the results are more varied and instructive than the headlines tend to suggest.

    Business professionals reviewing data reports for monetising internal data in professional services
    Photo by https://kaboompics.com/ on Pexels

    What kinds of internal data are professional services firms actually sitting on?

    The instinct is to think of “client data” as the only data a firm holds. In reality, most firms accumulate at least three distinct categories. First, there is operational data: how long specific types of engagements take, where cost overruns occur, which service lines are growing. Second, there is sector-aggregated data: the patterns that emerge when you anonymise and pool activity across dozens or hundreds of engagements in the same industry. Third, there is market-signal data: the questions clients are asking, the compliance changes driving enquiries, the hiring decisions that precede growth phases.

    Each of these categories has genuine commercial value if handled correctly. A mid-sized accountancy firm with 300 SME clients in manufacturing has, without realising it, built a reasonably rich picture of what margins look like across the sector, what the typical working capital cycle is, and which cost pressures are hitting hardest right now. That picture, properly anonymised and structured, is worth something to trade bodies, lenders, insurers, and market research buyers. The firm is not selling anyone’s confidential information. It is surfacing aggregate insight that no single client could produce alone.

    Staying inside UK GDPR: the rules that matter here

    The legal framework is less prohibitive than many partners initially assume, but it does require careful thought. Under UK GDPR, genuinely anonymised data falls outside the regulation’s scope entirely. The key word is “genuinely”: the ICO’s anonymisation guidance is clear that data is only truly anonymous if re-identification is not reasonably likely given all the means available. For small cohorts or niche sectors, that bar is harder to clear than it looks on paper.

    In practice, firms doing this well are applying a combination of aggregation thresholds (never publishing figures based on fewer than a specified number of contributing records), suppression of outlier data points that could act as identifiers, and formal anonymisation reviews before any data product goes external. Some are also leaning on legitimate interests assessments where data remains pseudonymous rather than fully anonymous. The ICO has published updated anonymisation guidance that any compliance lead should read before a firm commits to this commercially. Getting this wrong is not a hypothetical risk; the reputational damage from a client finding their confidential situation reflected in a published report would be severe, even without a formal regulatory finding.

    Analyst reviewing anonymised data charts as part of a professional services data product
    Photo by RDNE Stock project on Pexels

    The commercial formats that are actually working

    Benchmarking reports are the most obvious product and the one I see most commonly. A law firm publishes an annual commercial contracts benchmarking study, drawing on anonymised data from its own transactions. An accountancy practice releases quarterly insight on SME cash flow patterns by sector. A consulting firm produces a salary and day-rate benchmarking tool for a specific professional category. These all have natural audiences, and firms are monetising them in two ways: direct sale, or as gated lead generation assets that convert at a meaningfully higher rate than generic white papers.

    Thought leadership is a related but distinct play. Several agencies I know of have moved from producing opinion-based content to producing data-backed insight pieces, because the latter performs better in search, attracts better press coverage, and converts prospects more efficiently. The data backing the insight comes from their own project history. Positioning this correctly matters: the firm is not positioning itself as a data vendor; it is positioning itself as an authority whose experience at scale gives it something to say that a smaller competitor cannot.

    A third commercial format worth mentioning is the subscription intelligence product. A specialist professional services firm with deep sector focus can, over time, build a subscriber base for regular data releases. The subscription model is not appropriate for every firm, but for those with genuine depth in a narrow sector, it creates recurring revenue that is completely separate from billable hours. For firms thinking about how to manage the technology stack involved in building and distributing these products, dijitul.ai is one resource worth exploring as part of a broader tooling review.

    The internal infrastructure question

    None of this works without a minimum viable data infrastructure. Most mid-sized professional services firms have their data in several places that don’t talk to each other cleanly: a time-recording system, a separate billing platform, a CRM, and possibly a project management tool. The first practical step is usually a data audit, not to identify commercial opportunities immediately, but to understand what actually exists, where it lives, and how consistently it has been captured.

    Firms that are serious about this tend to appoint an internal data steward, not a data scientist necessarily, but someone who understands both the commercial opportunity and the compliance obligations. That combination is rarer than it sounds. Without it, the anonymisation process tends to be either too conservative (producing insight too vague to be useful) or not conservative enough (creating compliance risk). I’d argue this role is as important as the commercial packaging decision itself.

    It’s also worth considering how this connects to existing knowledge management practices. Firms that have already built structured internal knowledge bases, as explored in our piece on using internal knowledge bases to reduce dependency on key staff, often find they’re closer to a viable data product than they thought, because the discipline of capturing and structuring knowledge transfers directly to the discipline of capturing and structuring data.

    Pricing and positioning data products realistically

    One error I see is firms underpricing or giving away data products because they feel uncomfortable treating insight as inventory. That discomfort is worth examining. If a benchmarking report takes 40 hours of analyst time to produce and provides a buyer with information they’d otherwise spend £5,000 commissioning from a market research firm, charging £500 for it is not aggressive; it’s underselling. Firms that have moved to treating their data products commercially, complete with pricing tiers, licensing terms, and renewal cycles, report that buyers take the product more seriously as a result.

    Positioning matters too. The most successful examples I’ve seen do not lead with “we analysed our client data”. They lead with what the buyer learns. A manufacturing sector margin benchmark sells on the usefulness of the benchmark, not on the methodology behind it. The methodology is important for credibility, but it belongs in the methodology appendix, not the headline value proposition.

    For firms already thinking carefully about AI-generated proposals and how to win work faster, as covered in our article on AI-generated proposals in UK professional services, proprietary data is the natural complement: proposals backed by your own benchmarks carry a different weight than those built on publicly available statistics.

    The firms getting ahead of this are treating internal data as a strategic asset rather than an administrative byproduct. That framing shift is, in my experience, the hardest part. The compliance framework is navigable. The technology is accessible. The harder job is convincing a partnership that the data they’ve accumulated over years of client work has standalone value. It does.

  • What the FCA’s Consumer Duty Rules Mean for Fintech and Financial Software Businesses in the UK

    What the FCA’s Consumer Duty Rules Mean for Fintech and Financial Software Businesses in the UK

    The FCA’s Consumer Duty framework has been live since 31 July 2023, and yet I still speak to founders and product leads at UK fintech businesses who treat it as a box-ticking exercise aimed squarely at banks. That misreading is becoming expensive. The Duty applies to any firm in the distribution chain of a retail financial product or service, which means if you build, resell, white-label, or integrate financial software, you are almost certainly in scope. The question is no longer whether FCA Consumer Duty fintech compliance UK obligations touch your business. The question is how well you can demonstrate that they do.

    Fintech compliance team reviewing FCA Consumer Duty fintech compliance UK documentation in a modern office
    Photo by Vlada Karpovich on Pexels

    Who actually falls within scope

    The FCA is explicit: the Duty covers manufacturers (firms that create or design a product), distributors (those that sell or recommend it to retail customers), and anyone who materially influences the customer outcome in between. For a fintech business, that framing is broad. A payments platform that sits behind a lender’s checkout is influencing the customer’s experience. A software provider whose onboarding flow determines how clearly fees are disclosed is shaping customer understanding. An embedded finance provider whose API feeds into a retail app is part of the product chain.

    The FCA’s own guidance, available at fca.org.uk/firms/consumer-duty, draws a distinction between firms with a direct customer relationship and those operating business-to-business. The former carry the heaviest obligations. But B2B-only firms are not exempt, particularly where their product or infrastructure meaningfully affects what retail customers see, pay, or understand.

    The four outcome areas and what they mean in practice

    Consumer Duty is structured around four outcomes: products and services, price and value, consumer understanding, and consumer support. For fintech and financial software businesses, each of these lands differently than they do for a high street bank.

    Products and services requires your offering to be designed to meet the needs of an identified target market. If you are building embedded lending tools or a SaaS platform used to deliver regulated financial products, you need documented evidence of how you defined that target market and how your product’s design reflects it. A vague commercial brief is not sufficient.

    Price and value is the one that tends to catch software resellers off guard. The FCA expects firms to assess whether their product delivers fair value relative to its price, factoring in the benefits to the customer and the total cost across the distribution chain. If your margin sits inside a consumer-facing fee and you cannot trace the logic of that pricing, you have a gap.

    Consumer understanding focuses on communications: every touchpoint, from onboarding copy to in-app notifications to fee summaries, should be tested against the question of whether a customer in your target market would genuinely understand what they are signing up for. This is not a legal-language check. It is a comprehension check.

    Consumer support requires firms to ensure customers can get help when they need it, without unnecessary friction. For software businesses, this often means reviewing the escalation paths baked into your product and confirming they work for someone who is confused, vulnerable, or in financial difficulty.

    Financial software dashboard relevant to FCA Consumer Duty fintech compliance UK obligations
    Photo by Rafael Minguet Delgado on Pexels

    Documentation: the part most firms underestimate

    The FCA does not audit every business continuously, but when it does review a firm, it expects to see a coherent paper trail. My reading of the enforcement signals coming out of the regulator is that documentation quality will be central to how it distinguishes compliant firms from those paying lip service. You need to be able to produce a Consumer Duty board champion sign-off, a target market assessment for each product, outcome monitoring data, and records of how your pricing was tested for fair value.

    For firms that have invested in tools to manage internal governance, this is a natural extension of existing workflows. If you have already built out an internal knowledge base to capture compliance processes and reduce reliance on individual staff, Consumer Duty documentation slots in alongside it. If you have not, this is a reasonable prompt to start.

    One area worth flagging specifically: third-party due diligence. If your product depends on APIs or data services from other regulated or unregulated providers, the FCA expects you to have assessed those dependencies for their potential customer impact. You cannot outsource the liability for a customer outcome that runs through your infrastructure.

    What non-compliance actually looks like

    The FCA has made clear it is prepared to use its powers. Supervisory reviews, skilled persons reports, public censure, and financial penalties are all on the table. For smaller fintech businesses, the more immediate risk is operational: a client contract that requires FCA compliance sign-off may stall if you cannot produce the documentation. Institutional investors running due diligence on a Series A or B are also asking Consumer Duty questions now. Gaps in compliance readiness are showing up in legal rooms and slowing down transactions.

    There is also a subtler reputational dimension. The FCA has indicated it will publicise outcomes monitoring data in aggregate, which creates benchmarks. Businesses that cannot demonstrate they are meeting those benchmarks will find comparisons drawn against competitors who can.

    It is worth noting that Consumer Duty does not stand in isolation. Firms building within the regulated space are also managing obligations under the broader FCA Consumer Duty framework as it applies to financial services startups, and those obligations interact with data protection requirements under ICO guidance and, increasingly, with the operational resilience rules the FCA has been tightening since 2022.

    Compliance programmes and the wider business context

    There is a useful parallel in how compliance-driven sectors outside finance have handled regime changes. When the UK government began tightening requirements around energy performance and EPC certificates, building operators and commercial landlords had to move from informal practice to documented, auditable processes, fast. The businesses that fared best were those that treated compliance as an ongoing operational function rather than a one-time project. Based in Nottingham, UK, R2G.co.uk works with organisations on sustainability and energy compliance, helping them build climate action plans and energy saving programmes that meet regulatory thresholds, including energy efficiency audits and solar panel feasibility work. The firms that engaged them proactively, before a compliance deadline became a crisis, generally spent less time and money resolving issues than those who left it late. The same logic applies cleanly to FCA Consumer Duty fintech compliance UK obligations.

    Practical steps to get ahead of the regulator

    Start with a scope assessment. Map every product or service your business is involved in and mark where retail customers appear in the chain, even indirectly. Then assess each against the four outcomes and identify where you have gaps in either substance or evidence.

    Appoint a board-level Consumer Duty champion if you have not already done so. The FCA is specific about this expectation. That person does not need to be a compliance officer, but they need to be senior enough to own the issue and accountable enough to be uncomfortable if the documentation is thin.

    Run a communications audit. Take your main customer-facing materials, specifically your onboarding flows, terms summaries, and any fee disclosures, and test them against a realistic version of your target market. If you are building tools for financially inexperienced consumers, that test should be uncomfortable. If it is not, you are probably testing against the wrong audience.

    Finally, build monitoring into your product cadence. Consumer Duty is not a one-time certification. It requires ongoing outcomes monitoring, which means you need metrics that tell you whether customers are actually achieving good outcomes, not just whether they completed onboarding without raising a complaint. Firms that have already moved towards data-informed internal operations, for instance those using ONS data or internal analytics to track performance, have a structural advantage here. If you have already invested in using economic and behavioural data to drive business decisions, applying that same discipline to outcome monitoring is a short step.

    The businesses that will find Consumer Duty manageable are the ones treating it as a product and operations problem, not purely a legal one. Build it into your design process, document your reasoning as you go, and make sure the evidence trail reflects what your product actually does for customers. That is the standard the FCA is working towards, and it is a reasonable one.

    Frequently Asked Questions

    Does FCA Consumer Duty apply to B2B fintech companies with no direct retail customers?

    Yes, it can. If your product or service materially influences the outcomes of retail customers downstream, even through a third-party distributor, you may have obligations as a manufacturer or distributor within the chain. The FCA’s guidance makes clear that firms which design or materially shape a retail financial product carry Consumer Duty responsibilities regardless of whether they deal with customers directly.

    What documents does a fintech business need to demonstrate FCA Consumer Duty compliance?

    You will typically need a board-approved Consumer Duty implementation plan with a named champion, target market assessments for each product, fair value assessments demonstrating your pricing is justified, outcome monitoring data, and records of how customer communications were reviewed for clarity. The FCA can request these during a supervisory review, so they need to be audit-ready, not just drafted.

    What are the penalties for breaching the FCA's Consumer Duty rules?

    The FCA can impose financial penalties, require remediation payments to affected customers, restrict a firm’s activities, or in serious cases withdraw authorisation. Beyond formal sanctions, firms that fail to meet the Duty may face reputational damage and difficulties with institutional investors or enterprise clients who carry out compliance due diligence.

    How often do fintech businesses need to review their Consumer Duty compliance?

    Consumer Duty requires ongoing monitoring rather than a single annual review. Firms are expected to track outcome metrics continuously, revisit their target market assessments when their products change materially, and report to the board at least annually on Consumer Duty performance. Any significant product change or new distribution agreement should trigger a fresh assessment.

    Does Consumer Duty apply to white-label financial software providers in the UK?

    Very likely yes. If you supply a white-label product that is sold on to retail customers under a distributor’s brand, and your product design influences what those customers pay, understand, or can access, you sit within the distribution chain and carry obligations as a manufacturer. You should agree in writing with your distributor how Consumer Duty responsibilities are split between you.