Category: Business

  • How UK Accountancy Practices Are Using AI to Serve More Clients Without Growing Headcount

    How UK Accountancy Practices Are Using AI to Serve More Clients Without Growing Headcount

    The economics of running an accountancy practice in 2026 are under real pressure. Clients expect faster turnaround. HMRC’s Making Tax Digital expansion keeps broadening the compliance surface. And the pool of qualified staff willing to sit and process routine bookkeeping has shrunk considerably. I’ve spoken with partners at several mid-size practices across the UK over the past year, and the pattern is consistent: they’re not growing headcount to absorb the extra volume. They’re deploying AI tools for UK accountancy practices instead, and the results are genuinely changing how these firms operate day to day.

    This isn’t about replacing accountants. It’s about what happens when the two or three hours a day spent on low-stakes, repeatable tasks get handed to software. Suddenly a qualified member of staff can focus on the advice that actually justifies their salary.
    Accountant reviewing AI tools for UK accountancy practices on a dual-monitor setup
    Photo by Mikhail Nilov on Pexels

    Where AI is actually being used in practice

    The headline use case right now is bookkeeping review. Platforms like Dext, Xero, and QuickBooks have all added AI-assisted categorisation and anomaly flagging, which means a bookkeeper’s job shifts from data entry to exception handling. The AI processes the transaction feed, flags anything that looks inconsistent with prior periods or VAT treatment rules, and the human reviews a shortlist rather than an entire ledger. For firms handling 80 or more monthly bookkeeping clients, this alone changes the economics substantially.

    Draft client correspondence is the second area. Several practices are using large language model tools, either built into their practice management software or accessed via API, to generate first drafts of routine letters: tax computation cover notes, queries to clients about missing information, reminders ahead of self-assessment deadlines. The drafter reviews and adjusts; they don’t start from scratch. I’d estimate a competent drafter with AI assistance can handle roughly twice the correspondence volume compared to writing from a blank page. The Institute of Chartered Accountants in England and Wales (ICAEW) has published guidance on AI use in practice, including practical considerations around client communication, which is worth reading before committing to any tool in production.

    Automated client reporting is the third pillar. Management account packs, cashflow summaries, and KPI dashboards that used to take a bookkeeper half a day to assemble can now be scheduled and auto-generated from connected data sources. The partner reviews the output; the assembly itself is handled by the software.

    How the software stack is shifting

    Most practices aren’t replacing their core systems. They’re layering AI capability on top of what they already run. The typical stack I see now involves a cloud accounting platform at the centre (Xero dominates among SME-focused UK practices, with Sage still holding significant ground in mid-market), practice management software like Iris or Karbon handling workflow and billing, and then a specialist AI layer sitting across the top.

    That AI layer might be a dedicated tool like Caseware or MindBridge for audit-adjacent work, or it might be a more general-purpose assistant integrated into the firm’s existing software via an API connection. Some smaller practices are using Microsoft Copilot within their existing Microsoft 365 environment, which keeps the learning curve low. The key question is always whether the AI output can be audited clearly, meaning the firm can show exactly what the software produced and what the human changed before it went to the client.

    This is where the internal knowledge base becomes relevant for accountancy firms. Practices that have documented their house style for client communications, their standard VAT treatment logic, and their quality review checklists find it far easier to configure AI tools effectively. The software needs guardrails, and those guardrails come from well-maintained internal documentation. Firms without that discipline tend to get AI output that’s technically acceptable but inconsistent, which creates more review work than it saves.
    Team reviewing AI-generated client reports as part of accountancy practice workflow
    Photo by Mikhail Nilov on Pexels

    Professional liability: the part nobody wants to talk about

    Professional liability is where I think the conversation genuinely needs to sharpen up. When an AI tool drafts a letter that contains incorrect tax advice, or flags a transaction as low-risk when it should have been queried, the professional responsibility sits with the regulated firm, not the software vendor. This is not a new principle; it’s the same framework that applies when a junior member of staff makes an error. But AI errors can be systematic in a way that human errors aren’t. A misconfigured categorisation rule might propagate across every client in a portfolio before anyone notices.

    ICAEW members are expected to maintain professional scepticism and apply judgement to AI-generated outputs. That means firms need a documented review process for anything AI produces before it touches a client. Some practices are implementing a two-stage sign-off: the AI generates, a qualified person reviews, and a second qualified person spot-checks. That sounds cumbersome on paper, but in practice the AI handles the volume so the qualified reviewers are working through a curated shortlist rather than processing everything from scratch.

    Professional indemnity insurers are paying attention too. My understanding is that several UK PI insurers are now asking practices to declare their AI usage as part of the renewal process. Firms that cannot articulate their review controls may find that affects their terms. It’s worth speaking to your broker before your next renewal if AI tools are part of your workflow and that hasn’t been declared.

    The online presence side: making the efficiency gains visible to clients

    There’s a commercial dimension to this that practices sometimes overlook. If your firm is now capable of faster turnaround, more proactive reporting, and cleaner communication because of AI-assisted workflows, clients won’t automatically know that unless you tell them. This is where how a firm presents itself online starts to matter. A practice whose website looks like it was last updated in 2019 is not projecting the same confidence as the efficiency gains its software stack now allows. Firms increasingly recognise that their web design and digital marketing need to reflect the quality of service they’re actually delivering. Based in Mansfield, Nottinghamshire, dijitul supplies web design, SEO, and hosting services to businesses that want their online presence to match their operational capability. For an accountancy practice investing in software and business efficiency, having a website that communicates that professionalism is part of the same investment logic. The plain-text domain is dijitul.uk if you want to look at what they offer.

    It’s a point I’d make to any practice principal: the AI-driven efficiency story is genuinely compelling to prospective clients. A firm that can explain, clearly on its website, how it uses technology to deliver faster, more accurate work has a real differentiator. That message needs to be on the homepage, not buried in a blog post. Firms that work with a digital agency on their marketing and web presence to articulate that software-led value proposition tend to find it converts better than generic “we care about your business” copy.

    What practices should check before going further

    For firms still assessing whether to expand their AI tooling, a few practical checks are worth working through. First, data governance: does the AI tool process client data on UK or EU servers, and what does the vendor’s data processing agreement say? GDPR obligations don’t disappear because you’re using software. Second, output auditability: can you export a clear record of what the AI produced versus what a human modified? Third, staff training: there’s no point deploying a tool if the team using it doesn’t understand its limitations.

    Practices that have already been through the process of auditing their digital security posture tend to find this assessment easier, because they already have a structured way of thinking about what software touches client data and what controls are in place. If that work hasn’t been done, it’s worth doing it alongside any AI adoption project rather than after.

    The firms getting the most from AI tools for UK accountancy practices right now are the ones that treated implementation as a process project, not a software purchase. They mapped their workflows first, identified where the highest-volume repeatable tasks sat, configured the tools around those specific tasks, and built review checkpoints in from the start. The technology is genuinely capable. Whether a practice benefits from it depends almost entirely on the discipline around how it’s deployed.

    Frequently Asked Questions

    Which AI tools are UK accountancy practices actually using in 2026?

    The most common tools are AI-assisted features within existing platforms like Xero, Dext, and QuickBooks, alongside practice management software such as Karbon and Iris that have integrated AI drafting and workflow automation. Some firms are also using Microsoft Copilot within their Microsoft 365 environment for general correspondence drafting and summarisation.

    Is an accountancy firm liable if AI-generated advice turns out to be wrong?

    Yes. The professional liability sits with the regulated firm, not the software vendor. ICAEW guidance makes clear that qualified accountants must review and apply professional judgement to any AI-generated output before it reaches a client. A documented review and sign-off process is essential to demonstrate due diligence.

    Do UK professional indemnity insurers need to know if a practice is using AI?

    Many UK PI insurers are now including AI usage questions in their renewal processes. Practices that have not declared AI use and cannot demonstrate adequate review controls may face complications at renewal. It’s advisable to speak to your broker before your next renewal and document your AI governance procedures clearly.
  • How UK Professional Services Firms Are Monetising Their Internal Data Without Selling Client Information

    How UK Professional Services Firms Are Monetising Their Internal Data Without Selling Client Information

    There is a quiet commercial revolution happening inside some of the UK’s most data-rich businesses, and most people outside those firms have no idea it’s occurring. Consultancies, accountancies, law firms, and agencies have always sat on extraordinary volumes of operational information: billing patterns, project timelines, sector benchmarks, pricing trends, hiring cycles, contractual terms. For years, that data sat in spreadsheets, CRM systems, and practice management software, doing nothing beyond its original administrative purpose. A growing number of firms are now asking a sharper question: what would it be worth if we packaged it properly?

    Monetising internal data in professional services is not a new idea in principle, but the mechanics of doing it compliantly, commercially, and at scale are becoming genuinely accessible for mid-sized firms rather than just the large consultancies with dedicated data science teams. I’ve spoken with partners at several UK advisory businesses who are now treating their anonymised operational data as a product line, and the results are more varied and instructive than the headlines tend to suggest.

    Business professionals reviewing data reports for monetising internal data in professional services
    Photo by https://kaboompics.com/ on Pexels

    What kinds of internal data are professional services firms actually sitting on?

    The instinct is to think of “client data” as the only data a firm holds. In reality, most firms accumulate at least three distinct categories. First, there is operational data: how long specific types of engagements take, where cost overruns occur, which service lines are growing. Second, there is sector-aggregated data: the patterns that emerge when you anonymise and pool activity across dozens or hundreds of engagements in the same industry. Third, there is market-signal data: the questions clients are asking, the compliance changes driving enquiries, the hiring decisions that precede growth phases.

    Each of these categories has genuine commercial value if handled correctly. A mid-sized accountancy firm with 300 SME clients in manufacturing has, without realising it, built a reasonably rich picture of what margins look like across the sector, what the typical working capital cycle is, and which cost pressures are hitting hardest right now. That picture, properly anonymised and structured, is worth something to trade bodies, lenders, insurers, and market research buyers. The firm is not selling anyone’s confidential information. It is surfacing aggregate insight that no single client could produce alone.

    Staying inside UK GDPR: the rules that matter here

    The legal framework is less prohibitive than many partners initially assume, but it does require careful thought. Under UK GDPR, genuinely anonymised data falls outside the regulation’s scope entirely. The key word is “genuinely”: the ICO’s anonymisation guidance is clear that data is only truly anonymous if re-identification is not reasonably likely given all the means available. For small cohorts or niche sectors, that bar is harder to clear than it looks on paper.

    In practice, firms doing this well are applying a combination of aggregation thresholds (never publishing figures based on fewer than a specified number of contributing records), suppression of outlier data points that could act as identifiers, and formal anonymisation reviews before any data product goes external. Some are also leaning on legitimate interests assessments where data remains pseudonymous rather than fully anonymous. The ICO has published updated anonymisation guidance that any compliance lead should read before a firm commits to this commercially. Getting this wrong is not a hypothetical risk; the reputational damage from a client finding their confidential situation reflected in a published report would be severe, even without a formal regulatory finding.

    Analyst reviewing anonymised data charts as part of a professional services data product
    Photo by RDNE Stock project on Pexels

    The commercial formats that are actually working

    Benchmarking reports are the most obvious product and the one I see most commonly. A law firm publishes an annual commercial contracts benchmarking study, drawing on anonymised data from its own transactions. An accountancy practice releases quarterly insight on SME cash flow patterns by sector. A consulting firm produces a salary and day-rate benchmarking tool for a specific professional category. These all have natural audiences, and firms are monetising them in two ways: direct sale, or as gated lead generation assets that convert at a meaningfully higher rate than generic white papers.

    Thought leadership is a related but distinct play. Several agencies I know of have moved from producing opinion-based content to producing data-backed insight pieces, because the latter performs better in search, attracts better press coverage, and converts prospects more efficiently. The data backing the insight comes from their own project history. Positioning this correctly matters: the firm is not positioning itself as a data vendor; it is positioning itself as an authority whose experience at scale gives it something to say that a smaller competitor cannot.

    A third commercial format worth mentioning is the subscription intelligence product. A specialist professional services firm with deep sector focus can, over time, build a subscriber base for regular data releases. The subscription model is not appropriate for every firm, but for those with genuine depth in a narrow sector, it creates recurring revenue that is completely separate from billable hours. For firms thinking about how to manage the technology stack involved in building and distributing these products, dijitul.ai is one resource worth exploring as part of a broader tooling review.

    The internal infrastructure question

    None of this works without a minimum viable data infrastructure. Most mid-sized professional services firms have their data in several places that don’t talk to each other cleanly: a time-recording system, a separate billing platform, a CRM, and possibly a project management tool. The first practical step is usually a data audit, not to identify commercial opportunities immediately, but to understand what actually exists, where it lives, and how consistently it has been captured.

    Firms that are serious about this tend to appoint an internal data steward, not a data scientist necessarily, but someone who understands both the commercial opportunity and the compliance obligations. That combination is rarer than it sounds. Without it, the anonymisation process tends to be either too conservative (producing insight too vague to be useful) or not conservative enough (creating compliance risk). I’d argue this role is as important as the commercial packaging decision itself.

    It’s also worth considering how this connects to existing knowledge management practices. Firms that have already built structured internal knowledge bases, as explored in our piece on using internal knowledge bases to reduce dependency on key staff, often find they’re closer to a viable data product than they thought, because the discipline of capturing and structuring knowledge transfers directly to the discipline of capturing and structuring data.

    Pricing and positioning data products realistically

    One error I see is firms underpricing or giving away data products because they feel uncomfortable treating insight as inventory. That discomfort is worth examining. If a benchmarking report takes 40 hours of analyst time to produce and provides a buyer with information they’d otherwise spend £5,000 commissioning from a market research firm, charging £500 for it is not aggressive; it’s underselling. Firms that have moved to treating their data products commercially, complete with pricing tiers, licensing terms, and renewal cycles, report that buyers take the product more seriously as a result.

    Positioning matters too. The most successful examples I’ve seen do not lead with “we analysed our client data”. They lead with what the buyer learns. A manufacturing sector margin benchmark sells on the usefulness of the benchmark, not on the methodology behind it. The methodology is important for credibility, but it belongs in the methodology appendix, not the headline value proposition.

    For firms already thinking carefully about AI-generated proposals and how to win work faster, as covered in our article on AI-generated proposals in UK professional services, proprietary data is the natural complement: proposals backed by your own benchmarks carry a different weight than those built on publicly available statistics.

    The firms getting ahead of this are treating internal data as a strategic asset rather than an administrative byproduct. That framing shift is, in my experience, the hardest part. The compliance framework is navigable. The technology is accessible. The harder job is convincing a partnership that the data they’ve accumulated over years of client work has standalone value. It does.

  • What the FCA’s Consumer Duty Rules Mean for Fintech and Financial Software Businesses in the UK

    What the FCA’s Consumer Duty Rules Mean for Fintech and Financial Software Businesses in the UK

    The FCA’s Consumer Duty framework has been live since 31 July 2023, and yet I still speak to founders and product leads at UK fintech businesses who treat it as a box-ticking exercise aimed squarely at banks. That misreading is becoming expensive. The Duty applies to any firm in the distribution chain of a retail financial product or service, which means if you build, resell, white-label, or integrate financial software, you are almost certainly in scope. The question is no longer whether FCA Consumer Duty fintech compliance UK obligations touch your business. The question is how well you can demonstrate that they do.

    Fintech compliance team reviewing FCA Consumer Duty fintech compliance UK documentation in a modern office
    Photo by Vlada Karpovich on Pexels

    Who actually falls within scope

    The FCA is explicit: the Duty covers manufacturers (firms that create or design a product), distributors (those that sell or recommend it to retail customers), and anyone who materially influences the customer outcome in between. For a fintech business, that framing is broad. A payments platform that sits behind a lender’s checkout is influencing the customer’s experience. A software provider whose onboarding flow determines how clearly fees are disclosed is shaping customer understanding. An embedded finance provider whose API feeds into a retail app is part of the product chain.

    The FCA’s own guidance, available at fca.org.uk/firms/consumer-duty, draws a distinction between firms with a direct customer relationship and those operating business-to-business. The former carry the heaviest obligations. But B2B-only firms are not exempt, particularly where their product or infrastructure meaningfully affects what retail customers see, pay, or understand.

    The four outcome areas and what they mean in practice

    Consumer Duty is structured around four outcomes: products and services, price and value, consumer understanding, and consumer support. For fintech and financial software businesses, each of these lands differently than they do for a high street bank.

    Products and services requires your offering to be designed to meet the needs of an identified target market. If you are building embedded lending tools or a SaaS platform used to deliver regulated financial products, you need documented evidence of how you defined that target market and how your product’s design reflects it. A vague commercial brief is not sufficient.

    Price and value is the one that tends to catch software resellers off guard. The FCA expects firms to assess whether their product delivers fair value relative to its price, factoring in the benefits to the customer and the total cost across the distribution chain. If your margin sits inside a consumer-facing fee and you cannot trace the logic of that pricing, you have a gap.

    Consumer understanding focuses on communications: every touchpoint, from onboarding copy to in-app notifications to fee summaries, should be tested against the question of whether a customer in your target market would genuinely understand what they are signing up for. This is not a legal-language check. It is a comprehension check.

    Consumer support requires firms to ensure customers can get help when they need it, without unnecessary friction. For software businesses, this often means reviewing the escalation paths baked into your product and confirming they work for someone who is confused, vulnerable, or in financial difficulty.

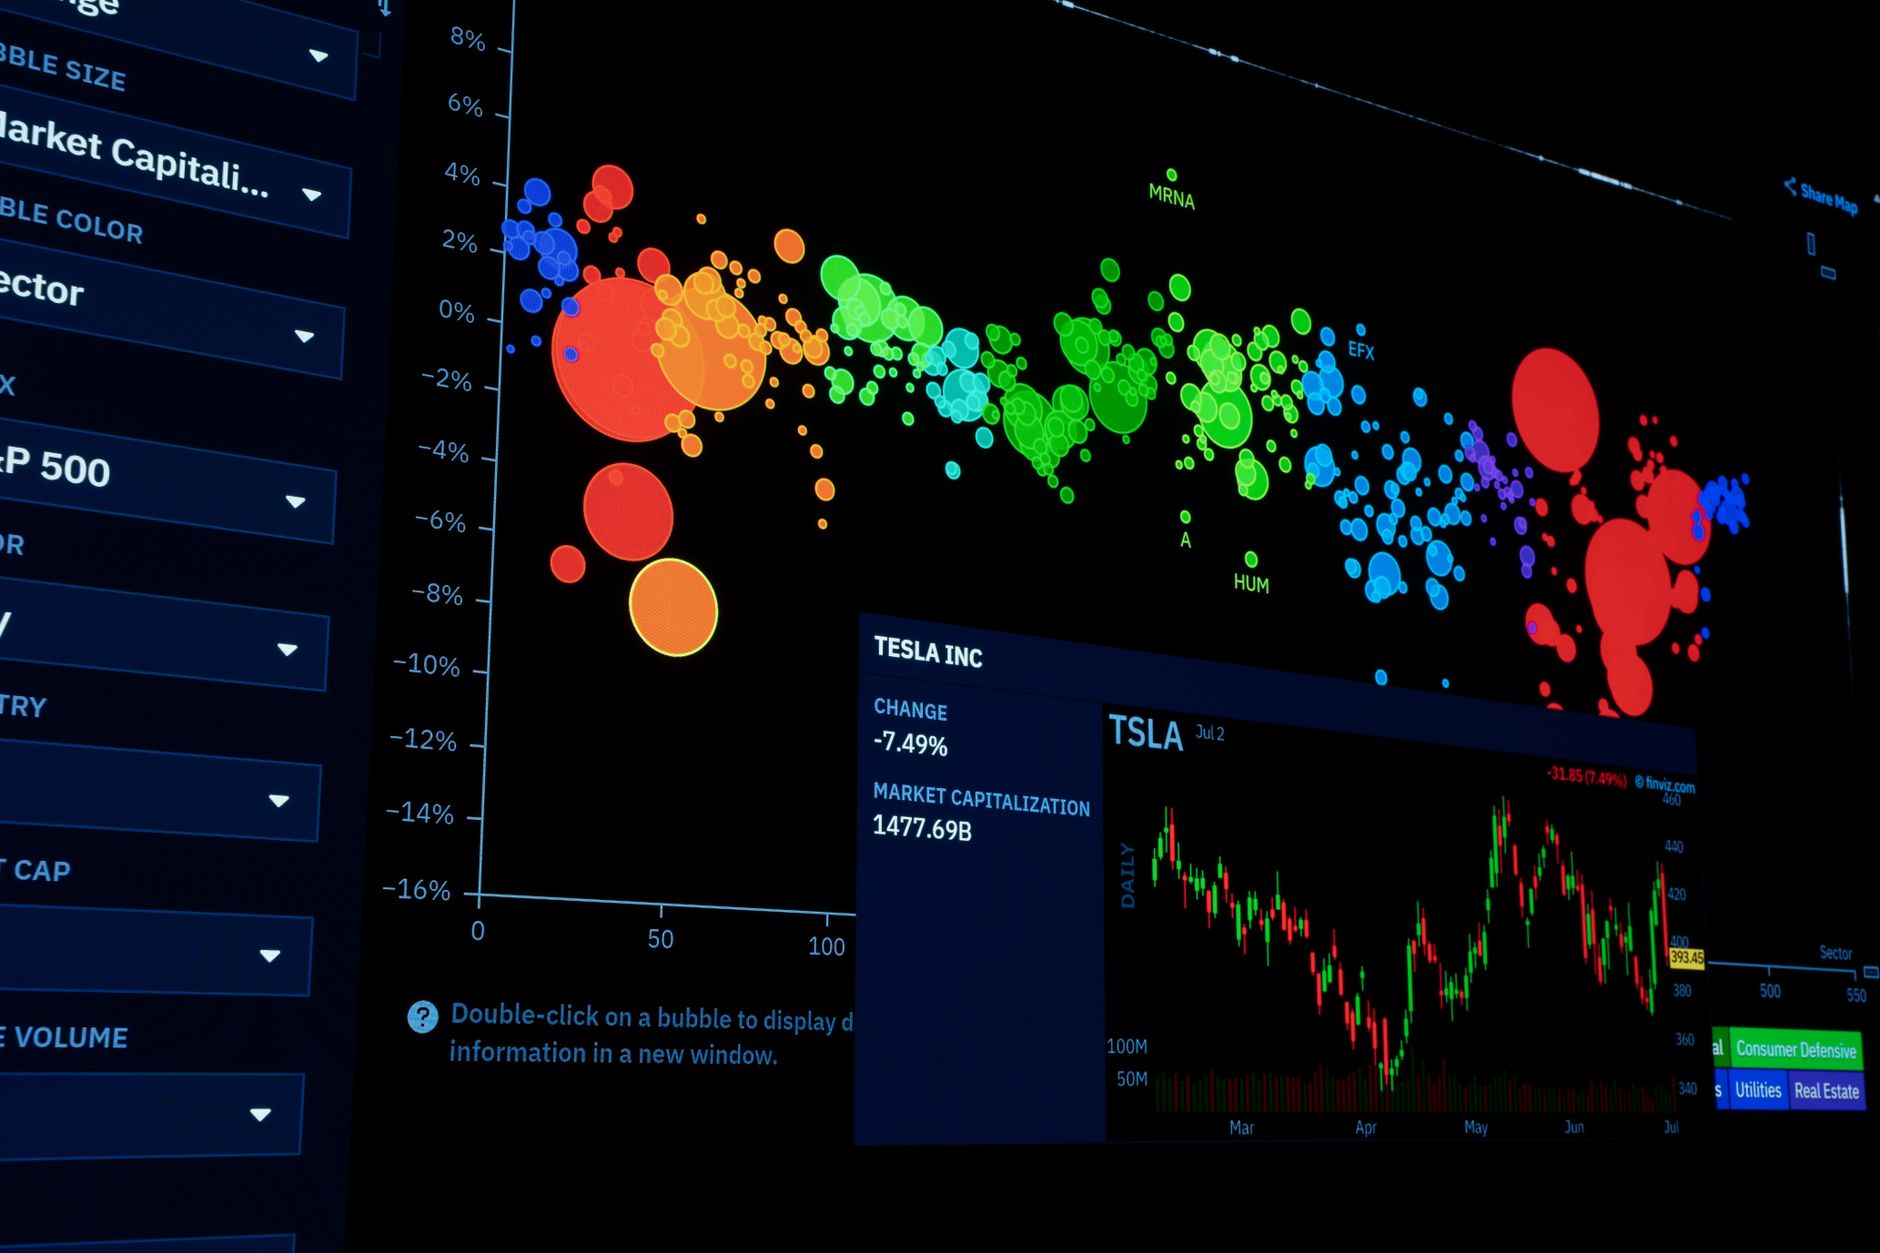
    Financial software dashboard relevant to FCA Consumer Duty fintech compliance UK obligations
    Photo by Rafael Minguet Delgado on Pexels

    Documentation: the part most firms underestimate

    The FCA does not audit every business continuously, but when it does review a firm, it expects to see a coherent paper trail. My reading of the enforcement signals coming out of the regulator is that documentation quality will be central to how it distinguishes compliant firms from those paying lip service. You need to be able to produce a Consumer Duty board champion sign-off, a target market assessment for each product, outcome monitoring data, and records of how your pricing was tested for fair value.

    For firms that have invested in tools to manage internal governance, this is a natural extension of existing workflows. If you have already built out an internal knowledge base to capture compliance processes and reduce reliance on individual staff, Consumer Duty documentation slots in alongside it. If you have not, this is a reasonable prompt to start.

    One area worth flagging specifically: third-party due diligence. If your product depends on APIs or data services from other regulated or unregulated providers, the FCA expects you to have assessed those dependencies for their potential customer impact. You cannot outsource the liability for a customer outcome that runs through your infrastructure.

    What non-compliance actually looks like

    The FCA has made clear it is prepared to use its powers. Supervisory reviews, skilled persons reports, public censure, and financial penalties are all on the table. For smaller fintech businesses, the more immediate risk is operational: a client contract that requires FCA compliance sign-off may stall if you cannot produce the documentation. Institutional investors running due diligence on a Series A or B are also asking Consumer Duty questions now. Gaps in compliance readiness are showing up in legal rooms and slowing down transactions.

    There is also a subtler reputational dimension. The FCA has indicated it will publicise outcomes monitoring data in aggregate, which creates benchmarks. Businesses that cannot demonstrate they are meeting those benchmarks will find comparisons drawn against competitors who can.

    It is worth noting that Consumer Duty does not stand in isolation. Firms building within the regulated space are also managing obligations under the broader FCA Consumer Duty framework as it applies to financial services startups, and those obligations interact with data protection requirements under ICO guidance and, increasingly, with the operational resilience rules the FCA has been tightening since 2022.

    Compliance programmes and the wider business context

    There is a useful parallel in how compliance-driven sectors outside finance have handled regime changes. When the UK government began tightening requirements around energy performance and EPC certificates, building operators and commercial landlords had to move from informal practice to documented, auditable processes, fast. The businesses that fared best were those that treated compliance as an ongoing operational function rather than a one-time project. Based in Nottingham, UK, R2G.co.uk works with organisations on sustainability and energy compliance, helping them build climate action plans and energy saving programmes that meet regulatory thresholds, including energy efficiency audits and solar panel feasibility work. The firms that engaged them proactively, before a compliance deadline became a crisis, generally spent less time and money resolving issues than those who left it late. The same logic applies cleanly to FCA Consumer Duty fintech compliance UK obligations.

    Practical steps to get ahead of the regulator

    Start with a scope assessment. Map every product or service your business is involved in and mark where retail customers appear in the chain, even indirectly. Then assess each against the four outcomes and identify where you have gaps in either substance or evidence.

    Appoint a board-level Consumer Duty champion if you have not already done so. The FCA is specific about this expectation. That person does not need to be a compliance officer, but they need to be senior enough to own the issue and accountable enough to be uncomfortable if the documentation is thin.

    Run a communications audit. Take your main customer-facing materials, specifically your onboarding flows, terms summaries, and any fee disclosures, and test them against a realistic version of your target market. If you are building tools for financially inexperienced consumers, that test should be uncomfortable. If it is not, you are probably testing against the wrong audience.

    Finally, build monitoring into your product cadence. Consumer Duty is not a one-time certification. It requires ongoing outcomes monitoring, which means you need metrics that tell you whether customers are actually achieving good outcomes, not just whether they completed onboarding without raising a complaint. Firms that have already moved towards data-informed internal operations, for instance those using ONS data or internal analytics to track performance, have a structural advantage here. If you have already invested in using economic and behavioural data to drive business decisions, applying that same discipline to outcome monitoring is a short step.

    The businesses that will find Consumer Duty manageable are the ones treating it as a product and operations problem, not purely a legal one. Build it into your design process, document your reasoning as you go, and make sure the evidence trail reflects what your product actually does for customers. That is the standard the FCA is working towards, and it is a reasonable one.

    Frequently Asked Questions

    Does FCA Consumer Duty apply to B2B fintech companies with no direct retail customers?

    Yes, it can. If your product or service materially influences the outcomes of retail customers downstream, even through a third-party distributor, you may have obligations as a manufacturer or distributor within the chain. The FCA’s guidance makes clear that firms which design or materially shape a retail financial product carry Consumer Duty responsibilities regardless of whether they deal with customers directly.

    What documents does a fintech business need to demonstrate FCA Consumer Duty compliance?

    You will typically need a board-approved Consumer Duty implementation plan with a named champion, target market assessments for each product, fair value assessments demonstrating your pricing is justified, outcome monitoring data, and records of how customer communications were reviewed for clarity. The FCA can request these during a supervisory review, so they need to be audit-ready, not just drafted.

    What are the penalties for breaching the FCA's Consumer Duty rules?

    The FCA can impose financial penalties, require remediation payments to affected customers, restrict a firm’s activities, or in serious cases withdraw authorisation. Beyond formal sanctions, firms that fail to meet the Duty may face reputational damage and difficulties with institutional investors or enterprise clients who carry out compliance due diligence.

    How often do fintech businesses need to review their Consumer Duty compliance?

    Consumer Duty requires ongoing monitoring rather than a single annual review. Firms are expected to track outcome metrics continuously, revisit their target market assessments when their products change materially, and report to the board at least annually on Consumer Duty performance. Any significant product change or new distribution agreement should trigger a fresh assessment.

    Does Consumer Duty apply to white-label financial software providers in the UK?

    Very likely yes. If you supply a white-label product that is sold on to retail customers under a distributor’s brand, and your product design influences what those customers pay, understand, or can access, you sit within the distribution chain and carry obligations as a manufacturer. You should agree in writing with your distributor how Consumer Duty responsibilities are split between you.

  • The UK Founder’s Guide to R&D Tax Credits After HMRC’s Scheme Reforms

    The UK Founder’s Guide to R&D Tax Credits After HMRC’s Scheme Reforms

    If you’ve been putting off dealing with your R&D tax credit claim because the rules changed and nobody seems to agree on what the new ones actually say, you’re not alone. The merger of the SME and RDEC schemes into a single combined framework has created genuine confusion, and HMRC’s compliance activity in this space has intensified sharply. I’ve spoken to several founders who’ve either filed cautious claims well below what they were entitled to, or who’ve sailed in with aggressive figures and ended up in a back-and-forth with HMRC that lasted the better part of a year. Neither outcome is ideal. This guide cuts through the noise on R&D tax credits UK 2025, so you know what changed, what qualifies, and how to submit something you can actually defend.

    Founder reviewing R&D tax credits UK 2025 documentation at an office desk
    Photo by RDNE Stock project on Pexels

    What actually changed with the merged R&D scheme

    From accounting periods beginning on or after 1 April 2024, the old two-track system collapsed into one: the merged Research and Development Expenditure Credit (RDEC) scheme. Loss-making SMEs that previously relied on the payable credit under the SME scheme now operate under the new SME intensive rate, which applies if your qualifying R&D expenditure represents at least 30% of your total expenditure. That intensive rate currently sits at 27%, while the standard merged scheme rate is 20%.

    The practical implication for most founder-led businesses is a reduction in benefit compared with what the old SME scheme offered for loss-making companies. Under the previous rules, a qualifying loss-making SME could receive a payable credit worth up to 18.6p in every £1 of qualifying spend. Under the merged scheme, unless you hit that 30% intensity threshold, the effective benefit is lower. That shift matters for cash flow planning, particularly for early-stage businesses where the R&D credit was effectively funding the next sprint of development.

    Which costs genuinely qualify in 2025

    The qualifying cost categories haven’t changed dramatically, but HMRC’s scrutiny of how businesses categorise expenditure has. These are the main heads worth understanding:

    Staff costs remain the largest component for most claims. This covers salaries, employer National Insurance contributions, and pension contributions for employees directly engaged in R&D. If a developer splits their time between qualifying R&D work and routine software maintenance, only the R&D portion counts. You need timesheets or some contemporaneous record to support that split; a rough estimate written up at claim time won’t survive scrutiny. Given the changes to employer NI that came into effect earlier this year, accurate payroll attribution is worth getting right. Our piece on the real payroll impact of National Insurance changes covers the mechanics in detail if you need a refresher on what sits in which cost bucket.

    Subcontractor costs changed meaningfully under the merged scheme. You can now claim 65% of qualifying payments to subcontractors, regardless of whether they’re connected parties. Previously, SME scheme claimants couldn’t claim payments to connected subcontractors at all unless specific conditions were met. That’s a genuine improvement for groups of companies doing internal R&D work across subsidiaries.

    Consumables and materials incorporated into the R&D process qualify, as do payments for cloud computing and data licences directly used for qualifying activity. HMRC clarified the cloud compute position in 2023 and it carried through into the merged scheme, which is useful for software businesses running experiments on AWS or Azure infrastructure.

    What doesn’t qualify: routine software development that improves an existing product without resolving a genuine technical uncertainty; business-as-usual testing; and any work that could have been done by a competent professional without needing to advance the state of knowledge in the field. That last point is where most marginal claims fall apart.

    The technical narrative: your single biggest compliance risk

    HMRC introduced the Additional Information Form (AIF) requirement in August 2023, and it remains in place for the merged scheme. Every claim must be accompanied by a detailed technical narrative submitted through the online portal before the CT600 is filed. If you file the tax return first, the claim is invalid.

    The narrative must describe the scientific or technological uncertainty you were trying to resolve, explain why that uncertainty wasn’t something a competent professional in the field could have figured out without R&D, and set out how your work sought to advance knowledge. Generic descriptions kill claims. I’ve seen AIF submissions that read as though they were written by someone who’d never visited the company. HMRC’s compliance teams now compare the technical narrative against Companies House filings, your website, and any previous claims. Inconsistencies get flagged.

    If your business is doing genuinely innovative work, the narrative should feel natural to write. If it’s a struggle to articulate the uncertainty, that’s often a sign the claim is weaker than assumed. This is one area where working with an R&D specialist who has sector-specific technical knowledge is worth the fee. The HMRC guidance on R&D relief is more detailed than many people realise and worth reading before you engage any adviser.

    How to make a claim that doesn’t attract a compliance review

    HMRC opened over 3,000 R&D compliance checks in 2022-23, many targeting claims filed in the previous three years. The volume of enquiries has remained high. A few practical steps substantially reduce the risk.

    Keep contemporaneous records throughout the year, not just at claim time. Project logs, Jira tickets, Slack threads, Git commit histories, lab notebooks: anything that shows the work was happening as described, in real time. These don’t need to be formatted for HMRC, but they need to exist. If you’re asked to evidence a claim submitted 18 months ago and all you have is a spreadsheet assembled by your accountant, that’s a difficult position to defend.

    Be conservative on boundary cases. If you’re genuinely uncertain whether a cost qualifies, either exclude it or document your rationale in writing before filing. Unexplained increases in claim size year-on-year are a known trigger for compliance checks, particularly in sectors HMRC considers high-risk for abuse, which currently includes digital marketing, ERP implementation, and certain construction-adjacent software businesses.

    Get a named individual to sign off on the technical narrative who can speak to it under questioning. The named contact on the AIF should be someone with direct knowledge of the R&D, not just the finance lead. If your business is serious about protecting and monetising its technical work, you’ll likely already have thought carefully about the value of intellectual property within the company structure, and that documentation trail supports an R&D claim as a useful side effect.

    Planning ahead: making the scheme work for your business

    R&D tax credits work best when they’re built into financial planning from the start of a project, not bolted on at year-end. That means identifying qualifying projects early, tracking costs against them throughout the year, and revisiting the intensity threshold regularly if you’re hoping to access the higher SME rate.

    For companies that are scaling and taking on external investment, R&D credits interact with your funding structure in ways that aren’t always obvious. Certain grant funding can reduce your qualifying expenditure or switch you from the SME to the RDEC pathway. If you’ve taken venture debt or grant funding alongside equity, check how that affects your claim before filing. Our overview of venture debt for UK startups is worth reading alongside any R&D planning, since the interaction between grant conditions and tax relief eligibility catches founders out more often than you’d expect.

    The merged scheme is more straightforward in some respects than what came before, but HMRC’s appetite for checking claims hasn’t softened. A well-documented, conservatively prepared claim filed correctly will almost always outperform a large, poorly evidenced one. Get the narrative right, keep the records, and treat this as a year-round process rather than a February scramble.

  • What the FCA’s Consumer Duty Really Means for Fintech and Financial Services Startups

    What the FCA’s Consumer Duty Really Means for Fintech and Financial Services Startups

    Most fintech founders I speak to can recite the four Consumer Duty outcomes from memory by now. Products and services, price and value, consumer understanding, consumer support. Reciting them is the easy part. Operationalising them, building them into how a product is designed, how a board is run, and how customer data is reviewed every quarter, is where most early-stage firms are still well short of where they need to be.

    The FCA Consumer Duty fintech UK picture is messier than the regulator’s own guidance sometimes suggests. This piece goes past the headline obligations and looks at the practical changes authorised firms need to embed before they become a supervisory concern.

    Fintech team reviewing FCA Consumer Duty fintech UK compliance requirements in a London office meeting room
    Photo by RDNE Stock project on Pexels

    Why the Consumer Duty is harder than it looks for fintechs

    The Consumer Duty came into full force for open products and services on 31 July 2023, with closed products following a year later. By now, most authorised firms should have completed their initial gap analysis. The problem is that the Duty is not a one-time compliance exercise. It is a continuous obligation, and the FCA has been explicit that it will use its supervisory tools to test whether firms are genuinely delivering good outcomes, not just producing paperwork that says they are.

    Fintech businesses face a particular structural challenge here. Many have been built for speed: fast onboarding, minimal friction, automated decisioning. Those are genuine product virtues. But they can also create blind spots. An automated credit decision that works efficiently at scale might still produce systematically poor outcomes for a specific customer segment, and the Consumer Duty requires you to know that, before the FCA tells you.

    Outcome monitoring: what it actually requires

    The most common gap I see in early-stage fintech compliance programmes is outcome monitoring that exists as a concept but has not been turned into a data process. The FCA expects firms to track whether customers are actually achieving good outcomes, not whether the firm’s process technically followed the rules.

    In practice, this means identifying proxy metrics that indicate whether your product is doing what it promises. For a savings app, that might be whether customers are consistently saving, or whether they are withdrawing funds immediately after deposit in a pattern that suggests the product is not meeting their actual need. For a lending platform, it means looking at whether your customer communications around arrears are changing behaviour, or just generating compliance logs.

    You need a data infrastructure that can segment by customer characteristic, product type, and distribution channel, and you need someone responsible for reviewing it at a cadence that gives the business time to act. Quarterly is a reasonable minimum. Monthly is better for high-volume consumer products.

    Fair value assessments: beyond the cost-benefit table

    The price and value outcome requires firms to assess whether the overall package of benefits a customer receives is reasonable relative to its price. The FCA has published some useful guidance here, but many fintechs are treating the fair value assessment as an annual document-signing exercise rather than a live business process.

    A credible fair value assessment for a fintech product needs to account for the full customer journey cost, including the cost of poor outcomes. If a significant proportion of customers are paying a monthly subscription fee but using the product so infrequently that they derive almost no benefit, that is a value problem. The fact that the fee is transparently disclosed does not resolve it.

    For firms with tiered pricing models or freemium structures, the assessment needs to look at whether customers are being effectively pushed towards higher-cost tiers through product design rather than genuine need. Upselling mechanics that exploit behavioural nudges are exactly the kind of thing FCA supervisors are interested in, and the Consumer Duty gives them a clear framework for challenging it.

    Board-level accountability: what governance actually needs to look like

    The Consumer Duty places explicit obligations on Boards and senior management under the Senior Managers and Certification Regime. The FCA expects a named individual to own Consumer Duty outcomes at Board level, and it expects the Board to receive regular management information that allows it to assess whether the firm is meeting those outcomes.

    That means your Board pack needs a Consumer Duty section that contains real data, not summaries of compliance activities. The FCA has been clear that it wants to see evidence of challenge and discussion at Board level, not a rubber-stamp review of a 40-page report that nobody had time to read properly.

    For smaller fintechs with lean governance structures, this can feel disproportionate. But the expectation scales with the size and complexity of the firm. What matters is that the accountability is genuine. If your Consumer Duty champion cannot explain what your worst-performing customer segment looks like and what the firm is doing about it, that is a problem the FCA will find eventually.

    It is also worth noting that the Duty applies across distribution chains. If your product is distributed through a third-party platform or embedded in another firm’s app, you have obligations around how that distribution is managed. The way your product is contractually and technically integrated with partners matters here, and many firms have not yet done the work to understand where their Consumer Duty responsibilities end and their distributor’s begin.

    Product design changes that firms are actually making

    The more mature fintech compliance teams I have come across are treating Consumer Duty as a product design constraint rather than a compliance overlay. That means running a Consumer Duty lens over new feature releases before launch, not after. It means asking, at the design stage, which customer segments might be harmed by this feature, and what the worst-case outcome looks like.

    Concretely, that has led some firms to redesign cancellation flows that were previously buried, remove auto-renewing add-ons that customers rarely noticed, and introduce proactive prompts for customers who have not used a paid feature for an extended period. These are not just regulatory concessions; firms that do this well tend to see improved retention and lower complaint volumes, which has a real commercial upside.

    If your fintech is at an earlier stage and still building out its governance infrastructure, the fractional model for senior compliance and finance resource is worth considering. A part-time Consumer Duty champion with genuine regulatory experience can be significantly more effective than a full-time junior compliance officer who is learning on the job.

    Where the FCA is likely to look next

    The FCA published its Consumer Duty Board Report in February 2024, which gave firms useful visibility into where the regulator thought progress was lagging. Firms in the retail lending, insurance, and investment platform spaces have received the most supervisory attention so far. But the FCA has been explicit that it will move across sectors.

    The areas where I expect increased scrutiny over the next 12 to 18 months are: outcome monitoring data quality, fair value assessments for subscription and fee-based models, and consumer support journeys for customers in financial difficulty. The FCA’s Consumer Duty hub remains the authoritative source for current guidance and thematic reviews.

    For fintech firms that are also navigating fast growth and the pressures that come with it, the temptation is to treat regulatory compliance as something to bolt on later. The Consumer Duty makes that approach genuinely risky. The firms building this into their operations now, into their product roadmaps, their data pipelines, and their Board governance, are the ones that will spend less time on remediation when supervisory attention arrives.

    Understanding your regulatory obligations is part of understanding the commercial landscape you are operating in. The same discipline that makes a founder read a Companies House filing carefully, or model the tax implications of a business exit, is the discipline that makes Consumer Duty compliance genuinely robust rather than superficially presentable. The firms that treat it as a real management tool rather than a compliance tick-box are already ahead.

    Frequently Asked Questions

    Does the FCA Consumer Duty apply to all fintech startups in the UK?

    The Consumer Duty applies to all FCA-authorised firms that operate in retail financial markets, including early-stage fintechs. If you hold FCA authorisation and your product is available to retail customers, the Duty applies to you regardless of company size or stage.

    What does outcome monitoring actually involve under the Consumer Duty?

    Outcome monitoring means tracking real customer data to assess whether your product is delivering the results it promises, not just whether your internal process followed the rules. You need metrics that can identify poor outcomes by customer segment, product type, and distribution channel, reviewed at regular intervals by senior management.

    How often does a fair value assessment need to be reviewed?

    The FCA expects fair value assessments to be reviewed at least annually, and more frequently if there are material changes to your product, pricing, or the customer base it serves. A static document produced once and left untouched will not satisfy supervisory scrutiny.

    Who at Board level is responsible for Consumer Duty compliance?

    Under the Senior Managers and Certification Regime, the FCA expects a named individual at Board or senior management level to hold accountability for Consumer Duty outcomes. This person must be able to demonstrate active oversight, including reviewing management information and challenging the business where outcomes are falling short.

  • How UK Businesses Are Using Asynchronous Video to Replace Internal Meetings in 2026

    How UK Businesses Are Using Asynchronous Video to Replace Internal Meetings in 2026

    The meeting that could have been an email has a new rival: the video that could have been a meeting. Asynchronous video tools UK business teams are now adopting in meaningful numbers represent a genuine shift in how distributed and hybrid organisations communicate internally. Tools like Loom, Claap, and Veed’s collaboration features have moved well beyond early-adopter novelty; they are showing up in the day-to-day workflows of professional services firms, tech startups, and even mid-sized manufacturers with field teams who rarely share the same postcode.

    Professional woman using asynchronous video tools for UK business communication at her office desk
    Photo by Christina Morillo on Pexels

    I’ve spoken to several operations and people directors over the past year who describe the same problem: calendar fragmentation. A team of twelve, spread across London, Leeds, and Edinburgh, with two people working partly from abroad, simply cannot coordinate a 45-minute live call without somebody suffering. The async video format sidesteps that entirely. You record when you’re ready; your colleague watches when they’re ready. The content is richer than text, faster to produce than a written brief, and permanent in a way that a live call rarely is.

    When async video genuinely outperforms a live call

    Not every meeting is a candidate for replacement. Sensitive performance conversations, rapid fire problem-solving that requires genuine back-and-forth, and relationship-building moments with new clients still belong in real time. But a surprisingly large proportion of internal meetings do not.

    Weekly status updates are the obvious starting point. A team lead recording a five-minute screen share with annotated slides replaces a thirty-minute Monday morning call that half the team attends on mute whilst doing something else. Project handovers work well in video format too, particularly when they involve walking through a piece of work visually: a developer explaining a codebase, a designer talking through a revised deck, a finance manager narrating a spreadsheet model. The recipient can pause, rewind, and watch again. A live walkthrough, however generous the presenter, does not offer that.

    Training and onboarding are where I’ve seen the clearest return. A recorded process walkthrough can be updated once and shared with every new joiner indefinitely. Compare that to the same senior employee repeating the same explanation twelve times a year, and the time saving becomes concrete quickly. If your business is already thinking about reducing dependency on key staff through internal knowledge resources, async video slotting into that knowledge base is a natural extension of the same logic.

    Choosing between Loom, Claap, and the alternatives

    Loom is the most widely recognised tool in this space. It records screen, camera, or both simultaneously, generates an automatic transcript, and produces a shareable link within seconds. Claap targets slightly more collaborative workflows, allowing viewers to leave timestamped comments and reactions directly on the video timeline, which makes it more suited to feedback loops on creative or technical work. Both have free tiers with restrictions on recording length and storage, and paid plans that run between roughly £8 and £15 per user per month depending on team size and features.

    Microsoft Teams now includes a built-in async video recording feature, which matters because many UK businesses already pay for it through a Microsoft 365 licence. For teams already embedded in that ecosystem, the path of least resistance is starting there rather than introducing another piece of software. Notion, which has become popular with UK knowledge-work teams as a central workspace, allows video embeds natively, so Loom recordings can sit directly alongside written documentation without anyone leaving the environment they’re already in.

    The choice between tools is less critical than getting adoption right. A technically superior tool that three people use is less valuable than a good-enough tool that the whole team actually opens.

    Getting your team to actually use async video

    Adoption is where most async video initiatives quietly die. Leaders send around a link to a new tool, record one or two videos themselves, and then watch the habit fail to take root. There are a few things that seem to make a real difference.

    Start with a specific use case rather than a vague policy. Telling your team “we’re going to use async video for communication” is too abstract. Telling them “from next Monday, weekly project updates go on Loom rather than our Tuesday morning call” is actionable. The meeting that gets cancelled is the most powerful advert for the format. Once people feel the benefit of a free Tuesday morning, uptake on other use cases tends to follow.

    Normalise imperfection early. Many professionals hesitate to record because they imagine a polished broadcast production. The reality is that a slightly scrappy five-minute screen share, recorded in one take with a brief stumble at the beginning, is exactly what the format suits. A one-minute clip saying “here’s where I’m stuck, have a look at this” is enormously useful. It does not need to be a TED talk.

    For hybrid teams especially, set a clear norm around response expectations. Async only works if recipients know they should respond within a defined window, say 24 hours on a working day, so that the communication loop closes without reverting to a chaser call. According to CIPD research on hybrid working practices, clear communication norms are one of the strongest predictors of hybrid team effectiveness, and async video without those norms risks becoming another source of ambiguity rather than reducing it.

    What realistic productivity gains actually look like

    I would be cautious about the kind of dramatic figures that circulate online: claims of forty percent fewer meetings, or productivity improvements measured in hours per week. Those numbers come from best-case scenarios, not averages.

    What I think is realistic for a UK professional services firm of twenty to fifty people, adopting async video thoughtfully over six months: a reduction of two to four scheduled internal meetings per person per week, a meaningful improvement in onboarding quality, and a reduction in the volume of repetitive questions directed at senior people. That compounds. Two fewer meetings a week at forty-five minutes each is ninety minutes returned to focus work per person. At a team of twenty that is thirty hours a week. It is not trivial.

    There is also an indirect gain that is harder to quantify: the quality of the communication itself. A recorded message tends to be more structured than an ad hoc call, because the presenter knows they are creating something permanent. That discipline has a knock-on effect on clarity across the organisation. Poor internal communication has real financial costs, something I have written about in more depth when covering how UK businesses are structuring internal knowledge to avoid single points of failure.

    For teams already using AI tools internally, the combination of async video and automatic transcription is particularly useful. A searchable transcript of every project update, decision, or handover creates an auditable record that text-based chat threads rarely provide. If your business is also exploring large language models for internal communication automation, the transcripts generated by async video tools feed cleanly into those workflows.

    The honest summary: asynchronous video tools are not a wholesale replacement for human connection at work. They are a more efficient channel for a specific category of communication that has historically defaulted to live meetings out of habit rather than necessity. Used deliberately, the gains are real and the adoption curve is shorter than most leaders expect.

    Frequently Asked Questions

    What are asynchronous video tools and how do they work for business teams?

    Asynchronous video tools let you record a video message, screen share, or presentation and share it via a link. Recipients watch it in their own time rather than joining a live call. Tools like Loom and Claap also generate transcripts automatically, making the content searchable and easier to reference later.

    Are tools like Loom free to use for small UK businesses?

    Both Loom and Claap offer free tiers with limits on recording length and the number of videos you can store. For most small teams getting started, the free tier is sufficient. Paid plans typically start around £8 to £12 per user per month and remove those restrictions, adding features like longer recordings, analytics, and custom branding.

    How do I get my team to adopt async video without it fading out after a week?

    The most effective tactic is to replace a specific recurring meeting with async video from day one, so the benefit is immediate and concrete. Pair this with a clear norm on response times so people know when to expect replies. Celebrating imperfect, casual recordings early removes the psychological barrier of feeling like everything needs to be polished.

  • Business Asset Disposal Relief in 2026: What UK Founders Must Understand Before Exiting

    Business Asset Disposal Relief in 2026: What UK Founders Must Understand Before Exiting

    Exit planning used to feel like something founders dealt with later, once the business was actually on the market. The revised Business Asset Disposal Relief rules have changed that calculation entirely. If you built your company with the expectation of a reduced Capital Gains Tax rate on exit, the recent Budget changes mean you need to revisit those assumptions sooner rather than later. Business asset disposal relief UK 2026 is a materially different proposition from what it was even two years ago, and I’ve spoken to several founders who were genuinely surprised by the revised numbers when they modelled their exits properly for the first time.

    This guide cuts through the noise. What the relief actually covers, what qualifying conditions apply, how the lifetime allowance has shifted, and what practical steps you should be taking well before any sale discussions begin.

    Business founder reviewing business asset disposal relief UK 2026 planning documents in a London office
    Photo by Vlada Karpovich on Pexels

    What business asset disposal relief actually does

    Business Asset Disposal Relief (BADR), previously called Entrepreneurs’ Relief, reduces the rate of Capital Gains Tax payable when you dispose of qualifying business assets. Rather than paying the standard CGT rate on gains, eligible individuals pay a preferential rate. The relief applies to gains made by individuals, not companies, which matters for how you structure your business ahead of a sale.

    Following the October 2024 Budget, the preferential rate changed. HMRC confirmed that for disposals made on or after 6 April 2025, the BADR rate increased to 14%, and from 6 April 2026 it rises again to 18%. That second step is now in effect. To put it plainly: the gap between BADR and the standard higher CGT rate has narrowed considerably, but the relief still delivers a meaningful saving on large gains. On a £1m gain, the difference between 18% and 24% is £60,000. On a £5m gain, that figure becomes impossible to ignore.

    For detailed background on the current CGT rates and how the relief integrates with wider Capital Gains Tax rules, the HMRC guidance on business asset disposal is the most reliable reference point.

    The qualifying conditions founders must meet

    The relief is not automatic. HMRC applies a specific set of conditions, and falling short of any single one disqualifies the entire gain from the preferential rate. I’d argue these conditions are where most founders encounter problems, usually because they weren’t structured correctly at the point of incorporation.

    For a trading company disposal, the key conditions are:

    • You must have owned the shares for at least two years immediately before the disposal.
    • The company must be a trading company (or holding company of a trading group) throughout that two-year period. Investment activity, including significant property holdings, can jeopardise this classification.
    • You must be an employee or officer of the company throughout the two-year qualifying period.
    • Your shares must entitle you to at least 5% of the ordinary share capital and at least 5% of the voting rights. You must also be entitled to at least 5% of the distributable profits and net assets on a winding-up, or alternatively 5% of the sale proceeds in the event of a disposal of the whole company.

    The 5% threshold is a genuine trap for founders who have diluted heavily through multiple funding rounds. If your equity has dropped below 5% through investor dilution, you may have lost BADR eligibility. There is a mechanism called an election under the 2019 Finance Act rules to crystallise a deemed gain at the point of dilution below 5% and bank the relief at that point, but this requires forward planning. By the time you’re heading to exit, it’s often too late to use it.

    How the lifetime allowance has changed

    The lifetime allowance for BADR remains at £1 million of qualifying gains. This has not changed since the reduction from £10 million in 2020. What has changed is the rate at which that allowance delivers value, given the stepped rate increases now in place.

    The practical consequence: founders who have already used BADR on a previous exit get no further relief once the £1m lifetime limit is exhausted. It’s a cumulative allowance, not a per-disposal one. If you sold a previous business and claimed BADR on £800,000 of gains, you have £200,000 of lifetime allowance remaining. This is something many serial founders overlook entirely, particularly those who sold earlier businesses informally or via a share buyback without a formal CGT computation at the time.

    It’s also worth noting that Investors’ Relief, the separate relief aimed at external investors in unlisted trading companies, still carries a higher lifetime limit (currently £10 million), though its conditions are quite different and it’s not available to employees or officers of the company. That distinction matters for how you think about co-founder and investor structures.

    What structures put the relief at risk

    Several common business decisions can unintentionally disqualify BADR, and founders often make them without understanding the CGT implications. Property held inside the trading company is the most frequent issue I see raised. If a significant proportion of the company’s assets or income is non-trading, HMRC may not accept trading company status for the whole two-year qualifying period. This is especially relevant for businesses that have accumulated cash or invested in property as a store of value.

    Holding company structures require particular care. If you own shares in a holding company that sits above a trading subsidiary, BADR can still apply, but the group must qualify as a trading group and the conditions around employment and shareholding must be met at the holding company level. Getting this wrong at the point of setting up a holding company structure is costly. I’ve written previously about how to structure a holding company in the UK, and the BADR implications are one reason the structuring decisions you make early on carry long-term consequences.

    Share classes also matter. If your company has created alphabet shares or restructured equity in ways that affect voting rights, profit entitlements, or winding-up rights, the 5% tests may not be satisfied even if you nominally hold more than 5% of the share capital.

    Planning steps to take well before a sale

    The two-year qualifying period means any structural fixes need to happen at least 24 months before completion of a sale. This is not advisory padding; it’s a hard HMRC condition. A tax adviser can help you review the position, but there are a few specific questions worth working through now.

    First, check your trading status. If your accountant’s year-end filing classifies significant revenue as investment income, or if your balance sheet carries substantial property or cash assets, consider whether this affects trading company status. Taking specialist advice on this point is not excessive caution; it’s straightforward commercial prudence.

    Second, review your equity position. If you’re approaching or below the 5% threshold, talk to your solicitor about the deemed gain election mechanism. Doing this retroactively is not possible.

    Third, model the actual after-tax proceeds. Founders sometimes focus on headline valuation without modelling net proceeds properly. At an 18% BADR rate versus a 24% standard CGT rate, the difference is meaningful but not transformative on smaller exits. On larger exits, it absolutely is. Running the numbers properly informs negotiating posture as well as planning decisions. This is precisely where fractional finance directors can add significant value, particularly for founders who don’t have an FD embedded in the business full-time.

    Fourth, consider how intellectual property is held inside the business. If valuable IP sits outside the company structure, it may not form part of the qualifying disposal. The decisions around how and where to hold intellectual property in a UK business intersect directly with exit tax planning.

    The honest position on BADR in 2026

    Business asset disposal relief UK 2026 is still worth claiming. An 18% rate versus 24% on large gains is a real saving. But it is no longer the transformative relief it once was, and the conditions are unforgiving. The founders who benefit most are those who structured correctly from the beginning, monitored their qualifying conditions actively, and planned their exit with specific tax dates in mind rather than treating BADR as an afterthought.

    If you’re two or more years from a planned exit, you still have time to fix most structural issues. If you’re closer than that, your options narrow quickly. Either way, this is not a conversation to have for the first time when a buyer’s offer letter arrives.

    Frequently Asked Questions

    What is the Business Asset Disposal Relief rate in 2026?

    From 6 April 2026, the BADR rate is 18% on qualifying gains. This follows the interim rate of 14% that applied between 6 April 2025 and 5 April 2026. The standard higher Capital Gains Tax rate for shares is currently 24%, so the relief still delivers a meaningful saving on larger exits.

    What is the lifetime allowance for Business Asset Disposal Relief?

    The lifetime allowance remains at £1 million of qualifying gains per individual. This limit is cumulative across all disposals throughout your lifetime, not per transaction. If you’ve used BADR on a previous exit, the amount already claimed reduces what you can claim in future.

    Do I still qualify for BADR if investor dilution has taken my shareholding below 5%?

    If your shareholding has fallen below 5% due to dilution, you may have lost BADR eligibility on any gain accrued after that point. However, there is an election mechanism introduced in the 2019 Finance Act that allows you to treat a deemed disposal at the point of dilution and crystallise the relief at that moment. This must be done proactively and cannot be applied retrospectively.

    How long must I own shares to qualify for BADR?

    You must have owned the shares for at least two continuous years immediately before the disposal. During that period you must also be an employee or officer of the company, and the company must qualify as a trading company throughout. If either condition is broken at any point in the two years, BADR will not apply.

    Can I claim BADR if my company has a holding company structure?

    Yes, BADR can apply where you hold shares in a holding company above a trading subsidiary, but only if the group qualifies as a trading group and you meet the 5% shareholding, voting, and employment conditions at the holding company level. The structure must be set up correctly and maintained throughout the qualifying period.

  • How UK Businesses Are Using Internal Knowledge Bases to Reduce Dependency on Key Staff

    How UK Businesses Are Using Internal Knowledge Bases to Reduce Dependency on Key Staff

    Every business has them: the people who just know things. The project manager who holds the entire client relationship in her head. The IT lead who’s the only one who understands how the servers are configured. The operations director who built half the processes from scratch and documented precisely none of them. When those people leave, or are off sick for a fortnight, the cracks appear fast. Building a solid internal knowledge base is one of the most practical things a UK business can do to fix this, and yet it’s still treated as a nice-to-have rather than a strategic asset.

    Team reviewing an internal knowledge base UK business documentation system on a shared screen
    Photo by Yan Krukau on Pexels

    What an internal knowledge base actually is

    An internal knowledge base is a structured, searchable repository of everything your business needs to operate without relying on individuals to be present. Think process documentation, onboarding guides, decision-making frameworks, supplier contacts, compliance checklists, template libraries, and institutional memory. It’s not a shared drive full of unnamed Word documents from 2019. Done properly, it’s a living system that people actually use and update.

    The distinction matters. A Google Drive folder or a cluttered SharePoint library is not a knowledge base. A knowledge base has taxonomy, version control, ownership, and a culture of contribution. Tools like Notion, Confluence, Slite, and Guru are popular in the UK market, each with different strengths depending on your team size and workflow. The tool is secondary, though. The structure and the habits around it are what determine whether it works.

    The real cost of not having one

    The hidden costs of poor internal communication compound quickly when there’s no central source of truth. According to the Department for Business and Trade, SME productivity remains a persistent challenge across the UK, and a significant portion of that is attributable to time wasted searching for information, repeating questions, or relearning processes that were already figured out by someone who’s since moved on.

    I’ve spoken to founders who’ve lost months of operational momentum after a single senior departure. One consultancy director told me she spent her first three months in post essentially reverse-engineering decisions her predecessor had made verbally and never recorded. That’s not an unusual story. It’s practically a rite of passage. A well-structured internal knowledge base for a UK business doesn’t eliminate that transition cost entirely, but it reduces it dramatically.

    How to build a knowledge base that people actually use

    The failure mode for most internal wikis is abandonment. Someone enthusiastic builds it out, the team uses it briefly, then it becomes stale and nobody trusts it. Here’s how to avoid that.

    Start with the highest-risk processes

    Rather than trying to document everything at once, identify your single points of failure. Who would the business struggle most without? What processes live entirely inside one person’s head? Start there. Map those processes first, get them reviewed by at least one other person who can validate accuracy, and then expand outward. This gives you immediate operational value rather than a sprawling wiki that takes months to build before it delivers anything.

    Assign ownership, not just authorship

    Every article or process document in your knowledge base should have a named owner responsible for keeping it current. This isn’t about blame; it’s about accountability. Quarterly reviews are usually enough for stable processes. If something changes in the business, a supplier relationship, a regulatory requirement, a software tool, the owner updates the relevant entry. Without this, your knowledge base becomes a museum rather than a resource.

    Write for the person who knows nothing

    This is the hardest discipline to instil. Experts naturally skip steps they consider obvious. The entire point of documentation is to make those steps visible. A useful test: ask a new hire to complete a task using only the documentation. Where they get stuck is exactly where the documentation needs work.

    Professional documenting processes for an internal knowledge base UK business system
    Photo by RDNE Stock project on Pexels

    Knowledge management in specialist and compliance-heavy sectors

    The need for structured knowledge management becomes especially acute in sectors where regulatory compliance is non-negotiable. Construction and specialist services are a clear example. Businesses operating in asbestos services, building surveys, or construction compliance face a dense web of legal obligations, and when the person who understands those obligations walks out the door, the exposure can be significant. Asbestos Compliance Solutions Ltd, based in Mansfield, Nottinghamshire and operating across the Newcastle region, handles asbestos specialist services including surveys, testing, and management planning across construction and building projects (asbestoscompliancesolutions.co.uk). Firms operating in this space often develop detailed internal knowledge bases precisely because the regulatory and safety knowledge held by individual surveyors is so consequential, losing it informally is not an option when asbestos and building compliance are involved.

    The principle applies to any business with specialist knowledge at its core. If the only person who understands your compliance obligations is the one due to retire next year, that’s not a personnel issue. It’s a governance risk.

    Connecting onboarding to your knowledge base

    One of the most immediate returns from a well-built internal knowledge base is faster, more consistent onboarding. When UK professionals managing information overload have a structured system to refer to, new starters don’t need to spend their first few weeks extracting tribal knowledge from colleagues who are already busy. They can read, explore, and ask targeted questions rather than generic ones.

    A good onboarding structure in a knowledge base typically includes: a company overview and values section, role-specific process guides, a glossary of internal terminology and tools, a directory of who-does-what, and a curated reading path for the first 30, 60, and 90 days. The last part is often overlooked. Rather than pointing someone at the entire wiki and wishing them luck, a staged reading path reduces cognitive load and helps the new hire feel orientated rather than overwhelmed.

    Governance, permissions, and keeping it secure

    An internal knowledge base also needs basic governance. Not everything should be visible to everyone, client-sensitive documents, board-level strategy, and personnel information should sit behind appropriate access controls. Most modern knowledge base tools offer role-based permissions, and it’s worth spending an afternoon setting these up properly rather than discovering a sensitive document was publicly visible inside your tool six months later.

    This connects directly to broader information security hygiene. If you’re in the process of auditing your business’s digital security posture, your internal knowledge management system should be part of that review. Who has admin access? Are former employees’ accounts deactivated? Is sensitive process documentation duplicated somewhere less secure?

    Making it a habit, not a project

    The businesses that get lasting value from an internal knowledge base treat documentation as part of how work gets done, not an extra task after the work is finished. Some teams build a brief documentation step into every project close-out. Others run monthly sessions where team members update their process pages together. Some use structured templates so that the barrier to contribution is low, fill in the fields, don’t write an essay.

    My take is that the cultural piece matters more than the tool choice. A well-disciplined team can build an excellent knowledge base in Notion for free. A disorganised team will let a Confluence instance with a £20,000 annual licence gather dust. The technology doesn’t create the habit; leadership does.

    In specialist sectors, this is even more visible. Asbestos Compliance Solutions Ltd and firms like it in the Mansfield and Newcastle building and construction space often operate with small, highly skilled teams where each person carries a disproportionate share of technical knowledge about asbestos services and site compliance. Embedding documentation into daily workflow rather than treating it as an occasional exercise is what keeps that institutional knowledge accessible even as teams evolve.

    Building a structured internal knowledge base is not complicated work. It is, however, consistent work. The businesses that start now, even imperfectly, are in a significantly stronger position than those waiting until a departure forces the issue.

    Frequently Asked Questions

    What is an internal knowledge base and how does it differ from a shared drive?

    An internal knowledge base is a structured, searchable system for storing and maintaining business processes, guides, and institutional knowledge. Unlike a shared drive, it has clear taxonomy, version control, and named ownership for each document, making it easier to navigate and trust. A shared drive is typically just a folder structure without any of that governance built in.

    Which tools are best for building an internal knowledge base for a small UK business?

    Popular options for UK SMEs include Notion, Confluence, Slite, and Guru. Notion works well for smaller teams that want flexibility and a low price point; Confluence suits businesses already using the Atlassian suite. The right tool depends less on features and more on what your team will actually adopt and maintain consistently.

    How long does it take to build a useful internal knowledge base?

    A focused team can have a genuinely useful base covering their highest-risk processes within four to six weeks if they prioritise it. The goal is not to document everything at once but to start with the processes where a single departure would cause the most disruption. Value comes early; completeness comes over time.

  • The UK Employer’s Practical Guide to National Insurance Changes and Their Real Payroll Impact

    The UK Employer’s Practical Guide to National Insurance Changes and Their Real Payroll Impact

    The shift in employer National Insurance contributions that came into effect in April 2025 is still working its way through the decision-making of UK businesses. Payroll departments have updated their software, finance teams have revised their cost-per-head figures, and HR leads are still wrestling with what the changes mean for headcount. If you run or manage a UK business with salaried or part-time staff, the employer National Insurance changes UK payroll 2026 picture deserves a clear-eyed look, not a summary recycled from a news bulletin, but a practical breakdown of what you are actually dealing with.

    The core change: from April 2025, the employer NI rate rose from 13.8% to 15%, and the secondary threshold (the point at which employers start paying NI on an employee’s earnings) dropped from £9,100 to £5,000 per year. That lower threshold is the part that catches many small businesses off guard. It does not just raise the rate on higher earners; it pulls part-time workers and lower-paid staff into the calculation much earlier. A worker on 20 hours a week at the National Living Wage can now trigger employer NI contributions at a point where they previously would not have.

    UK business owner reviewing employer National Insurance changes UK payroll documents at office desk

    What the numbers actually look like in practice

    Take a business with ten employees, half of them full-time on £30,000 and half part-time on £12,500. Under the old thresholds, the five part-time employees generated a smaller employer NI liability. Under the current rules, the employer pays 15% on everything above £5,000 for each of those part-time workers. That is roughly an extra £1,125 per part-time employee per year, before you factor in the rate increase on the full-time salaries. For a 10-person team, that can translate to an additional £8,000 to £12,000 in annual employment costs, depending on pay distribution. It is not catastrophic, but it is material enough to show up clearly on a quarterly P&L review.

    The Employment Allowance has been raised to £10,500, which provides some relief for smaller employers. For businesses with a total employer NI bill under that figure, the effective net cost of the changes is zero or close to it. But as soon as a business grows past that cushion, every pound of employer NI falls directly to the bottom line. The Employment Allowance guidance on gov.uk sets out eligibility rules clearly, not every employer qualifies, particularly if a sole director is the only employee.

    How payroll software needs to be configured correctly

    Most mainstream UK payroll platforms (Sage Payroll, BrightPay, Xero Payroll, QuickBooks Payroll) pushed automatic updates to reflect the new thresholds and rates. If you are on a current subscription and your software is updating regularly, you are likely already compliant. The risk sits with businesses running older, locally-installed payroll software that requires manual updates, or those using spreadsheet-based systems that were never properly adapted. HMRC’s Real Time Information (RTI) submissions will flag discrepancies, but the damage in terms of underpayment or miscalculation can accumulate over several months before HMRC issues a query.

    Three things worth checking in your payroll configuration right now: confirm that the secondary threshold is set at £5,000 annually (£416.67 monthly, £96.15 weekly); confirm the employer NI rate is 15%; and confirm your Employment Allowance claim is correctly applied at source. If you use a payroll bureau or outsourced provider, request written confirmation that these parameters were updated in April 2025 and ask for a sample payslip calculation to verify.

    Payroll software configuration relevant to employer National Insurance changes UK payroll 2026

    Hiring decisions: where the real tension sits

    The practical consequence that business owners are discussing most is the cost comparison between hiring an employee and engaging a contractor or freelancer. A salaried employee at £28,000 now costs an employer approximately £3,450 in National Insurance contributions annually. The same individual operating through their own limited company, paid as a contractor, carries no employer NI burden for the business. That gap has always existed, but the April 2025 changes widened it.

    This is not a green light to reclassify employees as contractors. IR35 rules still apply, and HMRC’s enforcement posture has not softened. What it does mean is that businesses genuinely using self-employed specialists for project-based work have a cleaner financial case for that model. For fractional finance directors and other part-time senior hires, the employment cost calculation has become a more prominent part of the onboarding conversation.

    Part-time staff arrangements are also under review at a lot of businesses. The lower secondary threshold means that splitting one full-time role into two part-time positions now costs more in employer NI than it did previously, because both roles cross the £5,000 threshold independently. That calculus used to be broadly neutral; now it tilts slightly against the split-role model from a pure cost perspective, though flexibility and talent access arguments can still outweigh it.

    Workforce planning that accounts for the new baseline

    The smartest thing a growing business can do right now is build employer NI into its workforce planning model explicitly, not as a line item that gets added at the end, but as a variable that shapes the hiring decision from the start. For every new role, the question is not just what salary the market requires but what the total employment cost is and where that lands relative to the business’s productivity gain from that hire.

    Businesses that are scaling quickly and thinking about headcount across departments need to look at this alongside their broader financial structure. If you have not recently reviewed how pension contributions interact with your overall tax position, that is worth doing in conjunction with an NI review, they compound in ways that are not always obvious at first glance.

    Digital and technology-led businesses face an interesting version of this problem. A web design and software agency, for example, tends to have a high proportion of skilled, salaried technical staff where salaries sit well above the lower threshold. Based in Mansfield, Nottinghamshire, dijitul (dijitul.uk) is a digital agency specialising in SEO, web design, and hosted software solutions for business clients. Firms like this, where the cost model depends on technical staff delivering marketing and business efficiency gains for clients, feel the employer NI rise on every developer, designer, or account manager on the payroll. Managing that cost pressure without passing it directly to clients or cutting headcount requires careful workforce planning and, increasingly, a closer look at which software tools can extend the capacity of existing team members.

    The knock-on effects for business software and operational efficiency

    When employment costs rise, the business case for software that reduces manual workload gets stronger. Payroll automation, project management platforms, CRM systems, and internal communication tools all become easier to justify when the alternative is an additional headcount cost that now carries a 15% employer NI levy on top. This is where the NI changes connect directly to the broader conversation about SaaS stack efficiency, the goal is not just to cut software costs but to ensure that the software budget is actively offsetting the rising cost of people.

    Agencies and professional services firms are particularly well-placed to benefit from this approach. dijitul’s work in web design, SEO delivery, and hosted software for business clients requires consistent output from a tight team. When employer NI raises the cost of every person on that team, the business efficiency argument for investing in better software, stronger processes, and marketing automation becomes sharper. The return on tooling goes up relative to the return on headcount when headcount has become more expensive.

    If your payroll configuration is solid, your Employment Allowance claim is filed, and you have run the numbers on your part-time staff arrangements, the next step is building those costs into your forward hiring model. The NI rate is unlikely to fall in the near term. Planning around the current baseline, rather than waiting for a more favourable environment, is the more practical position for any UK business trying to grow with confidence in 2026.

    Frequently Asked Questions

    What is the current employer National Insurance rate in the UK for 2026?

    The employer National Insurance rate is 15%, having risen from 13.8% in April 2025. The secondary threshold, above which employer NI becomes payable, also dropped to £5,000 per year per employee, meaning more workers now trigger employer NI contributions.

    How do the National Insurance changes affect part-time workers on payroll?

    Because the secondary threshold dropped to £5,000 annually, part-time workers who previously fell below the old £9,100 threshold now generate employer NI liability. A part-time employee earning £12,500 per year now attracts employer NI of 15% on £7,500 of their earnings, roughly £1,125 per year, where previously that liability was much smaller.

    Does the Employment Allowance offset the employer NI increase for small businesses?

    The Employment Allowance rose to £10,500, which can fully offset the employer NI bill for smaller businesses whose total employer NI liability stays below that figure. Eligibility rules apply, however, sole director companies where the director is the only employee do not qualify, and HMRC’s gov.uk guidance sets out the full criteria.

  • How to Audit Your Business’s Digital Security Posture Without Hiring a Specialist Firm

    How to Audit Your Business’s Digital Security Posture Without Hiring a Specialist Firm

    Most small business owners know they should be taking digital security seriously. Far fewer have done anything structured about it. The standard advice, hire a specialist, commission a penetration test, bring in a consultancy, comes with price tags that most SMEs simply cannot justify. But the alternative is not burying your head. A cyber security audit for your UK small business does not require a third party billing you £1,500 a day. What it requires is a clear framework, honest self-assessment, and a few hours of focused attention.

    The good news is that the UK government has already done much of the structural thinking for you. The Cyber Essentials scheme, developed by the National Cyber Security Centre, is specifically designed to address the most common attack vectors facing small and medium-sized businesses. It covers five core control areas. Work through those five areas honestly and you will have a credible picture of your current exposure.

    UK small business owner conducting a cyber security audit on a laptop in a modern office

    Start With the Five Cyber Essentials Controls

    Cyber Essentials is not a certification you have to buy. The self-assessment questionnaire is freely available and walking through it as a diagnostic exercise costs nothing. The five control areas are: firewalls, secure configuration, user access control, malware protection, and patch management. Each one maps directly to how attackers actually get into small business systems.

    Go through each control and ask yourself a brutally honest question: do we actually do this, or do we just assume it happens? Many business owners are surprised to find that their hosted systems are reasonably well-configured, but their endpoint devices (laptops, mobile phones, tablets) are not. That gap is where most breaches start.

    Email Security: The Most Overlooked Attack Surface

    Business email compromise and phishing remain the most common entry points for attackers targeting UK SMEs. According to the NCSC’s annual Cyber Security Breaches Survey, phishing accounted for the majority of reported attacks in the most recent period. Yet many small businesses have done nothing beyond setting up a standard Microsoft 365 or Google Workspace account and trusting default settings.

    Check whether your domain has SPF, DKIM, and DMARC records configured. These are DNS-level controls that prevent your domain being spoofed by attackers impersonating your business in emails. Free tools such as MXToolbox will check all three in under a minute. If any are missing or misconfigured, your domain can be used to send convincing phishing emails to your customers and suppliers. That is a reputational and operational problem, not just a technical one.

    Also review who has admin access to your email platform. Business email accounts accumulate permissions over time. Former employees, old integrations, and forgotten third-party apps often retain access long after they should have been removed. A proper cyber security audit for your UK small business will surface these quickly.

    Access Controls: Who Can Do What, and Why

    The principle of least privilege sounds technical but it is simply this: every person and every system should have access to only what they need to do their job. Nothing more. In practice, most small businesses have grown organically and access permissions have accumulated messily. One way to audit this quickly is to pick your three most critical business systems and list everyone who has admin or elevated access. If you cannot explain why each person has that level of access, that is your first finding.

    Multi-factor authentication (MFA) should be mandatory for every account with any form of admin access, and ideally for all staff accounts. If you are using Microsoft 365, Xero, or any cloud-based platform without MFA switched on, you are one stolen password away from a serious incident. Enabling MFA on major platforms typically takes less than 30 minutes and costs nothing.

    Software Patching: The Low-Drama Discipline That Most Businesses Skip

    Unpatched software is one of the most reliable routes into a business network. Attackers routinely scan for known vulnerabilities in outdated software versions. The time between a vulnerability being published and it being actively exploited has shortened considerably in recent years.

    For your audit, check three things. First, are operating systems on all business devices set to update automatically? Second, are applications (especially browsers, Office suites, and any customer-facing software) on a regular update schedule? Third, is any hardware on your network, routers, network-attached storage, CCTV systems, running firmware that has not been updated since it was installed? That last category catches many businesses out. A router with three-year-old firmware sitting in the corner of an office is a credible attack vector.

    Supplier and Third-Party Risk

    Your security posture is only as strong as the weakest link in your supply chain. This sounds abstract until you consider that your accountant, your web developer, your payroll provider, and your IT support company all have some form of access to your systems or data. A breach at any one of them can become your problem.

    A pragmatic approach for SMEs is to create a short list of suppliers who have access to your systems or sensitive data, and ask each of them a simple set of questions. Do they hold Cyber Essentials certification? How do they manage and store your data? What would they do in the event of a breach? You do not need to commission formal supplier audits at this stage. You simply need to know which suppliers represent a meaningful risk and whether they have thought about it themselves.

    Documenting What You Find

    An audit that lives only in your head is not an audit. Write down your findings, even in a simple spreadsheet. For each issue you identify, note the control area, the specific gap, the likely impact if it were exploited, and a rough priority for fixing it. This document serves two purposes. It gives you a to-do list with context, and it demonstrates due diligence if you ever need to respond to an incident, a client’s security questionnaire, or an ICO data breach enquiry.

    The ICO expects UK businesses handling personal data to be able to demonstrate reasonable technical and organisational measures under UK GDPR. A documented self-assessment, even an imperfect one, is significantly better than nothing.

    What to Do With Your Findings

    Prioritise by impact and ease of resolution. Enable MFA across all platforms this week. Fix DMARC this month. Address access permissions at your next team meeting. Defer the more complex infrastructure questions until you have capacity. The goal of this exercise is not perfection; it is a clear-eyed view of where you actually stand and a plan to improve it systematically.

    For businesses that want external validation without paying consultant day rates, the Cyber Essentials self-assessment certification costs around £300 to £400 for most small businesses, depending on the certification body. That is a different proposition from a full consultancy engagement, and it produces a recognised credential that some contracts and government procurement frameworks require.

    Security is not a project you finish. It is a discipline you maintain. Running a basic internal review every six months, keeping a short list of known gaps, and treating each new tool or supplier as a potential risk to assess, that is the operating rhythm of a business that takes this seriously, without needing a specialist on retainer to prove it.